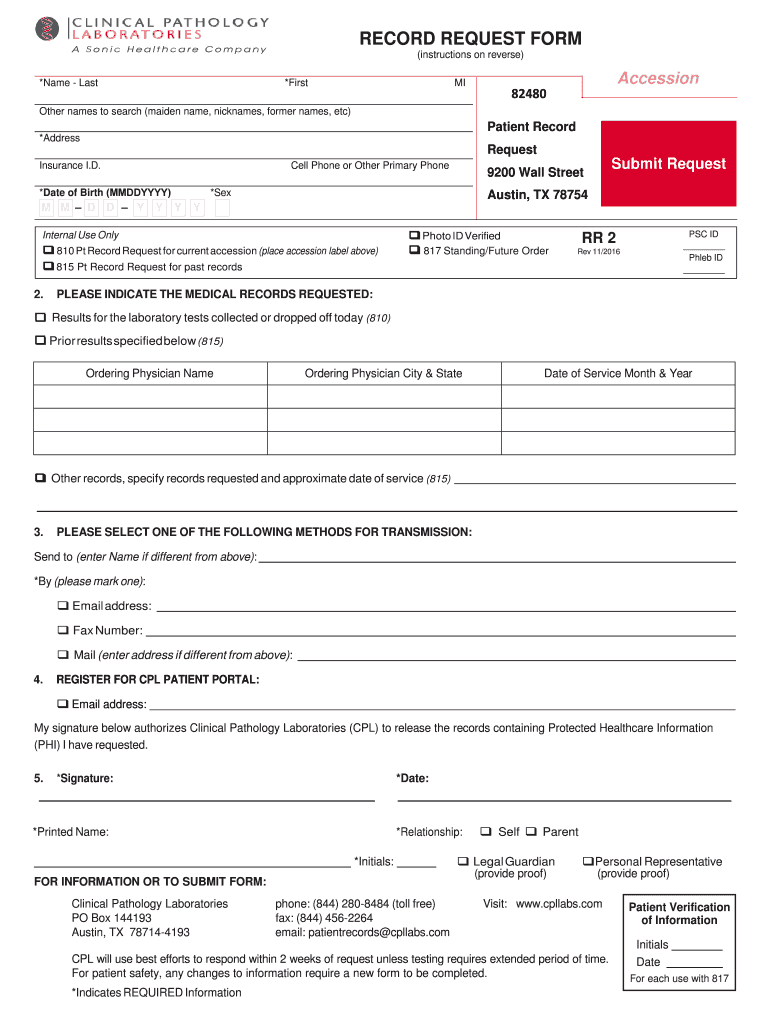
Instructions For Record Request Form Clinical Pathology Laboratories
Use a Instructions For Record Request Form Clinical Pathology Laboratories template to make your document workflow more streamlined.
What this pathology request form does
The Instructions For Record Request Form Clinical Pathology Laboratories is a healthcare authorization and routing document used to identify a patient, requester, requested laboratory records, and permitted recipient. Staff complete the relevant fields, confirm authorization and disclosure limits, obtain the required signature, and send the request for laboratory review. In a signNow workflow, the laboratory uploads the form, places fields over the existing document, sends it to the authorized signer, and stores the completed record with its audit trail. HIPAA safeguards apply when protected health information is involved.
Who uses this request form
Clinical laboratories
Laboratory staff use patient identifiers, requester details, record categories, authorization dates, and recipient information to process disclosure requests consistently and document the basis for releasing clinical pathology records.
Authorized requesters
Healthcare providers, attorneys, patients, and authorized representatives use the completed form to request specified pathology reports, establish permitted disclosure, and return a signed authorization for laboratory review.
Business types using the request form
Clinical pathology organizations use this form to identify requesters, define records, capture authorization, and document disclosure handling.
Independent pathology laboratories use the form to document patient-authorized requests, identify the requester, specify records needed, and route completed authorizations for secure review. Regional hospital systems use it to standardize medical-record disclosures across departments, capture patient consent, and preserve an auditable record of each laboratory-information request. Enterprise laboratory networks use reusable templates, role-based access, and centralized audit trails to coordinate high-volume requests while applying HIPAA safeguards to protected health information.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for pathology record requests
signNow combines field placement, signer routing, audit evidence, and controlled storage for the specific patient-record request workflow.
Field placement
Place fields directly over patient identifiers, requested report types, authorization language, signatures, and dates without recreating the laboratory’s approved form.
Signer routing
Route the request to the authorized patient or representative, while keeping recipient and laboratory review roles distinct in the signing order.
Audit trail
Capture timestamps, signer actions, and completion history so staff can evidence how the pathology request was completed and returned.
Reusable template
Reuse an approved request template for recurring laboratory disclosures while preserving request-specific patient and authorization information.
Mobile signing
Collect signatures from desktop or mobile devices when the authorized signer cannot attend the laboratory in person.
Record storage
Connect completed requests with Google Drive, Box, Egnyte, or Microsoft 365 for controlled document storage and retrieval.
How the signNow workflow works
The form moves from laboratory document preparation to authenticated completion, with each action recorded for later review.
Upload form: Upload the laboratory’s approved request document. Detect fields: Place fields over patient and authorization sections. Route signer: Send to the authorized signer by email. Preserve evidence: Store the signed request with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete the request
Prepare the laboratory’s approved document, complete its identifiers and authorization details, then route it through signNow for signature and documented retention.
Upload form:
Upload the approved laboratory request PDF. Add fields:
Place patient, requester, authorization, signature, and date fields. Set recipients:
Enter the authorized signer and recipient details. Check request:
Review identifiers, scope, and disclosure limits. Send request:
Send the form for completion and signature. Archive records:
Download the signed form and audit trail.
What the audit trail records
The audit trail supplements the signed pathology request with technical evidence about identity, timing, document integrity, and completion.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Record actions:
Retrieve evidence:



Security for pathology requests
AES-256 at rest:
TLS 1.2/1.3 in transit:
HIPAA compliant with BAA:
SOC 2 Type II certified:
ISO 27001 certified:
ESIGN and UETA compliant:
Privacy pitfalls to avoid
Patient identifiers can be entered inconsistently, causing laboratory staff to retrieve the wrong chart or delay processing while identity is confirmed. A request may name records broadly without specifying pathology reports, dates, recipients, or permitted uses, creating uncertainty about the authorized disclosure. Sending protected health information to an unverified recipient can expose data and undermine the laboratory’s HIPAA disclosure controls. Unsigned authorization pages, missing dates, or incomplete representative information can prevent the laboratory from validating the request before release.
Retention periods by record class
Apply the retention rule that matches the underlying record, rather than assigning one period to every pathology request.
Six years — HIPAA records
Three years — tax records
Three years — I-9 records
Five years — OSHA injuries
Thirty years — OSHA exposure
Record-keeping practices for requests
Retention, export, access control, and version history help laboratories preserve a defensible record of each pathology disclosure request.
Apply the correct retention rule
Export the audit trail
Control template changes
Preserve request history
Legal standing of signed requests
For a U.S. business transaction, an electronic pathology request can be evidence when the signer demonstrates intent, consents to electronic records, can be attributed to the signature, and the record remains reproducible. ESIGN and applicable state law support this framework; HIPAA obligations still govern protected health information.

Troubleshooting request workflows
Use these checks when a clinical pathology request is incomplete, misrouted, or difficult to evidence.
Upload the laboratory request PDF again and use signNow’s field placement tools to mark patient, requester, authorization, signature, and date fields. The Business plan includes templates and audit trails, so staff can reuse the corrected layout without changing the underlying request language.
Check that the signer’s email matches the authorized patient or representative identified in the request. signNow can add SMS authentication, while HIPAA workflows require an appropriate business associate agreement and safeguards for protected health information.
Review the patient name, date of birth, medical-record number, requested report types, recipient, and authorization dates before sending. A corrected request should be completed as a new version and linked to the original audit trail for traceability.
Use a signNow template containing the laboratory’s approved request fields, then restrict editing to designated staff. HIPAA compliance is available with a BAA; organizational privacy policies still determine who may access or disclose records.
The Business plan provides audit trails and templates. Business Premium adds bulk send, but use bulk workflows only when each request remains individually authorized, correctly addressed, and separated from other patients’ protected health information.
Export the completed form and audit trail from signNow, then retain them under the laboratory’s applicable policy. HIPAA-covered entities must retain required documentation for six years from creation or the last effective date under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.