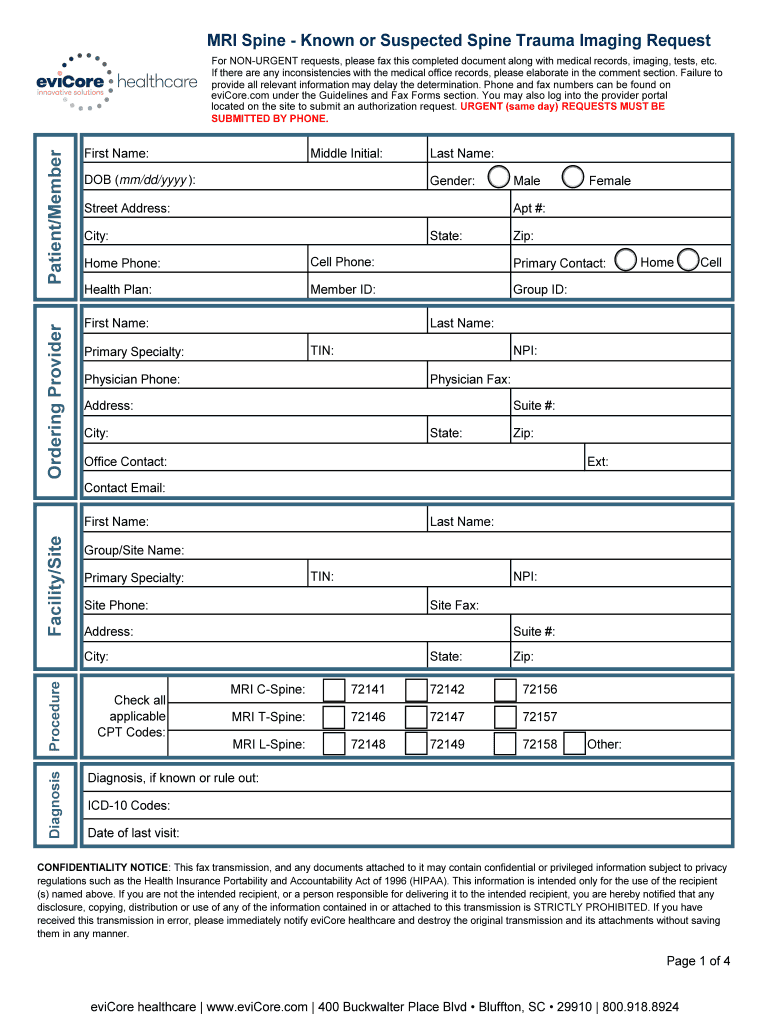
Mri And Ct Head And Mri Spine Imaging Request M Evicore Com Form
Use a MRI And CT Head And MRI Spine Imaging Request M Evicore com template to make your document workflow more streamlined.
What this imaging request form does
This form records the clinical and administrative information needed to request MRI or CT imaging of the head or spine through an eviCore-related authorization workflow. It can identify the patient, ordering provider, requested study, clinical indications, insurance details, and authorization information before review by the responsible payer or utilization-management team. With signNow, a sender uploads the PDF, reviews auto-detected fillable fields, assigns the appropriate signers, and sends the request electronically. Completed signatures, timestamps, delivery events, and the audit trail remain available with the final document for controlled recordkeeping.
How this imaging request works
The form moves from clinical information entry to authorized signatures, with signNow recording completion evidence for the request record.
Upload form: Upload the MRI and CT request PDF to signNow. Review fields: Review detected fields and add missing patient details. Assign signers: Assign physician, patient, and facility signing roles. Store record: Send, complete, and retain the signed request with its audit trail.
Complete the imaging request in signNow
Follow these steps to move the MRI or CT request from an uploaded PDF to an auditable completed record.
Upload form:
Upload the MRI and CT request PDF. Check fields:
Review auto-detected patient and provider fields. Assign roles:
Assign required clinical and administrative signers. Send request:
Send the request through signNow. Archive evidence:
Download the completed form and audit trail.
Recommended workflow configuration
Configure this imaging request around verified signer identity, protected health information safeguards, complete evidence, and the retention rule applicable to the organization.
| Setting | Recommendation |
|---|---|
| Authentication method | Email plus SMS verification |
| Signature type | Electronic signature with intent |
| Audit trail | Enabled for every completed request |
| Document retention | Six years under HIPAA 45 CFR §164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the signNow audit trail records
For this imaging request, the audit trail connects signer identity, document activity, and completion evidence without replacing the organization’s health-record retention policy.
Authenticate signer:
Capture timestamps:
Protect document integrity:
Seal record:
Record activity:
Export evidence:
Platform requirements for this form
Use a current Chrome, Firefox, Safari, or Edge browser on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing authorized staff to review and sign the imaging request away from a workstation.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android signNow apps
Healthcare organizations should deploy the form on managed devices, restrict access to authorized personnel, and configure account controls appropriate for protected health information. Enterprise deployments may also evaluate API access, SSO provisioning, and retention or certificate settings against internal HIPAA policies and payer requirements.



Security for protected imaging data
Transport encryption:
Storage encryption:
Healthcare compliance:
Security assurance:
Information security:
Signature legality:
Best practices for accurate requests
Accurate identifiers, defined signer roles, protected communications, and complete evidence handling reduce rework when this imaging request moves between clinical and administrative teams.
Verify clinical identifiers before sending
Assign each signer a clear role
Limit protected health information exposure
Archive the signed request evidence
Processing stages for imaging requests
No universal payer turnaround is stated for this form; signNow provides a controlled sequence from preparation through signer completion and archival.
Prepare the request
Deliver to signers
Complete signer review
Complete and archive
Privacy pitfalls for imaging requests
Including diagnosis details in an email subject exposes protected health information before the MRI or CT request reaches its authorized recipient. Using one shared signNow account for physicians and staff prevents reliable attribution of who approved the imaging request. Sending the request without electronic-record consent disclosures may weaken evidence that a patient agreed to receive and sign electronically. Leaving completed imaging requests in personal downloads folders creates uncontrolled copies outside the organization’s retention and access policies.
Troubleshooting the imaging request form
Resolve field detection, signer access, patient-consent, privacy, and audit-trail issues before submitting this imaging request.
If signNow does not detect fields, upload the original PDF again and review auto-detected fields. The Business plan supports templates and audit trails; manually add missing signer, date, or authorization fields before sending. HIPAA workflows require a business associate agreement when protected health information is involved.
The Business plan costs $8 per user per month with annual billing and includes 100 signature invites per user annually. Business Premium costs $15 and includes bulk send. If this request exceeds the included invite allocation, review overage terms or consider the Site License before sending.
Use signNow SMS authentication or another configured verification method before releasing the imaging request. HIPAA compliance requires a business associate agreement, appropriate access controls, and safeguards for protected health information; the signature platform alone does not determine whether the full workflow complies.
A signer can open the request from the email invitation or a signNow signing link without creating an account when the sender permits guest signing. Confirm the recipient address, resend the invitation, and avoid placing diagnosis details in the email subject or message.
If the completed request appears altered, download the signed PDF and its certificate of completion from signNow. The audit trail records signer actions, timestamps, and delivery activity. Preserve both files together so the record can be reviewed under ESIGN and UETA evidence requirements.
A patient’s electronic consent must show intent, consent to electronic records, and access to the retained record. For consumer-facing healthcare records, ESIGN 15 U.S.C. §7001(c) also requires paper-right disclosure and withdrawal procedures. Configure disclosures before requesting the signature.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.