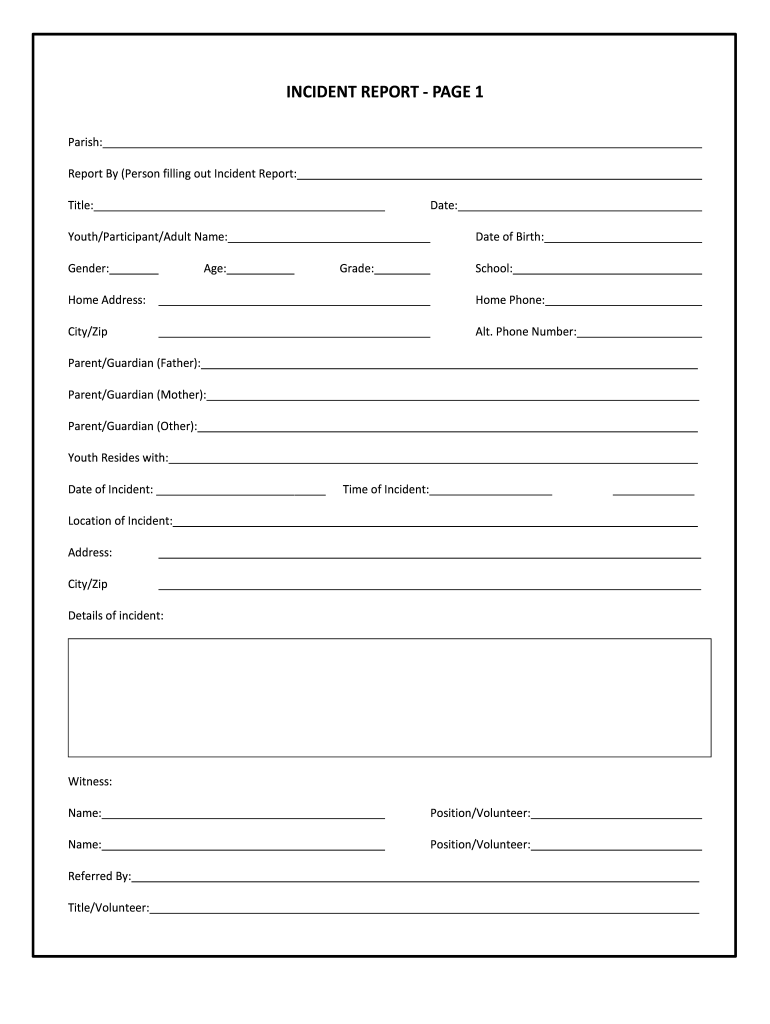
Incident Report Page 1 Form
Use a INCIDENT REPORT PAGE 1 template to make your document workflow more streamlined.
What the incident report form records
An Incident Report Page 1 Form records what happened, when and where it happened, who was involved, witness details, immediate actions, and required acknowledgments. It is an internal business record rather than a single federally issued form with one nationwide filing deadline. A supervisor or designated reviewer can check the entries, add signatures, and preserve the completed report. With signNow, upload the source document, review automatically detected fillable fields, send it to named recipients, and store the signed PDF with its audit trail.
Business types using incident reports
Incident Report Page 1 Form is useful wherever a documented event requires review, acknowledgment, signatures, and controlled retention.
Solo practitioners can document workplace, client-site, or property incidents, then send the completed report to witnesses or responsible managers without arranging an office meeting. Construction and healthcare teams can collect incident details from field personnel, route acknowledgments to supervisors, and preserve signed records for internal review. Enterprise compliance teams can standardize templates, permissions, audit trails, and storage connections across departments handling sensitive incident documentation.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for incident report handling
Incident Report Page 1 Form workflows combine structured data capture, signer routing, audit evidence, and controlled storage for workplace, construction, healthcare, and insurance records.
Structured reporting
Capture the incident narrative, dates, locations, witnesses, and corrective actions in one structured record that can be reviewed before signatures are requested.
Field detection
Upload a prepared Incident Report Page 1 Form and review automatically detected fields before adding missing text, date, initials, or signature fields.
Signer routing
Route the report to identified recipients in a defined signing order, reducing uncertainty about who must review or acknowledge each incident detail.
Audit trail
Retain the signed report with an audit trail that records signing activity, timestamps, and document history for internal investigations or compliance review.
Mobile access
Use signNow mobile apps to review or sign incident documentation from a phone or tablet when supervisors are away from the office.
System connections
Connect completed reports with named systems such as Google Drive, Box, Salesforce, or NetSuite when the organization requires centralized record handling.
Complete an incident report online
Use this sequence to prepare, sign, distribute, and retain an Incident Report Page 1 Form in signNow.
Upload form:
Upload the completed source file. Check fields:
Review detected fields and labels. Add signers:
Add recipients and signing order. Send report:
Send the incident report securely. Archive records:
Store the signed PDF and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended incident report setup
Configure the Incident Report Page 1 Form around signer identity, evidence preservation, access control, and the organization’s applicable retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Follow employer and state policy |
| Encryption | TLS 1.2/1.3 and AES-256 protection from signNow |
Review the incident report audit trail
The audit trail records signer activity and document history separately from the visible Incident Report Page 1 Form, supporting later review and retention.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Verify completion:
Export evidence:
Security controls for incident reports
Data encryption:
Security certification:
Information security:
Healthcare compliance:
Privacy compliance:
Signature compliance:



Best practices for incident reports
Accurate fields, controlled access, complete audit evidence, and policy-based retention make Incident Report Page 1 Form records easier to review and defend.
Standardize incident fields before sending
Review facts before requesting signatures
Preserve the report and audit trail
Restrict access to sensitive details
Privacy challenges in incident reports
Incident descriptions may expose employee names, medical details, witness statements, or location data to recipients who do not need full access. A report can be signed before a supervisor verifies dates, attachments, corrective actions, or the identity of each person involved. Using a shared signing link without appropriate authentication can make it harder to attribute an acknowledgment to the intended signer. Keeping the signed PDF without its audit trail can weaken the record’s ability to show who acted, when, and through which workflow.
Troubleshooting incident report workflows
Resolve field detection, signer delivery, authentication, compliance, and plan-limit questions before distributing an Incident Report Page 1 Form.
Upload the source file again and confirm that the page is readable. signNow can detect fillable areas after upload, but unclear scans may require manually placing text, date, and signature fields before sending.
Check the recipient email address, spam folder, and signing link. If delivery still fails, resend the Incident Report Page 1 Form from signNow after confirming the signer’s contact information and access permissions.
Business includes legally binding eSignatures, templates, mobile apps, and audit trails at $8 per user monthly when billed annually. Business Premium adds bulk send and kiosk mode at $15 per user monthly.
Use stronger signer authentication when incident details contain protected health information. signNow states that HIPAA compliance requires a business associate agreement, so confirm the BAA before processing PHI.
A typed or drawn signature can be supported by intent, attribution, consent, and retained records under ESIGN and UETA. Keep the completed document and audit trail together for later review.
Business plans include 100 signature invites per user per year, with overage fees. If your incident-report volume exceeds that allowance, review Business Premium, Enterprise, or the Site License before deployment.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.