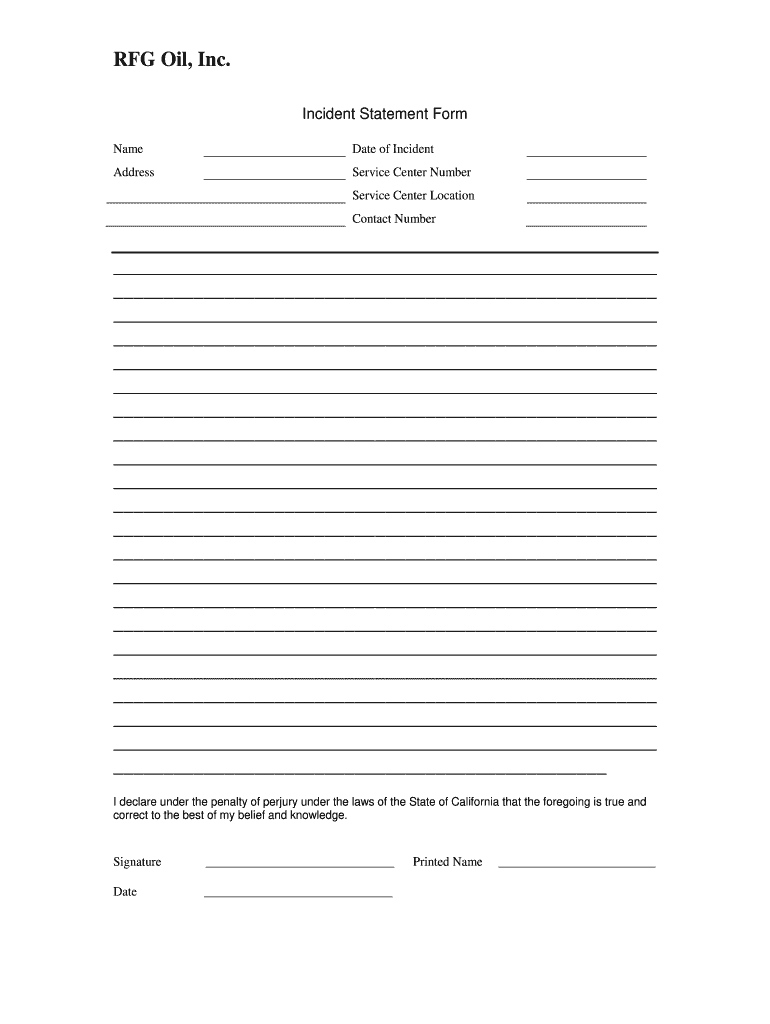
Incident Statement Form
Use a Incident Statement Template template to make your document workflow more streamlined.
What is an Incident Statement Form?
An Incident Statement Form records what happened during a workplace, customer, property, or operational incident. It typically captures the incident date and time, location, people involved, factual narrative, witnesses, and supporting details so an organization can review the event consistently. With signNow, a sender uploads the form, auto-detects fillable fields, assigns fields to the reporting person and reviewer, sends it for completion and signature, and stores the completed record with an audit trail. Electronic execution may be supported under ESIGN and applicable state law when intent, consent, attribution, and record retention requirements are met.
Who benefits from structured incident reporting?
Incident Statement Form supports consistent fact gathering, review, signature collection, and controlled recordkeeping across several U.S. business settings.
A small construction contractor uses the form to document jobsite injuries, equipment damage, witness accounts, and supervisor review before records enter its safety file. A healthcare clinic uses the form for patient-area incidents, employee observations, corrective actions, and authorized review while limiting access to protected information. A multi-site enterprise uses shared templates and role-based routing to standardize incident reporting across offices, contractors, and regional compliance teams.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How an Incident Statement Form works
The workflow moves from factual reporting to assigned review, signature collection, and preservation of the completed incident record.
Prepare: Upload the incident template and let signNow detect fillable fields. Route: Assign narrative, acknowledgment, and signature fields to recipients. Deliver: Send the form by email or signing link. Preserve: Complete, review, and store the signed record with its audit trail.
How to complete the form online
Use this workflow to capture the incident narrative, obtain required signatures, and preserve a reviewable record.
Upload form:
Upload the Incident Statement Form and review the detected fields. Assign roles:
Assign reporter, witness, supervisor, and reviewer fields. Set recipients:
Add email recipients or create a signing link. Send form:
Send the form and monitor completion status. Store record:
Review signatures, download the record, and preserve its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features that support incident reporting
signNow connects form preparation, role-based signing, audit evidence, and controlled storage for Incident Statement Form workflows.
Field detection
Upload an Incident Statement Form and use detected fields to prepare dates, narratives, acknowledgments, signatures, and reviewer assignments without rebuilding the document manually.
Role routing
Route the report to the person who observed the incident, witnesses, supervisors, or compliance reviewers in a defined sequence.
Audit trail
Capture invitations, access, timestamps, signing events, and completion status alongside the signed incident record.
Flexible signing
Use email delivery or signing links when an incident participant needs to complete the form without creating a signNow account.
Mobile access
Review and sign from signNow mobile apps when supervisors or field personnel are away from a desk.
Data protection
Protect incident records with encryption, access controls, and compliance capabilities selected for the organization’s data obligations.
Security for incident records
Data encryption:
Security reporting:
Security standard:
Healthcare protection:
Privacy frameworks:
Electronic signatures:
Privacy and disclosure pitfalls
Including medical details, employee identifiers, or witness contact information without limiting access can expose personal data beyond the incident review team. A reporter may sign without seeing a required consent or acknowledgment statement, weakening evidence that the person understood the electronic transaction. Sending a report to the wrong email address can disclose the incident narrative, attachments, and signatures to an unauthorized recipient. Changing the incident narrative after signature without preserving the original record can create uncertainty about what the signer actually reviewed.
Best practices for incident statements
A reliable Incident Statement Form workflow protects factual accuracy, signer attribution, privacy, and the integrity of the completed record.
Separate facts from conclusions
Assign every field carefully
Control supporting attachments
Preserve the signed record
What the audit trail records
The signNow audit trail adds evidence around the Incident Statement Form’s delivery, access, signing, and completion events without replacing the organization’s retention policy.
Authenticate signer:
Capture timestamps:
Track document:
Seal record:
Log activity:
Export evidence:



Incident Statement Form troubleshooting
These answers address field assignment, signatures, audit evidence, plan limits, and handling of sensitive incident information.
Check that every assigned field has a recipient, confirm the recipient email address, and resend the packet from signNow. An unassigned incident date, narrative, or signature field can prevent completion even when the document opens correctly.
Open the signNow Audit Trail and verify the invitation, access, viewed, completed, and signed events. The audit trail records timestamps, IP information, and action history, helping the organization identify where the reporting workflow stopped.
Business includes legally binding eSignatures, templates, and audit trails at $8/user/month when billed annually. It does not include bulk send; Business Premium is the plan identified as adding that feature.
For patient-related incident reports, signNow is HIPAA compliant when a BAA is required and properly established. Limit report access, collect only necessary information, and confirm the clinic’s own HIPAA policies before deployment.
Electronic execution generally requires intent, consent, attribution, and retention or reproduction of the record. ESIGN and applicable state law, including UETA or New York ESRA, govern the legal analysis; a platform alone does not decide enforceability.
Use signNow’s role assignments, authentication options, and audit trail rather than sending a completed report through unrestricted email. For sensitive records, administrators should define access, retention, and escalation rules before inviting a signer.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.