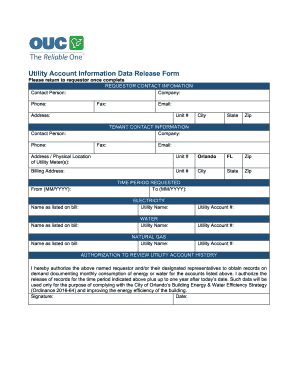
Authorization For Release Of Information Historical Customer Usage
Use a Authorization For Release Of Information Historical Customer Usage template to make your document workflow more streamlined.
What this release authorization does
An Authorization For Release Of Information Historical Customer Usage gives a named recipient permission to receive specified past customer-usage information. It should identify the customer, information covered, purpose, recipient, effective period, and signer. A sender prepares the document, confirms that the requested disclosure matches the authorization, and obtains the signer’s consent. With signNow, the document can be uploaded, fields reviewed, sent for signature, completed electronically, and stored with an audit trail. HIPAA-covered information requires separate privacy controls and a business associate agreement where applicable.
Legal standing of this authorization
This authorization can support an electronically signed release when the signer shows intent, consents to electronic records, can be attributed to the signature, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and UETA generally recognize that framework, but exclusions include wills, court orders, and family law decrees.

How teams manage authorization access
Healthcare records administrators use shared templates to standardize the authorization’s recipient, scope, purpose, and expiration fields. SignNow administrator controls can restrict who sends or accesses completed records, while delegated sending helps authorized staff issue forms without changing the underlying template or disclosure language. Customer operations teams can maintain a controlled authorization template and route signing tasks to designated staff. Role-based access, audit trails, and shared document workflows help separate preparation, sending, and records review when historical usage contains personal, financial, or health-related information.
How this release authorization works
The signNow workflow turns the authorization into a controlled electronic record while keeping the permitted information scope and recipient details visible to reviewers.
Upload: Upload the release authorization Prepare: Review detected fields and add missing consent fields Send: Send to the named signer by email or link Archive: Complete, store, and review the audit trail
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the signNow audit trail records
The audit trail documents the authorization event separately from the form’s business terms, creating a reviewable record of identity, timing, actions, and access.
Authenticate signer:
Capture timestamps:
Protect document:
Seal evidence:
Retrieve audit trail:
Control access:
Recommended authorization workflow setup
Configure the release authorization around signer identity, documented consent, controlled access, and retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Use verified email with role-based administrator access |
| Signature type | Use typed or drawn electronic signatures |
| Audit trail | Retain the completed audit trail with authorization |
| Document retention | Apply six years for HIPAA records |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
Security controls for release authorizations
Transport encryption:
Stored data:
Security certification:
Security management:
Health data:
Signature compliance:
Mobile options for release authorizations
Complete this authorization on iOS 15 or later and Android 10 or later through the signNow mobile apps, with TLS-protected browser and app connections.
iOS app iOS 15 or later signNow app Android app Android 10 or later signNow app Mobile tools Offline signing and camera capture
Managed mobile devices can support offline signing and camera-based document capture when staff need to prepare a customer usage authorization away from a desktop. Administrators should verify device controls, app permissions, identity checks, and storage policies before collecting personal information or health-related records.



Privacy challenges to address
Including historical usage details beyond the authorized scope can create an unnecessary disclosure of personal or health information. Missing signer identity, consent language, or effective dates can weaken the record’s evidentiary value during a later dispute. Sharing a completed authorization through uncontrolled email or storage can expose customer information to unauthorized recipients. Using one broad authorization for unrelated purposes can make the requested disclosure unclear and difficult to audit.
State and document exclusions
Notarization requirement
Wills and codicils
Court orders
State law
Troubleshooting release authorizations
These answers address field detection, signer access, plan limits, privacy controls, and electronic-signature requirements for this authorization.
Check that the authorization file is readable and that signNow can identify its fillable fields. On the Business plan, upload the document, review detected fields, and add any missing signer, date, or consent fields manually before sending.
A signer can open the request through the email link without creating a signNow account in many workflows. If stronger attribution is required, use SMS authentication or another available signer-authentication control and preserve the resulting audit trail with the completed authorization.
Business includes legally binding eSignatures, templates, and audit trails at $8/user/month when billed annually. Business Premium is $15/user/month annually and adds bulk send, while Enterprise is $30/user/month annually and adds advanced signer authentication.
For patient information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm that the organization has the required BAA and configure access, retention, and disclosure procedures separately from the electronic signature workflow.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. Consumer-facing records also require the disclosures in 15 U.S.C. §7001(c), including access and paper-record rights.
The Business plan includes 100 signature invites per user per year, with overage fees. Business Premium adds bulk send, and Site License pricing is $1.50 per signature invite for organizations processing 1,000 or more documents annually.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.