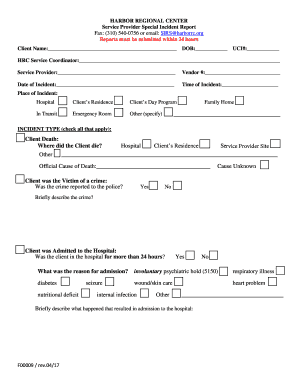
Service Provider Special Incident Report Form
Use a Service Provider Special Incident Report template to make your document workflow more streamlined.
What this incident report form does
A Service Provider Special Incident Report Form records an event involving a service provider, the relevant facts, the response, and required acknowledgments in one controlled document. The completed report gives authorized reviewers a consistent record of what happened and which actions followed. With signNow, a sender uploads the form, uses the editor to place or detect fillable fields, assigns recipients, and sends signature requests. Signers review and complete their assigned fields, while signNow records timestamps, signer actions, and the completed document for later retrieval.
Who uses this incident report
Service providers
Service providers and incident coordinators use the form to document an event, identify affected services, assign response actions, and obtain accountable review signatures. The form is suited to internal operations, vendor oversight, and regulated workflows when the organization defines the required fields and retention policy.
Review teams
Compliance, legal, privacy, and operations teams review completed reports, verify response ownership, and preserve the signed document with its audit trail. Healthcare organizations should apply HIPAA controls when the report contains protected health information.
How to complete the incident report
Follow these steps to prepare, route, sign, and retain the Service Provider Special Incident Report Form in signNow.
Upload form:
Upload the current Service Provider Special Incident Report Form. Check fields:
Review detected fields and add missing text, date, or signature fields. Assign recipients:
Assign each field to the correct service provider or reviewer. Send request:
Send the report through signNow and monitor completion status. Save records:
Download the signed report and its audit trail.
Recommended incident report setup
Configure the report around signer identity, evidence preservation, controlled access, and the organization’s documented retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Click-to-sign with intent |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Retain under incident-response policy |
| Encryption | AES-256 at rest and TLS 1.2/1.3 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Platform requirements for this form
Complete the Service Provider Special Incident Report Form through signNow in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow mobile apps support iOS and Android, while TLS 1.2/1.3 protects data in transit.
Browser access Chrome, Firefox, Safari, and Edge support browser-based report completion on Windows and macOS. Mobile apps The signNow mobile apps support report review and signing on iOS and Android devices. Secure access TLS 1.2/1.3 protects data in transit; use managed devices for sensitive reports.
Organizations handling sensitive incident information should use managed devices, role-based access, and approved storage procedures. Enterprise deployments can evaluate API access, SSO provisioning, and retention controls against internal security requirements before routing reports to service providers or reviewers.
What the signNow audit trail records
The audit trail links the Service Provider Special Incident Report Form to signer identity, timestamps, actions, completion status, and retrievable evidence.
Authenticate signer:
Capture timestamps:
Link document:
Preserve actions:
Retrieve evidence:
Export records:
Privacy pitfalls in incident reporting
Including names, medical details, or contact information in every recipient’s copy can expose personal data beyond the incident-response team. Sending before recording electronic-record consent can weaken evidence that the signer agreed to receive and sign the report electronically. Granting template-editing rights to every user can permit unauthorized changes to incident fields, instructions, or recipient routing. Storing completed reports in uncontrolled email attachments can make access reviews, retention decisions, and later retrieval difficult.
Best practices for incident reports
Use a controlled review, signing, access, and retention process so the completed incident report remains understandable and defensible.
Verify every incident detail before sending
Restrict report access by role
Preserve the report and audit trail
Document electronic-record consent
Legal standing of the completed report
A completed Service Provider Special Incident Report Form can support business evidence when the parties show intent, consent to electronic records, signer attribution, and reliable retention. ESIGN, 15 U.S.C. ch. 96, and UETA generally recognize qualifying electronic signatures, but they exclude wills, certain court filings, and family law decrees.

Processing stages for incident reports
Use internal response targets because no universal filing deadline is verified for this service-provider incident report.
Prepare the report
Deliver to signers
Collect signatures
Archive the record
State rules and document exclusions
State law varies
Excluded documents
Excluded documents
Acknowledgment required
Service Provider Special Incident Report Form troubleshooting
Resolve field, signer, consent, plan-limit, and privacy questions before distributing this incident report through signNow.
Use signNow's document editor to upload the Service Provider Special Incident Report Form, place fields, and send it for electronic signature. The Business plan includes templates, audit trails, and legally binding eSignatures; ESIGN and UETA provide the relevant U.S. framework.
If a signer cannot open the report, confirm the email address, resend the invitation, or create a quick invite link. signNow's Business Premium plan includes quick invite links, while mobile apps support signing from supported devices.
A missing incident detail should be corrected before sending. Edit the source document or template, upload the revised Service Provider Special Incident Report Form, and send a new request rather than altering a completed record.
For a consumer-facing report, electronic-record consent requires a clear paper-record disclosure and proof that the signer can access the electronic format under 15 U.S.C. §7001(c). Capture that consent before signature.
Business plans include 100 signature invites per user per year, with overage fees. If the report volume exceeds that allowance, review Business Premium, Enterprise, or Site License terms before sending additional invitations.
For health information included in an incident report, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm the BAA and your organization’s privacy controls before adding protected health information.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.