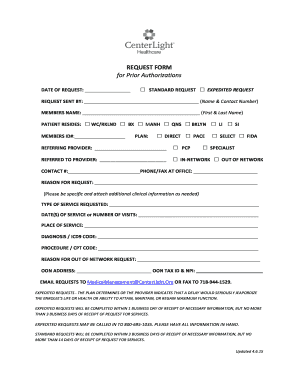
Request Form For Prior Authorizations Centerlight Health Centerlighthealthcare
Use a REQUEST FORM For Prior Authorizations CenterLight Health Centerlighthealthcare template to make your document workflow more streamlined.
What this prior authorization request does
Request Form For Prior Authorizations Centerlight Health Centerlighthealthcare is a healthcare document used to request payer approval before specified care, services, or supplies are provided. The requester completes patient, provider, insurance, diagnosis, service, and clinical-justification information, then obtains the required signatures and supporting documentation. With signNow, an authorized sender uploads the request, reviews detected fillable fields, routes it to the designated participants, and stores the completed file with an audit trail. The organization must still confirm payer-specific submission rules, required attachments, and applicable privacy procedures before sending.
Who completes the authorization request
Healthcare teams
Prior authorization specialists and clinicians use the request to collect patient identifiers, insurance details, diagnosis information, requested procedures, clinical justification, supporting records, and provider signatures before payer review.
Review participants
Patients, authorized representatives, payers, and utilization-review staff use the completed request to confirm consent, evaluate the requested service, and document the authorization decision or follow-up requirements.
Business types using prior authorization requests
The request is most useful where clinical documentation, payer review, and signatures must move together while preserving patient privacy and an accountable record.
Solo medical practices can prepare patient-specific authorization requests, obtain provider signatures, and preserve payer correspondence without passing paper between offices. Controlled templates reduce omitted diagnosis, service, and insurance details while keeping each request tied to its patient record and review process. Multi-site provider groups can route requests among clinicians, authorization specialists, and billing teams. Shared signNow templates standardize required fields, while role-based access and audit trails help administrators review who prepared, signed, or downloaded each authorization document. Health systems and managed-care organizations can connect authorization workflows with existing records, payer operations, and compliance controls. Enterprise teams can govern access, authentication, retention, and integrations for requests containing protected health information across departments.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to complete the prior authorization request
Complete this prior authorization request by checking required healthcare details, collecting signatures, and preserving the signed record for payer review.
Upload the form:
Upload the prior authorization request and review detected patient, provider, and service fields. Review the fields:
Correct missing information, then place signature, date, and approval fields. Add signers:
Add the payer, provider, or patient signers in the required sequence. Send for signature:
Send the authorization request and monitor completion from the signNow dashboard. Store the record:
Download the completed request with its audit trail for the medical record.
How the prior authorization workflow works
The workflow moves the prior authorization request from preparation through signature collection and documented storage without recreating the healthcare information each time.
Upload document: Upload the prior authorization request into signNow. Prepare fields: Detect and position fields for healthcare information and signatures. Invite signers: Invite authorized participants through email or a signing link. Complete and store: Collect signatures and retain the completed request with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the prior authorization audit trail records
The audit trail connects each prior authorization action to a signer, time, document state, and retrievable completion record.
Authenticate signer:
Timestamp actions:
Hash document:
Seal records:
Log activity:
Export evidence:
Recommended authorization workflow setup
Configure the request around verified signer identity, protected health information safeguards, complete audit evidence, and the applicable medical-record retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with intent evidence |
| Audit trail | Capture timestamps, IP, and document history |
| Retention and encryption | Six years for HIPAA records; AES-256 storage |
| User provisioning | Role-based access with managed users |
Key features for prior authorization requests
signNow helps healthcare teams prepare, route, sign, and preserve this prior authorization request while keeping the document-specific fields and evidence together.
Field detection
Upload the authorization request and review detected patient, payer, provider, service, and signature fields before routing it.
Signer routing
Route the request to clinicians, patients, representatives, or payer-side participants using defined signing order and recipient details.
Audit evidence
Capture timestamps, signer actions, document history, and completion evidence for the authorization record.
PHI safeguards
Protect patient information with TLS 1.2/1.3 in transit, AES-256 at rest, and HIPAA compliance when a BAA is required.
Reusable templates
Use templates for recurring authorization requests while preserving fields that change for each patient and requested service.
System integrations
Connect signed authorization records with approved storage or business systems such as Google Drive, Box, Salesforce, or Microsoft 365.



Platform requirements for prior authorization forms
Complete the prior authorization request in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, while TLS 1.2/1.3 protects data in transit.
Browser support Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, and Android Secure access TLS 1.2/1.3 and mobile apps
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices when requests contain protected health information. Confirm API, SSO, certificate, and retention requirements with the organization’s security and privacy teams before production deployment.
Security for prior authorization records
Transport encryption:
Storage encryption:
Healthcare compliance:
Independent assurance:
Security management:
Electronic records:
Best practices for prior authorization records
Accurate fields, controlled access, complete evidence, and documented retention help healthcare teams process this authorization request consistently and defensibly.
Verify every payer-required field before sending
Restrict access to protected health information
Export the audit trail with the completed request
Match retention to the record category
Retention periods for authorization records
Keep completed prior authorization requests according to the record category, applicable healthcare rules, payer policy, and any state requirements governing the patient record.
Six years for HIPAA records
Three years for tax records
Six years for major understatement
State period may be longer
Policy-controlled preservation
Privacy pitfalls in authorization requests
Patient identifiers or insurance member numbers can be exposed when a completed request is sent to an incorrect email address or downloaded onto an unmanaged device. A patient or representative may sign without documented electronic consent, creating an evidentiary gap under the consumer-disclosure requirements of ESIGN, 15 U.S.C. §7001(c). Overbroad permissions can allow staff without a treatment, payment, or operations role to view clinical justification and other protected health information. A missing payer attachment, diagnosis code, provider signature, or service detail can make the request incomplete and delay authorization review.
Troubleshooting prior authorization requests
Resolve authorization delays by checking the payer’s rules, signer identity, protected-health-information controls, field mapping, and final audit evidence.
On the Business plan, verify that the sender has an available signature invite and that the request is routed to the intended participant. If the organization needs bulk sending for many authorization requests, Business Premium includes bulk send; review the plan before changing the workflow.
A HIPAA-covered workflow requires a business associate agreement with signNow and appropriate organizational safeguards. Confirm the BAA, access permissions, recipient identity, and disclosure procedures before placing patient information into the request or sending it for signature.
signNow can capture signatures, timestamps, document history, and audit-trail evidence, but it does not decide whether a payer accepts electronic authorization requests. Confirm the payer’s submission channel, attachment rules, and signature requirements before relying on the completed file.
Check the recipient email address, spam filtering, and signing-link access first. If SMS or stronger authentication is required, confirm the configured authentication method and signer contact information. Do not forward a protected authorization link to an unauthorized person.
Use the detected fields as a starting point, then compare them with the actual prior authorization layout. Verify patient identifiers, payer details, requested service, diagnosis, clinical justification, and signatures manually before sending the document.
Download the completed request together with its audit trail or completion certificate, then place both in the approved record system. HIPAA-covered records generally require six years under 45 CFR §164.530(j), subject to longer state or organizational requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.