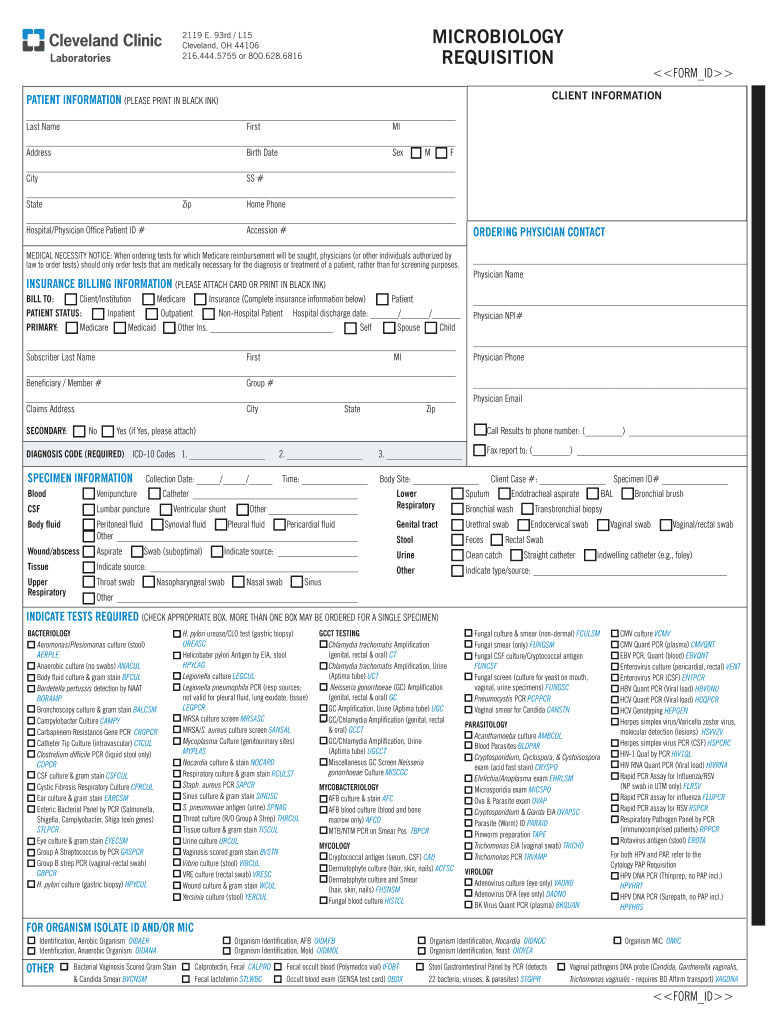
Microbiology Requisition Cleveland Clinic Laboratories Form
Use a Microbiology Requisition Cleveland Clinic Laboratories template to make your document workflow more streamlined.
What this microbiology requisition does
The Microbiology Requisition Cleveland Clinic Laboratories Form is a healthcare laboratory request used to organize information needed for microbiology testing at Cleveland Clinic Laboratories. A submitting healthcare provider records patient identifiers, specimen details, requested testing, ordering information, and required authorization in the designated fields. The completed requisition travels with the specimen or electronic request so laboratory personnel can identify the patient, understand the requested work, and document responsibility for the order. Because patient information may be protected health information, organizations should apply HIPAA safeguards and their laboratory’s submission procedures.
Who uses this microbiology requisition
Healthcare providers
Healthcare providers complete patient and ordering-provider details before requesting microbiology testing.
Laboratory teams
Clinical laboratory teams review submitted requisitions, verify required information, and retain completed records.
Business types that benefit from this requisition
The form is most useful where healthcare teams must collect complete specimen and ordering information before laboratory processing.
Independent physician practices use the requisition to capture patient, specimen, ordering-provider, and test information before sending microbiology work to Cleveland Clinic Laboratories. Urgent care centers use a reusable requisition workflow to collect complete specimen details, obtain required signatures, and route laboratory requests without repeated paper handling. Hospital laboratory networks use shared templates, controlled permissions, and audit trails to standardize microbiology requisitions across departments while protecting patient information.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete the requisition in signNow
Move the Cleveland Clinic Laboratories requisition from upload through field review, signature routing, completion, and controlled storage.
Upload form:
Upload the Cleveland Clinic Laboratories requisition PDF. Check fields:
Review detected fields and add missing patient or specimen fields. Assign signers:
Assign provider and laboratory signer roles. Send request:
Send the completed request through the approved workflow. Store records:
Download the signed requisition and completion record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the requisition workflow works
signNow turns the Cleveland Clinic Laboratories requisition into a controlled electronic workflow without changing the laboratory request itself.
Upload: Upload the requisition PDF to signNow. Detect fields: Auto-detect fillable fields for review. Route: Send assigned fields to authorized signers. Preserve: Store the completed requisition with its audit trail.
Platform requirements for completing the form
Use TLS-enabled Chrome, Firefox, Safari, or Edge on Windows 10, Windows 11, or macOS. signNow also provides apps for iOS and Android.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows 10, Windows 11, and macOS Mobile apps iOS and Android signNow apps
Healthcare organizations should use managed devices, approved accounts, and access controls suited to protected health information. Confirm that the Cleveland Clinic Laboratories submission process accepts the completed electronic record and that authorized staff can retrieve the signed document and audit trail.
Security for microbiology requisitions
HIPAA safeguards:
HIPAA BAA:
Stored encryption:
Transport encryption:
SOC 2 Type II:
ISO 27001:
Recommended requisition workflow setup
Configure the Cleveland Clinic Laboratories requisition around verified signer identity, protected health information, evidence, and controlled retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Legally binding electronic signature |
| Audit trail | Enabled with completion certificate |
| Document retention | Six years for HIPAA documentation (45 CFR 164.530(j)) |
| Encryption | TLS 1.2/1.3 and AES-256 |



What the requisition audit trail records
The audit trail preserves evidence around the Cleveland Clinic Laboratories requisition rather than replacing the clinical information inside it.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Export evidence:
Retrieve record:
Recordkeeping practices for this requisition
Preserve the completed requisition, its evidence, and its access controls according to the healthcare organization’s records policy.
Apply the HIPAA six-year documentation rule
Export and link the audit trail
Use encrypted HIPAA safeguards
Coordinate retention with healthcare policy
Privacy pitfalls in microbiology requisitions
Including unnecessary patient identifiers in the signed requisition increases disclosure exposure if the file is shared outside the approved laboratory channel. Sending a requisition to an unverified recipient can expose protected health information and weaken evidence that the ordering provider authorized the request. Omitting consent or authorization documentation may leave the healthcare organization unable to demonstrate the patient’s permission for the requested disclosure. Broad template permissions can let unauthorized staff alter patient, specimen, or test fields before signing and submission.
Troubleshooting this requisition workflow
These answers address field detection, protected health information, signer access, audit evidence, plan capabilities, and mobile completion.
Upload the original requisition PDF again and check whether fields are flattened or protected. signNow Business supports templates and audit trails, while field placement may require manual review when the source PDF is not fillable.
Confirm that the assigned recipient is the intended ordering provider or authorized healthcare worker. For protected health information, use the organization’s approved identity controls and a HIPAA-supported configuration, including a required BAA where applicable.
Check the recipient email, role order, and required fields before resending. signNow records invitation and signing events in the audit trail, helping the administrator identify whether delivery, access, or completion stopped the request.
Use signNow’s audit trail and completion certificate to verify who acted, when the action occurred, and which document was completed. Retain both with the requisition under the healthcare organization’s records policy.
The Business plan includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR. HIPAA-covered use requires a business associate agreement and appropriate organizational safeguards.
Signers can use a browser or signNow mobile app on supported iOS and Android devices. If a camera capture or offline workflow is used, confirm that the final requisition remains legible and reaches the approved laboratory channel.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.