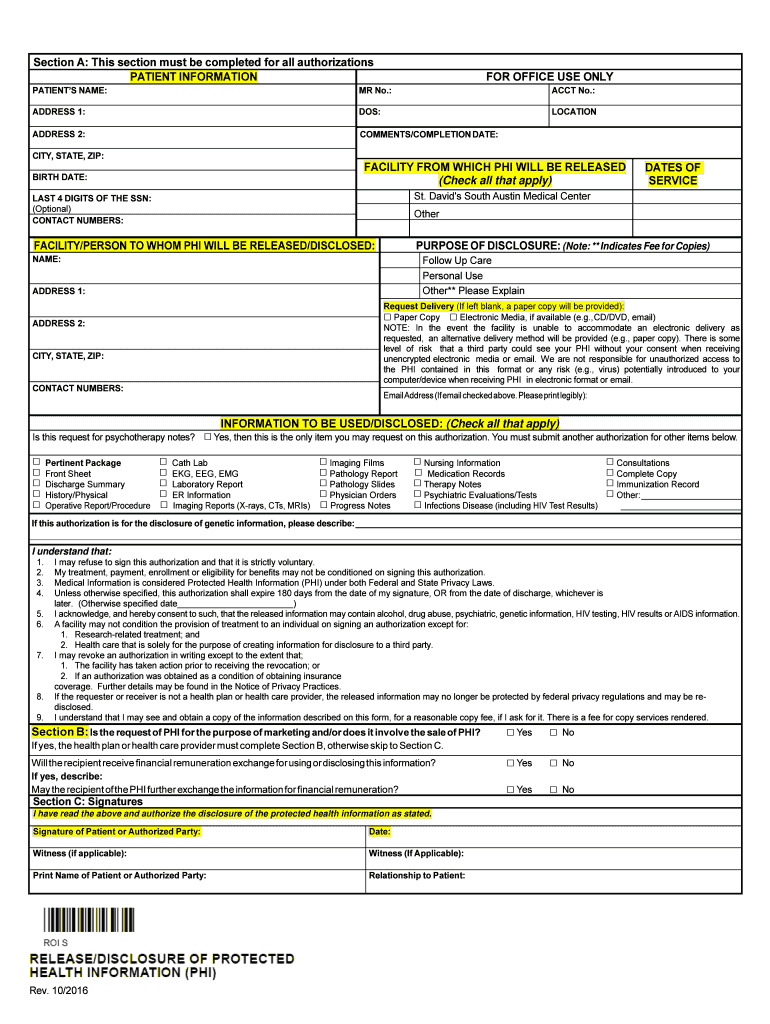
Releasedisclosure Of Protected Health Information Request For Records
Use a ReleaseDisclosure Of Protected Health Information Request For Records template to make your document workflow more streamlined.
What this protected health information request does
A Releasedisclosure Of Protected Health Information Request For Records authorizes a healthcare provider or covered entity to release specified protected health information to a named recipient. The requester identifies the patient, records, date range, purpose, recipient, delivery method, and authorization period, then signs the request. A personal representative may sign when legally authorized. HIPAA’s Privacy Rule governs the disclosure, while 45 CFR §164.508 addresses authorization content. The form should be completed accurately, signed, retained, and handled through an access-controlled process.
Who uses this records request
Healthcare providers
Healthcare providers use the request to document a patient’s authorization, identify the records sought, name the recipient, and capture the patient’s signature before releasing protected health information.
Authorized requesters
Patients, personal representatives, and authorized recipients use the request to specify records, delivery details, and authorization limits for a traceable disclosure workflow.
Who benefits from this request workflow
The form supports patient-authorized disclosures across independent practices, hospital release teams, and multi-site healthcare organizations handling protected health information.
Solo medical practices can collect patient authorizations remotely, identify requested records and recipients, and retain a completed request without coordinating paper exchanges. Hospital release-of-information teams can route standardized requests to patients or representatives, review authorization fields, and preserve audit evidence for disclosure processing. Enterprise healthcare networks can use templates, delegated sending, and role-based access to manage high-volume records requests across facilities while controlling PHI access.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Recommended request workflow settings
Configure the records request around signer identity, authorization evidence, PHI safeguards, and the applicable HIPAA retention rule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Preserve completion certificate and action history |
| Document retention | Six years under 45 CFR §164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
Complete the records request in signNow
Use the original request, confirm every disclosure field, and retain the completed authorization with its audit trail.
Upload form:
Upload the records request to signNow. Check fields:
Review detected fields and add missing authorization fields. Assign signer:
Assign the patient or representative as signer. Send request:
Send the request through signNow. Collect signature:
Collect the signature and completed authorization. Store records:
Store the signed request and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the audit trail supports disclosure evidence
A signNow audit trail records the request’s signing events and completed-document history for later review by authorized healthcare teams.
Authenticate signer:
Capture timestamp:
Track document history:
Seal record:
Log actions:
Export evidence:
Security for protected health information
HIPAA safeguards:
Transit encryption:
Stored encryption:
Control assurance:
Security management:
Signing history:
Privacy pitfalls to avoid
Leaving the requested record types or date range blank can make the authorization too vague for the provider to process. Entering a recipient without a complete name, address, or delivery method can create an avoidable disclosure error. Sending protected health information before the required patient or representative signature is collected can undermine the authorization workflow. Sharing a completed request through an unsecured channel can expose sensitive health information beyond the intended recipient.
Features for this records request
signNow combines field placement, signer routing, audit evidence, and PHI safeguards for a controlled electronic authorization workflow.
Clear authorization
Structured fields keep the patient, recipient, record scope, purpose, and authorization period together for review before disclosure.
Signer routing
Assigned signature fields direct the patient or authorized representative to the correct signing locations.
Audit trail
The audit trail records signing activity and supports evidence that the request was completed without altering the final file.
PHI safeguards
HIPAA support, a BAA requirement, TLS, and AES-256 help protect PHI during transmission and storage.
Reusable template
Templates let healthcare teams reuse an approved request structure while preserving required patient-specific fields.
Mobile signing
Mobile apps allow authorized staff and requesters to review and sign the form away from a desktop.



Best practices for records disclosure
Use a controlled authorization process that connects precise form fields with retention, audit evidence, and minimum-necessary review.
Set the six-year retention rule
Export the audit trail
Restrict access to PHI
Validate every authorization field
Retention rules for signed records
For this health-information request, retain the authorization and related evidence for six years under HIPAA’s documented retention rule.
Six years: HIPAA records
Three years: IRS records
Three years: I-9 records
Three years: FLSA payroll
Five years: OSHA injury
Risks of an incomplete records request
Invalid authorization
Wrong recipient
Incomplete signature
Excess disclosure
Troubleshoot this records request
These answers address authorization, PHI handling, signer identity, and signNow workflow issues for this specific records request.
Yes. signNow identifies the uploaded document’s fields, and you can review or add signature, date, and authorization fields before sending the request. Confirm that the patient, representative, recipient, record scope, and expiration details match the underlying disclosure authorization.
For protected health information, use a signNow plan and configuration that supports HIPAA compliance and execute the required business associate agreement. HIPAA compliance is not created by an eSignature alone; the healthcare organization remains responsible for its authorization and disclosure procedures.
The Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures. Business Premium adds bulk send and kiosk mode. Enterprise adds advanced signer authentication. Confirm that the selected plan and BAA arrangement fit the healthcare workflow before processing PHI.
Use the signer assignment and authentication options to identify the patient or authorized representative. If stronger identity proofing is needed, Enterprise adds advanced signer authentication. Keep the recipient and authorization scope specific so identity evidence supports the requested disclosure.
A request can be signed electronically when the signer demonstrates intent, consents to electronic records, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable state law support electronic signatures, but HIPAA authorization requirements still apply separately.
If a signer cannot complete the request, review required fields, recipient email, authentication settings, and device access. signNow preserves document history and audit-trail events, so correct the form before resending rather than altering a completed authorization.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.