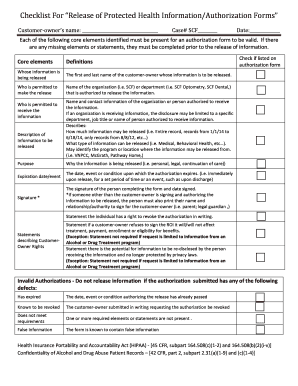
Checklist for Release of Protected Health Information Authorization Forms
Use a Checklist For Release Of Protected Health InformationAuthorization Forms template to make your document workflow more streamlined.
What this PHI authorization checklist does
Checklist for Release of Protected Health Information Authorization Forms documents a patient’s permission for a covered entity to disclose specified protected health information to an identified recipient. The checklist records the patient or representative, requested records, disclosure purpose, recipient, expiration or event, and required signatures. In signNow, the sender uploads the form, reviews detected fields, assigns participants, and sends it for electronic signing. The completed authorization and Audit Trail can then be retained for disclosure review under HIPAA 45 CFR 164.530(j).
Who uses PHI authorization checklists
Healthcare providers
Healthcare providers and medical practices use the checklist to document a patient’s permission for specified PHI disclosures. Staff identify the patient, recipient, requested records, purpose, expiration, and required signatures before releasing information. signNow supports electronic completion, mobile signing, and Audit Trail preservation within a HIPAA-compliant workflow requiring a BAA.
Authorization participants
Patients, authorized representatives, health plans, attorneys, and records departments use the completed authorization to coordinate a defined release. Each audience reviews only the fields relevant to its role, while the provider retains the signed checklist and supporting evidence under HIPAA and applicable state privacy policies.
How this PHI checklist works
The workflow turns a paper-style PHI authorization checklist into a controlled electronic record, from field review through signed retention.
Upload form: Upload the checklist PDF to signNow and allow its field-detection tools to identify completion areas. Review details: Review patient, recipient, purpose, expiration, and signature fields before assigning participants. Request signatures: Send the authorization to the patient or representative and other required signers. Archive record: Store the signed checklist with its Audit Trail before processing the PHI release.
How to complete the authorization checklist
Complete the PHI authorization checklist in signNow by checking each disclosure detail before requesting signatures and storing the completed record.
Upload form:
Upload the authorization checklist PDF to signNow. Check fields:
Review auto-detected fields against every authorization requirement. Assign signers:
Assign the patient and provider representative as signers. Send request:
Send the completed authorization for electronic signatures. Store records:
Download the signed form and Audit Trail.
Choose a signing method for PHI authorizations
- Use the signNow web app when staff need to upload the authorization checklist, verify PHI disclosure fields, assign signers, and monitor completion from a desktop browser.
- Use the signNow mobile app when clinicians or patients must review and sign the authorization checklist from iOS or Android during an active care workflow.
- Use kiosk mode for supervised, in-person completion at a healthcare reception desk, where staff control the device and confirm the patient reviews each disclosure field.
- Use a shareable signing link when a controlled intake process repeatedly collects the same authorization checklist, while limiting access and verifying each signer’s identity.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended PHI authorization setup
Configure authentication, signing, audit evidence, retention, encryption, and user access before sending a PHI authorization checklist.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with intent |
| Audit trail | Export with signed authorization |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
Security for PHI authorization records
HIPAA compliance:
Business Associate Agreement:
Data in transit:
Data at rest:
Security controls:
Information security:
What the signNow Audit Trail records
The signNow Audit Trail preserves technical evidence of who signed the PHI authorization checklist, when each action occurred, and how the final record was completed.
Authenticate signer:
Record timestamp:
Track document history:
Seal document:
Complete certificate:
Export evidence:
Retention periods for PHI authorization records
Keep signed authorization records and supporting HIPAA documentation for the applicable federal period, while checking stricter state requirements.
Six years from creation or last effective date
Six years for authorization documentation
Six years for access procedure records
Six years for complaint documentation
Six years for privacy training records
Best practices for retaining PHI authorizations
Use a documented review, signing, export, and retention process so every PHI authorization remains understandable, attributable, and retrievable.
Review every authorization field before sending
Export the signed record and Audit Trail
Apply HIPAA’s six-year retention rule
Confirm the BAA and access controls
Privacy pitfalls in PHI authorizations
Including a broad recipient description can authorize disclosure beyond the patient’s intended provider, organization, or records custodian. Leaving purpose, expiration, or requested-record fields blank weakens the authorization’s clarity and may delay a disclosure review. Sending PHI through an uncontrolled link can expose the signed checklist to an unintended recipient or unauthorized device. Storing the signed authorization without its Audit Trail separates the patient’s signature from evidence of the signing event.
Risks of incomplete PHI authorization
Disclosure may be unauthorized
Authorization may be rejected
PHI may be misdirected
Execution evidence may be incomplete
Features for PHI authorization checklists
signNow connects field preparation, signer assignment, HIPAA controls, electronic signing, and audit evidence for protected health information authorizations.
Field detection
Upload the checklist and let signNow identify signature, date, and text fields, reducing manual preparation before reviewing patient-specific authorization details.
Role assignment
Assign patients, providers, and authorized recipients to defined fields so each person signs the correct portion of the PHI authorization checklist.
Audit Trail
Capture timestamps, signer actions, and completion history in an Audit Trail that supports review of how the authorization was executed.
HIPAA workflow
Use signNow’s HIPAA-compliant environment with a required BAA to help protect PHI during electronic authorization workflows and document storage.
Mobile signing
Send the checklist through web or mobile workflows so patients can review and sign without returning paper documents to the healthcare office.
Secure records
Store the signed authorization with its Audit Trail so disclosure teams can retrieve the evidence supporting the permitted PHI release.



Troubleshooting PHI authorization workflows
Resolve field detection, signer access, plan, and retention questions before releasing protected health information through an authorization checklist.
Use signNow’s auto-detect fields to identify signature, date, and text areas after uploading the authorization checklist. Review every detected field against the patient’s name, requested records, recipient, purpose, and expiration details before sending.
The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps. HIPAA workflows require a Business Associate Agreement with signNow; confirm the BAA and internal access controls before handling PHI.
Business Premium adds bulk send and quick invite links, but each authorization should still be reviewed for patient-specific scope and recipient details. Do not reuse a template without checking the permitted disclosure fields.
If a signer cannot open the request, verify the email address, resend the invitation, or provide a controlled signing link. SMS authentication can add identity verification, but it does not replace required authorization language.
A signed authorization does not itself establish HIPAA compliance. signNow provides HIPAA compliance with a required BAA, while the covered entity remains responsible for valid consent, minimum necessary disclosure, access controls, and retention.
Export the completed document and its signNow Audit Trail, then store both under your records policy. HIPAA 45 CFR 164.530(j) requires covered entities to retain required documentation for six years.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.