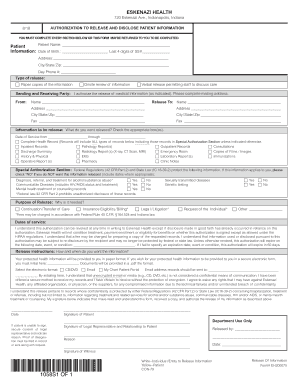
Authorization For Release Of Health Information Forms In Gov
Use a Authorization For Release Of Health Information Forms IN gov template to make your document workflow more streamlined.
What this health authorization does
Authorization For Release Of Health Information Forms In Gov is a written permission form that lets a patient or authorized representative identify which health information may be disclosed, to whom, and for what purpose. The completed form normally records the individual’s identifying details, requested records, recipient, purpose, expiration or revocation terms, signature, and date. With signNow, the sender uploads the form, places or detects fillable fields, assigns signer roles, sends it for review, and preserves the signed record and audit trail for controlled disclosure workflows.
Who benefits from this authorization
Clinics, records departments, and government health programs use this form when a documented release decision must be collected, verified, and retained.
A solo medical practice can collect patient authorizations for specified records, recipients, and purposes without printing each request, while keeping the completed form with its signing history. A hospital release-of-information department can route authorizations to patients, representatives, and records staff, using role-based workflows to reduce incomplete disclosure instructions and repeated follow-up. A government health program or large provider network can standardize authorization templates, control access, and retain signed records across departments while applying HIPAA safeguards and documented policies.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How this authorization works online
The signNow workflow turns the release authorization into a controlled sequence from document preparation through signed-record storage.
Upload form: Upload the health-information authorization PDF. Add fields: Detect or place fields for consent details. Assign signer: Assign the patient or representative signer. Complete record: Send, sign, and preserve the audit trail.
Complete the authorization in signNow
Follow these steps to prepare, route, complete, and retain Authorization For Release Of Health Information Forms In Gov in a controlled electronic workflow.
Upload form:
Upload the authorization PDF to signNow. Prepare fields:
Auto-detect or place patient and recipient fields. Assign signer:
Assign the patient or representative as signer. Send request:
Send for signature and review completion. Archive record:
Store the signed form with its audit trail.
Choose the right signing method
- Use the signNow web app when preparing the authorization, placing fields, and sending it to a patient or representative from a desktop workflow.
- Use the signNow mobile app when staff or patients need to review and sign the authorization on iOS or Android during field or clinic work.
- Use kiosk mode when a patient signs the authorization on a managed device at a reception desk, intake station, or government service location.
- Use a shareable signing link when repeatedly collecting the same authorization from patients, representatives, or records recipients without sending individual email invitations.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for release authorizations
signNow connects form completion, signer routing, consent evidence, and protected record handling around the specific release authorization workflow.
Fillable fields
Upload the authorization once, then use detected or placed fields for the patient, representative, recipient, purpose, expiration, signature, and date.
Role assignment
Assign each signer and recipient clearly so the authorization identifies who may release information and who may receive the specified records.
Flexible signing
Collect signatures through email invitations, mobile signing, kiosk mode, or links while matching the method to the patient’s access needs.
Audit trail
Preserve the completed authorization with timestamps, signer actions, and document history so staff can investigate how consent was captured.
Reusable templates
Use templates for recurring release requests while limiting editing rights and maintaining consistent disclosure language across departments.
HIPAA controls
Keep protected health information in a controlled workflow supported by HIPAA compliance and a business associate agreement where required.
Security for health authorizations
HIPAA protection:
Transport encryption:
Storage encryption:
Security reporting:
Information security:
Signer accountability:
Recommended authorization setup
Configure the authorization workflow around signer identity, consent evidence, protected information, and documented retention responsibilities.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication for signers |
| Signature type | Electronic signature with intent evidence |
| Audit trail | Enabled with export after completion |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
What the audit trail records
For this authorization, the audit trail connects signer identity, consent actions, document integrity, and retrieval evidence without replacing the organization’s records policy.
Authenticate signer:
Capture timestamps:
Hash document:
Seal document:
Log actions:
Export trail:
Retention periods for signed authorizations
Retention depends on the record type, covered-entity status, state law, and organizational policy. Apply the longest applicable requirement after legal review.
Six years: HIPAA documentation
State-defined period: health records
Until expiration: active authorization
Investigation period: disputed release
Policy period: related records
Retention and record-keeping practices
Keep the authorization, completed form, and consent evidence together under the health-information retention policy that applies to the organization.
Set a documented retention schedule
Export the audit trail
Limit access to release records
Archive protected information securely
Legal standing and exclusions
An electronically signed authorization can be admissible when the signer shows intent, consents to electronic records, can be identified, and the record remains reproducible under ESIGN and applicable UETA law. Those frameworks exclude wills, codicils, testamentary trusts, court orders, official court filings, and family law decrees.



Authorization form troubleshooting
These answers address field setup, signer identity, HIPAA handling, plan capabilities, and retention for this health-information release authorization.
On signNow’s Business plan, upload the authorization and place fields manually or use field detection before assigning the patient or representative. Confirm every required field, including the disclosure purpose, recipient, signature, and date, before sending.
Use signNow’s signer authentication options, including two-factor authentication or SMS OTP where configured, to strengthen attribution. HIPAA compliance requires a BAA when applicable, but the organization remains responsible for verifying representative authority and disclosure scope.
A signature alone does not authorize unlimited disclosure. The authorization should identify the information, recipient, purpose, and expiration or event. Review the form against HIPAA requirements and applicable state law before releasing records.
Business includes templates, audit trails, and mobile apps. Business Premium adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication. Confirm the selected plan and configuration before using kiosk or high-volume authorization workflows.
The HIPAA compliance designation includes a business associate agreement requirement. Confirm that the organization has the required BAA, limits access, configures authentication, and follows its own privacy, incident-response, and retention policies.
Download the completed authorization and audit trail from signNow after the final signature, then store them in the approved health-record repository. Apply the organization’s retention policy and the six-year HIPAA documentation rule where 45 CFR §164.530(j) applies.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.