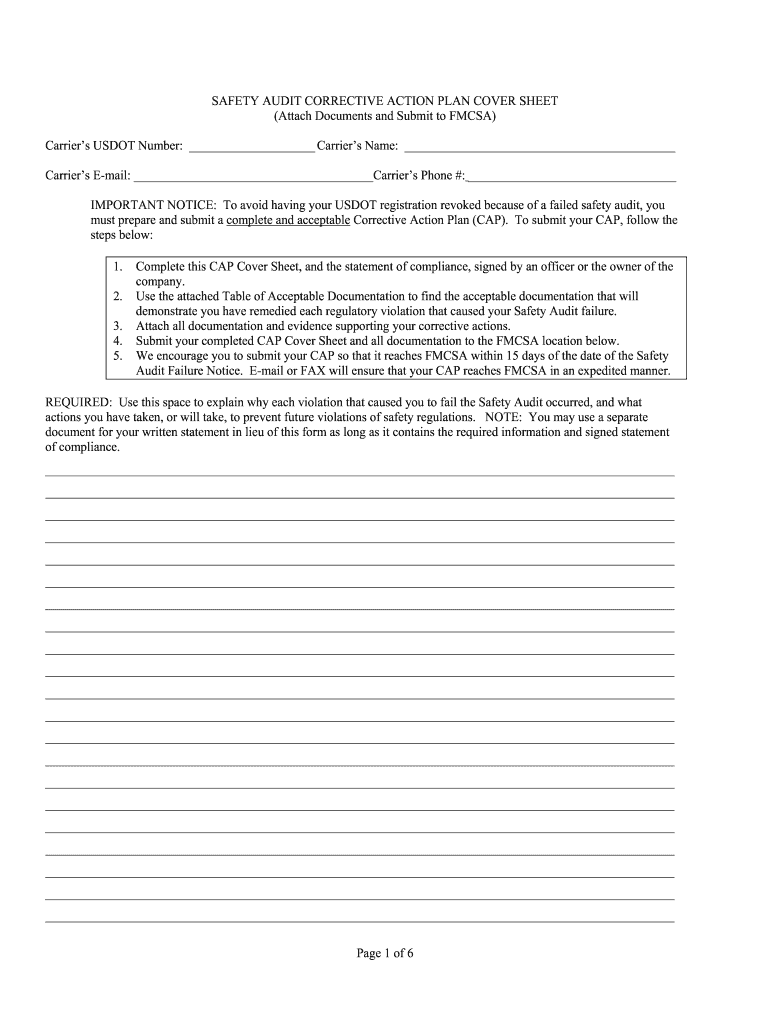
Of 6 Safety Audit Corrective Action Plan Cover Ok Gov Form
Use a Of 6 SAFETY AUDIT CORRECTIVE ACTION PLAN COVER OK gov template to make your document workflow more streamlined.
What this safety audit form does
The Of 6 Safety Audit Corrective Action Plan Cover Ok Gov Form is a cover document for organizing a safety audit’s corrective-action review and approval. It identifies the plan being submitted, connects findings with corrective measures, and provides signature points for responsible reviewers. Because the supplied form name does not identify a state agency, statutory filing deadline, or official form number, those details should be confirmed with the issuing Oklahoma office before submission. signNow can upload the cover, detect fillable fields, route it to named signers, and preserve the completed record with an audit trail.
Who uses this corrective action plan cover
Safety and compliance teams
Safety officers and compliance coordinators use the cover to identify an audit, assign corrective actions, document responsible reviewers, and obtain approval without circulating paper copies. They should confirm the Oklahoma program, facility, and submission instructions before treating the completed document as an agency filing.
Operations and government reviewers
Operations managers, contractors, and government reviewers use the cover to coordinate corrective-action ownership and sign-off. The workflow can include contracts, inspection attachments, approval records, and related acknowledgments, but the exact supporting documents depend on the issuing program and the audit’s subject.
Privacy and disclosure pitfalls
Uploading an outdated corrective action cover can place obsolete project identifiers, reviewer fields, or approval instructions into the signed record. Sending the form without required safety findings or corrective-action dates may produce an approval record that cannot support meaningful follow-up. Including employee, facility, or incident details in unrestricted copies can expose personal or operational information beyond the intended review group. Failing to capture electronic consent and signer identity can weaken evidence that each reviewer intended to approve this specific safety plan.
How this safety audit workflow works
The signNow workflow turns this safety audit cover into a controlled review sequence from upload through signed archival.
Upload: Upload the current cover document. Check fields: Review detected fields and add missing safety-plan inputs. Route: Send the prepared cover to assigned reviewers. Archive: Store the signed PDF with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents technical evidence around this safety audit cover rather than replacing review of its corrective-action content.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Record events:
Export trail:
Quick steps for this form
Prepare the exact safety audit cover, verify its fields, and preserve evidence after every required signature.
Upload form:
Upload the current safety audit cover. Check fields:
Review fields for findings and approvals. Add signers:
Add reviewers and signing order. Complete record:
Send, monitor, and download the completed record.
Features for this safety audit cover
signNow connects document preparation, reviewer routing, electronic signatures, and evidence preservation around the specific corrective action plan cover.
Field detection
Upload the named safety audit cover and let signNow identify likely fillable areas before you review the document manually.
Signer routing
Assign the corrective-action cover to responsible reviewers and control the order in which approvals are requested.
Audit trail
Capture timestamps, signer activity, and completion evidence for the executed safety audit record.
Reusable template
Use templates when the same Oklahoma safety audit cover repeats across facilities or review cycles.
Mobile review
Review and sign from signNow mobile apps when an authorized reviewer is away from the office.
Record storage
Keep the completed cover and supporting audit evidence together in a controlled record repository.
Platform requirements for this safety audit form
Complete the Of 6 Safety Audit Corrective Action Plan Cover Ok Gov Form through Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow uses TLS 1.2 or TLS 1.3 for data in transit, and its mobile apps support iOS and Android access.
Desktop browsers Use Chrome, Firefox, Safari, and Edge on Windows or macOS. Mobile apps Use signNow mobile apps on iOS and Android devices. Secure connection Maintain TLS 1.2 or TLS 1.3 connectivity for secure access.
Use a managed Windows, macOS, iOS, or Android device when the safety audit contains operational details. Confirm browser updates, camera permissions, and network access before uploading the form. Enterprise administrators can also review API, SSO, and certificate requirements before connecting the workflow to internal systems.
Security for signed audit records
Encryption:
Security certification:
Information security:
Health information:
Electronic signatures:
Privacy controls:
Retention periods for related records
The form name does not establish one universal retention period. Apply the rule matching the information attached to this safety audit cover, and verify any Oklahoma program requirement.
Three years for tax records
Six years for HIPAA records
Three years for payroll records
Five years for injury records
Thirty years for exposure records
Troubleshooting this safety audit form
These answers address field detection, signer access, plan selection, electronic-signature evidence, and retention questions for this specific safety audit cover.
If signNow does not detect a field on the safety audit cover, open the document editor and place the missing text, date, checkbox, or signature field manually. Compare the field placement with the source form before sending, because automatic detection does not establish the agency’s required layout.
The Business plan includes templates, audit trails, and legally binding eSignatures at $8/user/month with annual billing. Business Premium is $15/user/month annually and adds bulk send. Choose the plan based on the number of reviewers and repeated safety audit covers, not the form title.
signNow states that its eSignatures comply with ESIGN and UETA. For this safety audit cover, preserve signer intent, electronic consent where required, attribution, and a reproducible record. Confirm separately whether the Oklahoma program requires a wet signature, notarization, or agency portal submission.
If the cover contains protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Do not assume the form is a HIPAA record merely because it is a safety document; determine whether PHI is actually present and apply the six-year rule when applicable.
A signer can review the document from signNow’s web or mobile experience, but an account requirement, authentication method, or device restriction may affect access. Verify the recipient email, resend the invitation, or use a configured SMS authentication method before changing the document.
After completion, download the signed safety audit cover and its audit trail or completion evidence, then store both with the source upload and related corrective-action materials. Restrict access and document the applicable retention rule instead of deleting records when a workflow closes.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.