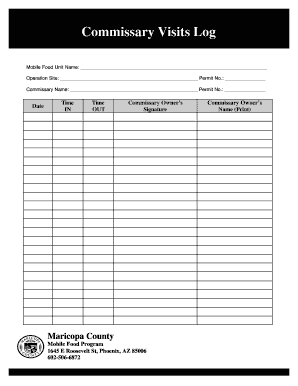
Commissary Visits Log Maricopa County Maricopa Form
Use a Commissary Visits Log Maricopa County Maricopa template to make your document workflow more streamlined.
What this commissary visits log records
The Commissary Visits Log Maricopa County Maricopa Form is a record for documenting commissary-related visits in Maricopa County. In signNow, an authorized user uploads the log, reviews automatically detected fillable areas, assigns fields to visitors or facility personnel, and sends the document for electronic completion. Each participant can review assigned information before signing. The completed PDF remains associated with an audit trail that records signing actions, timestamps, and available identity evidence. Facility policy determines which entries are required, who may access the record, and how long it must be retained.
Who uses this commissary visits log
Detention personnel
Maricopa County detention and commissary personnel can use the log to record scheduled visits, identify participants, document approvals, and preserve a consistent electronic record for internal review.
Visitors and supervisors
Visitors, supervisors, and authorized administrators can complete assigned fields, sign the relevant entries, and review the final record without exchanging multiple paper copies.
Features for the commissary visits log
signNow connects field preparation, recipient routing, electronic signing, and audit evidence around the specific Maricopa County commissary visits log.
Field detection
Upload the Maricopa County log and review detected fields before routing it, reducing manual recreation of visitor, staff, date, and approval fields.
Role assignment
Assign each log entry to a specific recipient so visitors and facility personnel know exactly which information and signatures belong to them.
Remote signing
Send the completed log through email or a controlled signing link, allowing authorized participants to review the same document remotely.
Audit trail
Capture timestamps, signer actions, and available identity details with the document, creating evidence for later administrative review.
Reusable template
Use templates for the approved commissary visits log so recurring facility workflows begin from a controlled document version rather than an unreviewed copy.
Record storage
Keep the signed PDF and related signing evidence together in the organization’s approved storage process for easier retrieval and records review.
Complete the commissary visits log
Prepare the Maricopa County commissary visits log in signNow by uploading the file, checking fields, assigning participants, and preserving the signed record.
Upload the log:
Upload the current commissary visits log PDF to signNow. Check fields:
Review detected fields and add missing visitor or approval fields. Assign signers:
Assign each field to the appropriate visitor, officer, or supervisor. Complete and store:
Send the log, collect signatures, and download the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the visits log workflow works
The workflow moves the Maricopa County commissary visits log from an uploaded PDF to an assigned, signed, and auditable electronic record.
Prepare document: Upload the log and inspect its detected fields. Route fields: Assign visitor, officer, and supervisor fields to recipients. Collect signatures: Recipients review the visit details and sign electronically. Store record: The completed log and audit evidence remain available for authorized review.
Set up the commissary visits log
Use a controlled signing workflow that identifies each signer, preserves the completed log, and limits access to authorized facility personnel.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Click-to-sign with signer intent |
| Audit trail | Retain timestamps, IP addresses, and action history |
| Document retention | Follow the facility’s approved records schedule |
| Encryption | AES-256 at rest and TLS in transit |
Review the log audit trail
The audit trail records technical evidence around the Maricopa County visits log, helping administrators explain who signed, when actions occurred, and whether the record changed.
Authenticate signer:
Capture timestamp:
Hash document:
Seal history:
Connect evidence:
Export audit trail:
Security for the signed log
AES-256 and TLS:
SOC 2 Type II:
ISO 27001 certification:
GDPR compliant controls:
ESIGN and UETA compliant:
Two-factor authentication options:



Best practices for this log
A controlled process helps Maricopa County personnel preserve accurate visit entries, signer evidence, and access decisions for the completed commissary visits log.
Use the approved county version
Assign each entry clearly
Restrict personal information access
Archive the log with evidence
Troubleshoot the signed visits log
Resolve field, delivery, signing, privacy, legal-record, and plan questions before treating a Maricopa County commissary visits log as complete.
If signNow does not detect the log’s fields, upload a clear PDF and add text, date, checkbox, and signature fields manually. Detection does not determine which entries Maricopa County requires; compare the document with the approved facility version.
If a recipient cannot open the document, verify the email address, resend the invitation, or provide a controlled signing link. Business plans include legally binding eSignatures and audit trails, but recipient access still depends on the delivery details used.
If a signature is missing, inspect the assigned recipient and required field settings before resending. A completed record should not be treated as final until every required Maricopa County entry and approval has been completed.
If the log contains sensitive personal information, restrict recipients and administrator access, use available two-factor authentication, and follow the facility’s privacy policy. signNow states that its security program includes SOC 2 Type II and ISO 27001 certifications.
For U.S. electronic records, ESIGN and applicable UETA rules generally require intent, consent, attribution, and record reproducibility. Keep the completed log and audit trail together so those elements can be evaluated later.
The Business plan is listed at $8 per user per month with annual billing and includes audit trails, templates, and mobile apps. It includes 100 signature invites per user annually; verify plan limits before recurring high-volume use.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.