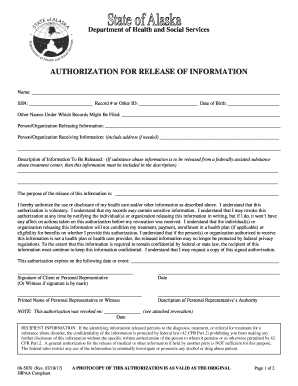
Authorization For Release Of Information Form
Use a AUTHORIZATION FOR RELEASE OF INFORMATION Form 2017 template to make your document workflow more streamlined.
What this authorization form does
An Authorization For Release Of Information Form records an individual’s permission for an identified person or organization to disclose specified information to a named recipient. The form usually states whose information may be released, which records are covered, the purpose, recipient, expiration, signature, and revocation instructions. In signNow, a sender uploads the document, reviews automatically detected fields, assigns the signer, sends it by email or link, and stores the completed PDF with its audit trail. HIPAA, FERPA, state privacy law, and the document’s wording determine the disclosure requirements.
Who uses this authorization form
Healthcare providers
Healthcare providers use this authorization to document a patient’s permission before releasing specified records to an identified recipient. HIPAA workflows should define the information scope, purpose, expiration, revocation process, access permissions, and retention policy before disclosure.
Administrative teams
Legal, insurance, education, and employer teams use release authorizations when an individual permits records to move between identified parties. They can send the form for signature, preserve consent evidence, and connect the completed record to the matter or case file.
How the authorization workflow works
The signNow process turns the authorization into a controlled sequence from document preparation through signed-record retention.
Upload form: Upload the authorization document to signNow. Detect fields: Auto-detect fields and verify authorization details. Set roles: Assign the signer and intended recipient. Complete record: Send, sign, and retain the completed record.
How to complete the authorization online
Use this signNow workflow to prepare, send, execute, and retain an Authorization For Release Of Information Form.
Upload document:
Upload the authorization form. Check fields:
Review detected fields and add missing fields. Assign roles:
Assign the individual signer and recipient. Send securely:
Send by email or signing link. Archive record:
Review the signed PDF and audit trail.
Legal standing of an electronic authorization
An electronic Authorization For Release Of Information Form can provide admissible evidence when the signer shows intent, consents to electronic records, can be identified, and the record remains reproducible. ESIGN and UETA support electronic signatures, but wills, court orders, family-law decrees, and other statutory exceptions remain outside their general coverage.

 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Best practices for completing the authorization
Accurate scope, informed consent, controlled disclosure, and a reproducible signed record are central to this authorization workflow.
Review every authorization element
Verify detected fields manually
Capture electronic consent clearly
Limit disclosure and access
Security controls for signed authorizations
Transport encryption:
Stored data encryption:
Healthcare safeguards:
Control assurance:
Information security:
Electronic signature law:
Find and fill out the correct authorization for release of information form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| AK DHSS 06-5870 2017 | 4.8 Satisfied (1419 Votes) | |
| AK DHSS 06-5870 2004 | 4.7 Satisfied (104 Votes) |
Platform requirements for signing
Use a current version of Chrome, Firefox, Safari, or Edge on Windows 10 or later, macOS, iOS, or Android. signNow mobile apps support completing and signing the Authorization For Release Of Information Form from supported mobile devices.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows 10+, macOS, iOS, Android Mobile signing signNow mobile apps
Organizations handling protected information should manage devices, browser updates, and account permissions centrally. Enterprise deployments may also require API access, SSO provisioning, managed mobile devices, or certificate and long-term-validation settings selected according to the organization’s security and retention policy.
How the audit trail records authorization
signNow records identity, timing, document integrity, and retrieval events while an Authorization For Release Of Information Form is signed.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Link events:
Export trail:
Risks of an incomplete authorization
Invalid disclosure
Unnecessary exposure
Privacy incident
Weak evidence
Unauthorized access



Processing stages for signed authorizations
The processing sequence depends on signer availability, required authentication, and the organization’s disclosure review, rather than a form-specific federal filing deadline.
Prepare the document
Deliver to signer
Complete signer review
Complete and archive
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting authorization workflows
Resolve field, consent, authentication, plan, and retention questions before releasing information under the completed authorization.
Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, and SOC 2 controls. For healthcare workflows, signNow states HIPAA compliance requires a business associate agreement. Confirm your organization’s plan and BAA requirements before sending protected health information.
Business Premium includes bulk send and quick invite links, which can help distribute the same authorization to multiple intended signers. Review each recipient and authorization scope individually; bulk delivery should not replace recipient verification or disclosure review.
The sender uploads the form, reviews auto-detected fields, assigns signer roles, and sends the document. The signer opens the email or link, reviews the authorization scope, completes required fields, and receives a completed copy after signing.
For consumer-facing electronic records, ESIGN requires disclosure of paper-record rights, electronic access capability, and procedures for withdrawing consent under 15 U.S.C. §7001(c). Configure the workflow and disclosures before requesting the authorization signature.
Business Premium lists bulk send, kiosk mode, request payments, and quick invite links. Enterprise adds advanced signer authentication, formula fields, and conditional fields. Select authentication based on the authorization’s privacy risk and organizational policy.
Export the completed authorization and audit trail after signing, then store them in an access-controlled repository. For HIPAA-covered documentation, evaluate the six-year rule in 45 CFR §164.530(j) and any longer state or organization retention requirement.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.