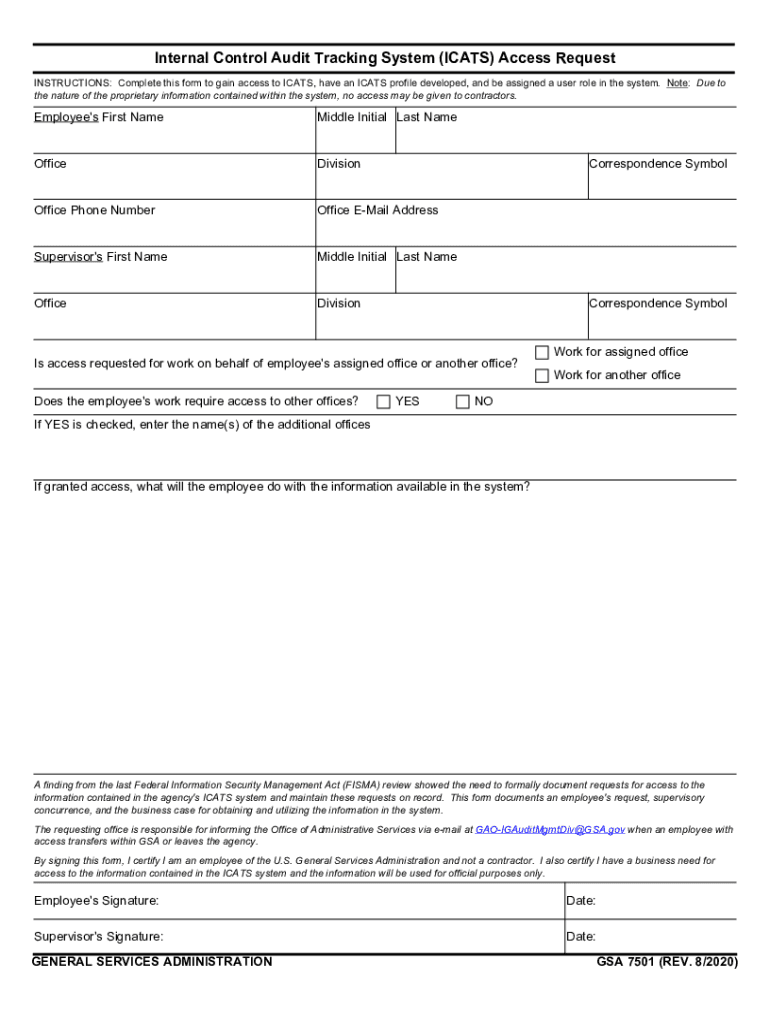
Internal Control Audit Tracking System Icats Access Request Gsa
Use a Internal Control Audit Tracking System ICATS Access Request GSA 2020 template to make your document workflow more streamlined.
What this access request does
The Internal Control Audit Tracking System Icats Access Request Gsa records a request for controlled access and the approvals supporting that request. Because no issuing agency, field list, deadline, or universal retention period is provided, the responsible organization must confirm its internal instructions before completion. In signNow, an administrator uploads the document, reviews detected fillable fields, assigns authorized requesters and approvers, sends the document, and stores the completed copy with its audit trail. ESIGN and UETA can support electronic execution when intent, consent, attribution, and reproducible records are established.
Who uses this access request
Government access
Federal agencies and contractors can use the request to document controlled access to systems, files, or operational resources.
Business administration
Corporate administrators can route requests to managers, security reviewers, and records teams before granting permissions.
Complete the access request in four steps
Prepare the Internal Control Audit Tracking System Icats Access Request Gsa, route it to authorized reviewers, and preserve the completed record.
Upload document:
Upload the current access request document to signNow for field recognition. Check fields:
Review detected fields and correct labels, recipients, and required approvals. Assign participants:
Add authorized requesters and approvers in the required signing order. Send and store:
Send the request, monitor completion, and retain the signed record.
Choose the right sending and signing method
- Use the web app when an administrator prepares the Internal Control Audit Tracking System Icats Access Request Gsa, maps fields, and sends it through an established approval sequence.
- Use the mobile app when an authorized requester or reviewer must inspect and sign the access request from an iOS or Android device.
- Use kiosk mode for supervised, on-site completion when staff share a controlled workstation and administrators need to manage the signing session.
- Use a shareable signing link when approved recipients need direct access without a separate email invitation, while retaining the link’s access controls.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features that support this access request
signNow combines field preparation, controlled routing, electronic signatures, audit evidence, templates, mobile access, and storage integrations for this request.
Field recognition
Upload the Internal Control Audit Tracking System Icats Access Request Gsa and review detected fields before routing it to authorized participants.
Approval routing
Place requesters, reviewers, and approvers in a controlled sequence so each person completes the responsibility assigned to them.
Audit trail
Capture signer actions, timestamps, and document history to support later review of the completed access request.
Reusable templates
Use templates to preserve recurring access-request language while requiring administrators to confirm each request’s current details.
Mobile signing
Let authorized participants review and sign from desktop or mobile devices when the organization permits remote completion.
Record integrations
Connect the completed request with approved storage or systems through integrations such as Microsoft 365, Google Drive, Box, or NetSuite.
Configure the request workflow
Configure authentication, signatures, audit evidence, retention, encryption, and access permissions before routing this request.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS 2FA |
| Signature type | Legally binding electronic signature |
| Audit trail | Enable detailed signing history |
| Document retention | Follow the approved agency schedule |
| Encryption | TLS 1.2/1.3 and AES-256 |
Find and fill out the correct internal control audit tracking system icats access request gsa
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| GSA 7501 2020 | 4.8 Satisfied (219 Votes) | |
| GSA 7501 2019 | 4.7 Satisfied (105 Votes) |
How the audit trail records activity
The audit trail separates the access request’s approval evidence from the document fields and preserves activity for later administrative review.
Authenticate signer:
Capture timestamps:
Protect document:
Seal evidence:
Retrieve history:
Export trail:
Platform requirements for this request
Prepare the Internal Control Audit Tracking System Icats Access Request Gsa in Chrome, Firefox, Safari, or Edge on Windows or macOS; signNow also provides iOS and Android mobile apps.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile access iOS and Android mobile apps
Organizations should use managed devices, approved identity controls, and role-based access for this request. Enterprise deployments may also require SSO provisioning, API access, and documented certificate or long-term-validation settings based on internal security policy.
Retain access requests with documented controls
The form has no stated universal federal retention period, so apply the schedule governing the underlying access record and preserve its audit evidence.
Export the signed record
Limit access by role
Standardize document naming
Confirm the governing schedule
Retention depends on the record context
Internal Control Audit Tracking System Icats Access Request Gsa has no stated universal retention period; use the rule governing its contents and purpose.
Organization-defined period
Six years where HIPAA applies
Three years for tax records
Three years after hire
As policy requires
Troubleshoot this access request
Resolve field, routing, evidence, retention, privacy, and plan questions before final approval of the Internal Control Audit Tracking System Icats Access Request Gsa.
Upload the source file again, then inspect detected fields before sending. signNow Business includes templates and audit trails, but field recognition still requires human review for this access request.
Add each authorized reviewer explicitly and confirm signing order. Business Premium adds bulk send and kiosk mode, while Enterprise adds conditional and formula fields for more complex routing.
Use signNow’s audit trail to review timestamps, signer actions, and document history. ESIGN and UETA support electronic signatures when intent, consent, attribution, and record reproduction are established.
Apply the organization’s approved retention schedule rather than assuming a universal period. HIPAA requires six years only when the record is subject to 45 CFR 164.530(j); unrelated access requests may follow another rule.
For protected health information, confirm that the selected signNow arrangement includes the required BAA. signNow identifies HIPAA compliance as requiring a BAA; do not transmit PHI before that requirement is satisfied.
Business is listed at $8 per user per month with annual billing and includes audit trails. Business Premium is $15 and adds bulk send; Enterprise is $30 and adds advanced signer authentication.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.