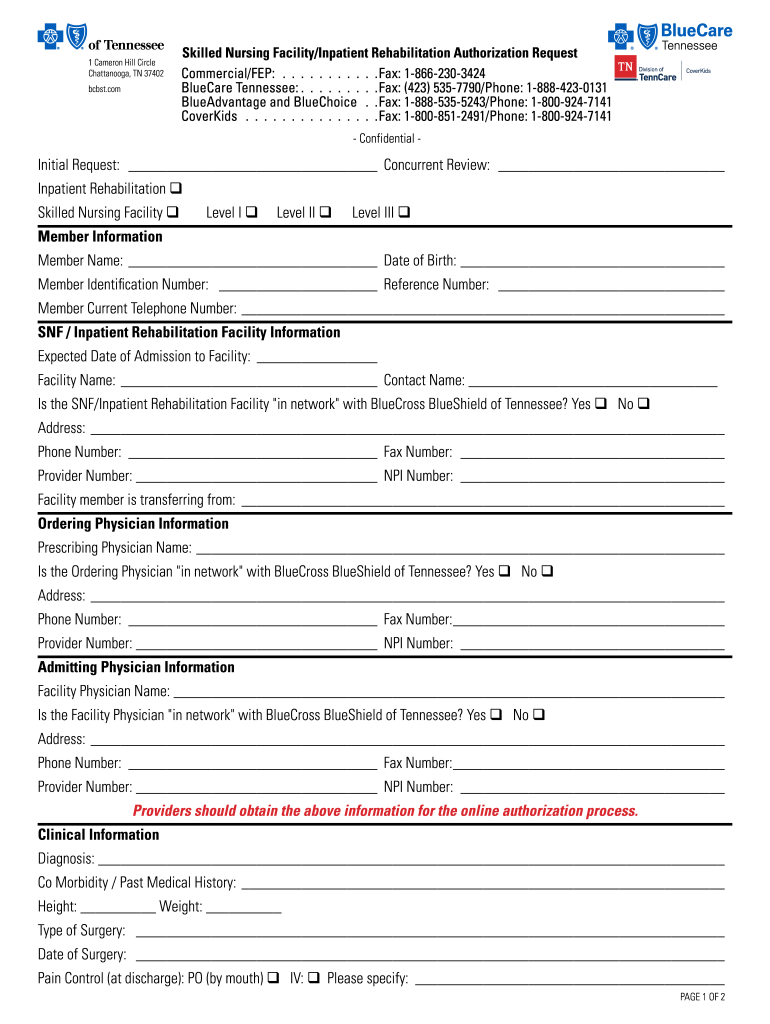
Tn Bcbs Skilled Nursing Facilityinpatient Rehabilitation Authorization Request
Use a TN BCBS Skilled Nursing FacilityInpatient Rehabilitation Authorization Request 2017 template to make your document workflow more streamlined.
About this rehabilitation authorization request
The Tn Bcbs Skilled Nursing Facilityinpatient Rehabilitation Authorization Request is a healthcare form used to request approval for skilled nursing facility or inpatient rehabilitation services. Staff complete patient, facility, provider, payer, clinical, service, and authorization-date information, then route the request to the responsible signer or reviewer. With signNow, the sender uploads the form, reviews auto-detected fields, assigns recipients, and sends it for electronic signature. The completed document and audit trail can then be retained with the patient’s authorization record under HIPAA and applicable state requirements.
Who uses this authorization request
Healthcare facilities
Admissions and utilization teams collect patient, facility, payer, provider, diagnosis, service, and date information before sending the request for authorization. They use the signed record to document the requested skilled nursing facility or inpatient rehabilitation services.
Payers and providers
Payers and referring providers review authorization details, confirm medical necessity information, and sign or approve the request through a controlled workflow. A complete audit trail helps staff identify who acted and when.
Healthcare teams that use this request
The request fits healthcare workflows where facility staff, providers, representatives, and payers must document approval for rehabilitation services.
A skilled nursing facility admissions team uses the request to gather patient, payer, provider, service, and authorization-date information before treatment begins or continues. A rehabilitation utilization-review department routes medical authorization requests to the correct payer reviewer, preserving signer identity, timestamps, and the completed record for later review. A multi-site healthcare enterprise uses shared templates, controlled permissions, and audit trails to standardize authorization requests across facilities without giving every employee unrestricted PHI access.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete the authorization request online
Use signNow to prepare the request, route it to the responsible healthcare signers, and preserve the completed authorization record.
Upload form:
Upload the authorization request and review detected fillable fields. Check fields:
Confirm patient, facility, provider, and authorization fields. Send request:
Assign signers and send the request securely. Store record:
Review the signed record and audit trail.
Recommended authorization request setup
Configure the request for protected health information, accountable signatures, and an exportable record of authorization activity.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for external healthcare signers |
| Signature type | Electronic signature with explicit consent |
| Audit trail | Capture signer identity, timestamps, and IP address |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2 or 1.3 in transit; AES-256 at rest |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for rehabilitation authorization records
Encryption in transit:
Encryption at rest:
HIPAA compliance:
Security certification:
Information security:
Activity evidence:
What the authorization audit trail records
The audit trail connects signer authentication, document integrity, and each authorization event so staff can review the completed request.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Build audit trail:
Export evidence:
Platform requirements for this request
Prepare the authorization request in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides iOS and Android apps for reviewing and signing assigned documents.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile apps iOS and Android signNow apps
Healthcare organizations should use managed devices, current browser security updates, and approved access controls when handling this request. Confirm that SSO, API access, and storage policies align with the facility’s HIPAA program and business associate agreement requirements.
Find and fill out the correct 2017 tn bcbs skilled nursing facilityinpatient rehabilitation authorization request
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| 2015 TN BCBS Skilled Nursing Facility/Inpatient Rehabilitation Authorization Request [2015-11] 2017 | 4.8 Satisfied (3555 Votes) | |
| 2015 TN BCBS Skilled Nursing Facility/Inpatient Rehabilitation Authorization Request [2015-11] 2015 | 4.8 Satisfied (95 Votes) |
Best practices for authorization requests
Accurate field review, controlled signing, restricted access, and documented retention reduce disputes around skilled nursing facility rehabilitation authorization.
Verify patient and authorization details before sending
Capture consent from the correct authorized signer
Preserve the signed document and audit trail together
Apply the HIPAA retention rule and exceptions
Retention periods for authorization records
Retain the completed request and supporting audit evidence under the applicable HIPAA, state, payer, and litigation-hold requirements.
6 years from creation or effective date
6 years for HIPAA documentation
Longer period when state law applies
Until a legal hold ends
Longer payer-required retention
Privacy pitfalls in authorization requests
Patient diagnoses, treatment details, and identifiers can appear in the completed request and require restricted access throughout routing and storage. Sending the request to the wrong representative can undermine consent evidence and delay authorization for skilled nursing facility rehabilitation services. Leaving payer, service dates, or facility fields blank can produce an incomplete request that requires correction before review. Sharing a completed authorization outside approved healthcare channels can expose protected health information and complicate HIPAA compliance documentation.
Risks from incomplete authorization records
Authorization dispute
Missing consent
PHI disclosure
Incomplete record
Legal standing of the authorization record
An electronically signed authorization request can provide admissible evidence when the signer shows intent, consents to electronic records, can be attributed to the signature, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable state UETA rules support electronic signatures, but they do not replace separate requirements for wills, court filings, family-law decrees, or other excluded records.



Troubleshooting authorization requests
Resolve field, signer, plan, authentication, HIPAA, and retention issues before releasing the completed rehabilitation authorization record.
On the Business plan, upload the request again and inspect auto-detected fields before sending. Correct field types, required status, recipient assignment, and page placement manually; an incomplete field map can prevent the intended signer from completing the authorization.
Use signNow’s recipient routing to assign the patient or authorized representative, referring provider, facility representative, and payer reviewer in the required order. Confirm every email address before sending because the request contains protected health information.
Business includes legally binding eSignatures and audit trails. For a HIPAA workflow, signNow identifies HIPAA compliance as requiring a BAA; confirm the organization’s plan, BAA, access controls, and clinical privacy procedures before processing PHI.
Business is listed at $8 per user per month with annual billing. Business Premium is $15 and adds bulk send, while Enterprise is $30 and adds advanced signer authentication; monthly prices are higher than annual pricing.
Use SMS OTP or another configured authentication method when the authorization requires stronger signer attribution. signNow’s compliance information describes 2FA, timestamps, and document history; select controls that match the facility’s risk assessment.
Export the completed authorization and audit trail after all required parties sign. Preserve them together under the facility’s retention schedule; HIPAA 45 CFR 164.530(j) requires six years from creation or the last effective date for covered documentation.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.