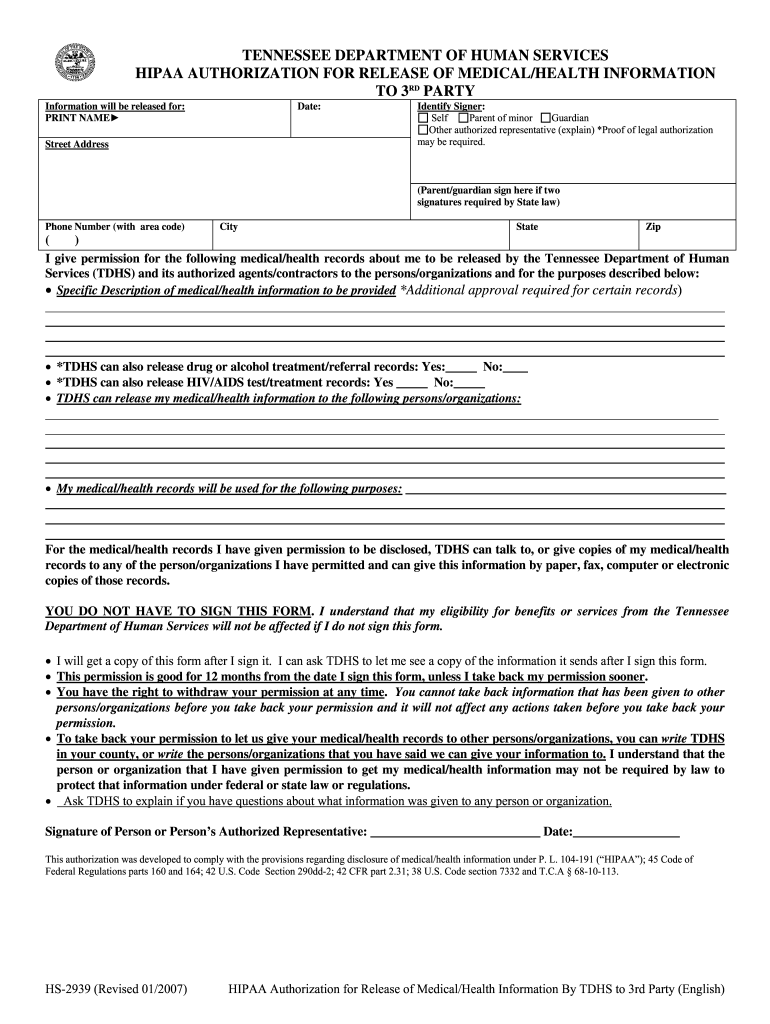
Tn HIPAA Authorization Form
Get the Tn Hipaa Authorization Form 2007 template, fill it out, eSign it, and share it in minutes.
What the Tn HIPAA Authorization Form does
The Tn HIPAA Authorization Form is a written permission document that lets a covered entity or business associate disclose specified protected health information to a named person or organization. It identifies the information, purpose, recipient, and expiration or revocation terms required by HIPAA 45 CFR 164.508. With signNow, upload the form, review detected fields, assign signer roles, send it by email or link, and retain the completed document with its audit trail. A business associate agreement is required for signNow’s HIPAA-compliant use.
Features for Tn HIPAA Authorization Form
signNow connects form preparation, controlled signing, audit evidence, and protected storage for healthcare authorization workflows.
Field detection
Upload the Tn HIPAA Authorization Form and review signNow’s detected fields before assigning patient, provider, or representative signature and date fields.
Signer routing
Route the authorization to named recipients by email or signing link, keeping each signer’s role and document access visible in the workflow.
Audit trail
Capture timestamps, signer actions, and document history in an audit trail that can accompany the completed authorization during compliance review.
Protected data
Use signNow encryption for protected information in transit and at rest, with HIPAA compliance available when the required BAA is in place.
Reusable templates
Reuse an approved authorization template while preserving the disclosure details, purpose, expiration, and recipient fields required for each request.
Mobile completion
Complete the authorization from a desktop or mobile device, then retain the signed document and audit trail under the covered entity’s policy.
How Tn HIPAA Authorization Form works
The signNow workflow moves the Tn HIPAA Authorization Form from upload through field review, signature collection, and documented storage.
Upload: Upload the authorization document Prepare: Review detected fields and recipients Send: Send for patient or representative signature Archive: Store the signed record with audit trail
Complete the authorization in signNow
Follow these document-specific steps to prepare, send, sign, and preserve the Tn HIPAA Authorization Form.
Upload form:
Upload the current Tn HIPAA Authorization Form into signNow. Review fields:
Check detected fields, disclosure details, and signer assignments. Send request:
Send the authorization to the named recipient or signer. Store record:
Confirm completion and save the signed record with its audit trail.
Recommended workflow setup
Configure the Tn HIPAA Authorization Form workflow around signer identity, audit evidence, protected transmission, and HIPAA retention requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS authentication |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps and signing actions |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for protected health information
HIPAA compliance:
Transit encryption:
Stored encryption:
Security certification:
Management certification:
Signer authentication:
What the signNow audit trail records
The audit trail provides evidence of who handled the authorization, when actions occurred, and how the completed record was preserved.
Authenticate signer:
Capture timestamps:
Record document history:
Seal completion:
Link evidence:
Export audit trail:
Find and fill out the correct tennessee form hipaa release
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2007 TN HS-2939 [2007-01] 2007 | 4.8 Satisfied (22045 Votes) |



Record-keeping practices for HIPAA authorizations
Treat the signed authorization, audit trail, access controls, and retention schedule as one controlled healthcare record.
Apply the HIPAA six-year retention rule
Export the audit trail with the document
Restrict access to authorized personnel
Validate required authorization elements
Tn HIPAA Authorization Form retention schedule
Retain the signed authorization and related documentation according to HIPAA’s six-year rule, while checking state and organizational requirements.
Six years for HIPAA authorizations
Six years for privacy documentation
Six years for disclosure records
Six years for authorization policies
Six years for compliance records
Risks of incorrect authorization handling
Missing required elements
Wrong recipient
Incomplete audit trail
Improper access
Privacy pitfalls in HIPAA authorization workflows
A broad disclosure description can authorize more protected health information than the patient intended, weakening purpose-specific consent under HIPAA 45 CFR 164.508. Sending a signing link to an unintended email address can expose protected health information and create an access-control incident requiring privacy review. Omitting the authorization’s expiration date or event can make the disclosure record incomplete under HIPAA’s authorization requirements. Storing the signed form outside an access-controlled repository can expose patient information even when the signature itself was valid.
Legal standing of the authorization
A completed Tn HIPAA Authorization Form can provide documented permission when it meets HIPAA 45 CFR 164.508 and applicable privacy procedures. Electronic signing may be recognized under ESIGN and UETA when intent, consent, attribution, and record retention are established. These frameworks exclude wills, certain court orders, and specified family-law documents.

Troubleshooting HIPAA authorization workflows
Resolve signing, privacy, and compliance questions before sending a Tn HIPAA Authorization Form through signNow.
Why does a HIPAA authorization fail after signing? signNow preserves the completed document and audit trail, but HIPAA authorization content must still satisfy 45 CFR 164.508, including the requested information, purpose, and recipient. Review the form fields before sending and confirm the authorization is specific and unexpired.
Does signNow Business include HIPAA compliance automatically? signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm that the selected account and deployment include the required BAA before handling protected health information, and configure access controls, authentication, and retention policies for the covered workflow.
Why can a signer not open the authorization link? Check whether the invitation expired, the recipient address is correct, or the signer is blocked by an organization policy. signNow supports email invitations and signing links; resend the request after verifying the recipient and authentication requirements.
How should a patient withdraw an electronic authorization? A signNow workflow can record the signed authorization and its audit trail, but withdrawal procedures come from the covered entity’s HIPAA process and the authorization language. Route the request to the designated privacy contact and preserve the original record.
What if the form contains an incorrect recipient or purpose? Do not rely on an amendment that obscures the original authorization. Void the pending request, correct the recipient or purpose, and send a new version in signNow so the audit trail clearly identifies the final document and signing events.
Can signNow store the completed HIPAA authorization securely? signNow states that its HIPAA compliance requires a BAA and uses encryption in transit and at rest, including TLS 1.2/1.3 and AES-256. Export the completed document and audit trail when required, then apply the covered entity’s retention policy.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.