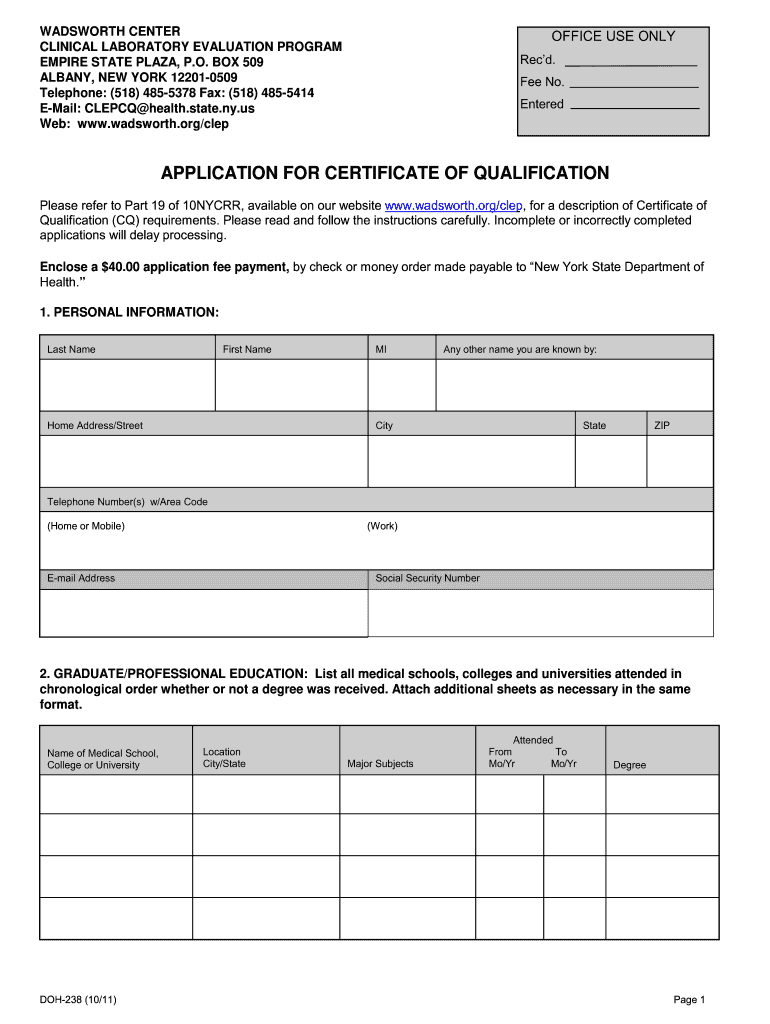
Application Certificate Qualification
Get the Application Certificate Qualification 2011 template, fill it out, eSign it, and share it in minutes.
What this qualification application does
Application Certificate Qualification records the information and approvals needed to assess an applicant for a certificate. In signNow, the sender uploads the document, uses automatic field detection where available, checks the required entries, and routes the application to the appropriate signer or reviewer. Recipients can complete designated fields and sign electronically, while the resulting record preserves the completed document and audit trail. U.S. electronic transactions generally receive legal recognition under ESIGN and applicable state law, subject to document-specific exceptions and required consent.
Who uses this qualification application
Certificate applicants
Businesses and professional practices use the Application Certificate Qualification to collect applicant information, supporting certifications, and approvals before issuing or reviewing a certificate. signNow can route fields to applicants, reviewers, and authorized approvers while preserving the completed record and audit trail.
Reviewing organizations
Compliance, operations, and administrative teams use the application when several people must review or approve the same qualification record. Role-based routing, templates, and audit-trail retrieval help separate data entry from verification and final approval.
Complete this application in signNow
Use this sequence to prepare, route, sign, and retain the Application Certificate Qualification without repeating information between participants.
Upload form:
Upload the Application Certificate Qualification. Detect fields:
Let signNow detect fillable fields. Assign fields:
Review and assign applicant fields. Send request:
Send the application for signature. Store evidence:
Store the signed record and audit trail.
Choose the right signing method
- Use the web app when preparing the Application Certificate Qualification on a desktop, placing fields, reviewing entries, and sending it through a controlled workflow.
- Use the mobile app when completing or reviewing the Application Certificate Qualification away from a desk, including signature tasks handled from iOS or Android.
- Use kiosk mode when an administrator supervises in-person completion of the Application Certificate Qualification on a shared device without distributing individual accounts.
- Use a shareable signing link when recipients need flexible access to the Application Certificate Qualification through a controlled URL instead of individualized email invitations.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Authentication options for certificate qualification
PKI foundation:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit evidence:
Platform requirements for this form
Application Certificate Qualification can be prepared in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow mobile apps support iOS and Android, while TLS 1.2 or TLS 1.3 protects connections during document access and signing.
Browser support Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, and Android Secure connection TLS 1.2 or TLS 1.3 connections
Organizations should also confirm managed-device policies, network access, and identity controls before deployment. API access, SSO provisioning, and certificate or long-term-validation configuration depend on the selected signNow plan and the organization’s compliance requirements.
Find and fill out the correct abmmmmb form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2011 DOH-238 [2011-10] 2011 | 4.8 Satisfied (11390 Votes) |
Recommended qualification workflow setup
Configure the Application Certificate Qualification around controlled access, attributable signatures, complete audit evidence, and secure handling of the finished record.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Use SMS OTP and admin-controlled user access |
| Signature type | Use an electronic signature with recorded intent |
| Audit trail | Enable audit-trail capture and export |
| Document retention | Retain signed records under organizational policy |
| Encryption | Use TLS 1.2 or TLS 1.3 in transit |
Best practices for this qualification
Accurate field assignment, proportionate authentication, and organized records help keep each qualification application reviewable from preparation through approval.
Verify applicant information before sending
Assign every field to its responsible person
Match authentication to application risk
Preserve the completed record and audit trail
What the audit trail records
The audit trail connects the applicant’s actions, identity checks, timestamps, and final Application Certificate Qualification record for later review.
Authenticate signer:
Capture timestamp:
Hash document:
Seal document:
Log actions:
Export evidence:
Risks in incomplete qualification records
Consent gap
Signer attribution
Missing fields
Lost audit trail
Privacy and disclosure pitfalls
Placing applicant identity details in unrestricted fields can expose personal information beyond the people reviewing the qualification application. Failing to capture electronic consent may weaken evidence that the applicant agreed to use electronic records for this transaction. Assigning approval fields to the applicant instead of the reviewer can obscure responsibility for the qualification decision. Retaining the signed application without its audit trail can make later reconstruction of the signing event more difficult.
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting qualification applications
These answers address access, authentication, compliance, usage limits, and evidence questions that can arise while processing an Application Certificate Qualification.
On the Business plan, signNow provides legally binding eSignatures, templates, mobile apps, and audit trails for routing this application. Check that required fields are assigned before sending, then review the recipient’s access method if the invitation cannot be opened.
The Business plan includes 100 signature invites per user per year, with overage fees. If repeated Application Certificate Qualification requests exceed that allowance, review usage or consider Business Premium, Enterprise, or a Site License based on volume.
signNow states that its eSignature service complies with ESIGN and UETA. Legal effect still depends on intent, consent, attribution, and record retention. For consumer-facing transactions, review the electronic-record disclosure requirements in 15 U.S.C. §7001(c).
If the qualification application contains protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm that the selected arrangement includes the required BAA before routing any PHI through the workflow.
Use SMS OTP or ID verification when email-only access does not provide enough identity evidence for the qualification decision. Advanced signer authentication availability depends on the selected signNow plan and configuration.
If a completed application is disputed, retrieve the signed document and its audit trail together. The audit trail records actions and timestamps, while the signed record preserves the applicant’s submitted information and signatures.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.