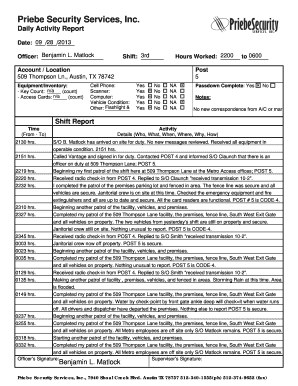
Security Daily Activity Report Form
Use a Security Daily Activity Report Example template to make your document workflow more streamlined.
What the Security Daily Activity Report records
A Security Daily Activity Report Form records what security personnel observed and did during a defined shift or day. It commonly captures the reporting employee, date, shift hours, patrol or checkpoint activity, incidents, visitors, equipment concerns, follow-up actions, and supervisor approval. In signNow, a sender uploads the form, places or confirms fillable fields, assigns completion and signature fields, and sends it to the responsible guard or manager. Completed records can be stored with the signed document and audit trail, creating a consistent electronic record for internal review, client reporting, and operational follow-up.
Businesses that use daily security reports
Security contractors, facility operators, and enterprise security teams use this form to document shift activity consistently and preserve supervisory review.
Security contractors use the form to document guard shifts, patrol checkpoints, incidents, and client-facing follow-up actions across managed properties and facilities. Facility operators use recurring reports to track access events, observed hazards, equipment concerns, and supervisor approvals for one site or multiple locations. Enterprise security departments use templates, delegated sending, and audit trails to standardize daily reporting while limiting sensitive operational details to authorized personnel.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key features for security activity reports
signNow features help security teams standardize daily entries, route approvals, and preserve evidence without rebuilding the report for every shift.
Structured fields
Capture officer identity, date, shift hours, patrol activity, incidents, equipment status, and follow-up actions in one repeatable report structure.
Role-based signing
Route the report to the guard first and supervisor second, keeping completion and approval responsibilities distinct.
Reusable template
Use a saved template to preserve field placement and required information across recurring daily reports.
Audit trail
Record signer actions, timestamps, delivery events, and document history for later operational review.
Mobile completion
Complete assigned reports from signNow mobile apps when security personnel work away from a desktop.
Data protection
Protect report data with encryption in transit and at rest, supported by signNow compliance controls.
Steps to complete the report online
Use this sequence to turn a blank Security Daily Activity Report Form into a completed, signed operational record in signNow.
Upload form:
Upload the blank Security Daily Activity Report Form. Place fields:
Add officer, shift, incident, and approval fields. Assign roles:
Assign completion and signature fields to recipients. Complete report:
Review, sign, and submit the completed report.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the report audit trail works
The signNow audit trail records the technical events that connect each completed Security Daily Activity Report Form to its signer and final file.
Authenticate signer:
Capture timestamps:
Hash document:
Seal document:
Log activity:
Export trail:
Recommended report workflow setup
Configure the Security Daily Activity Report Form around authenticated signing, controlled access, audit evidence, and secure handling of completed daily reports.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail and retention | Export completed report and audit evidence |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
| User provisioning | Role-based access with delegated sending |
Privacy controls for daily activity reports
Signed reports may expose employee names, patrol locations, incident details, or access information beyond the intended security management audience. Missing consent language can create uncertainty when reports include visitor information, surveillance references, or personally identifiable incident descriptions. Unrestricted sharing links may allow unauthorized users to view daily activity reports containing sensitive facility or personnel information. Unclear retention and deletion ownership can leave completed reports stored longer than business, contractual, or privacy requirements justify.
Security protections for signed reports
Data in transit:
Data at rest:
Control assurance:
Security management:
Protected information:
Privacy compliance:
Platform requirements for report completion
Complete the Security Daily Activity Report Form through Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow also provides mobile apps for iOS and Android, allowing security personnel to review and complete assigned reports away from a desk.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile systems iOS and Android mobile apps
Organizations should use managed Windows, macOS, iOS, or Android devices when reports contain facility details, employee information, or incident descriptions. Administrators can also evaluate signNow API access, SSO provisioning, and certificate or long-term validation requirements before deploying the workflow across multiple security locations.



Troubleshooting signed security reports
These answers address field assignment, authentication, compliance, and record-integrity questions for Security Daily Activity Report Form workflows.
Upload the original Security Daily Activity Report Form again and confirm that text is selectable. signNow can place fields manually when automatic field detection does not identify blank lines, checkboxes, or signature areas correctly.
The signNow Business plan includes templates and audit trails, while Business Premium adds bulk send. If recurring reports require sending to many guards, confirm the selected plan and invitation allocation before deployment.
Use signNow role assignments to separate the guard’s completion fields from the supervisor’s approval field. Recheck recipient order and permissions before sending, because an incorrect role can expose or lock fields.
For reports containing protected health information, signNow states that HIPAA compliance requires a BAA. Confirm the BAA and configure access, retention, and disclosure procedures before using the report for healthcare security operations.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. For consumer-facing records, follow the ESIGN disclosure requirements in 15 U.S.C. §7001(c).
If a completed report appears incomplete, open the audit trail and compare the signer’s actions, timestamps, and field history. Request a correction or send a new version rather than altering the signed record.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.