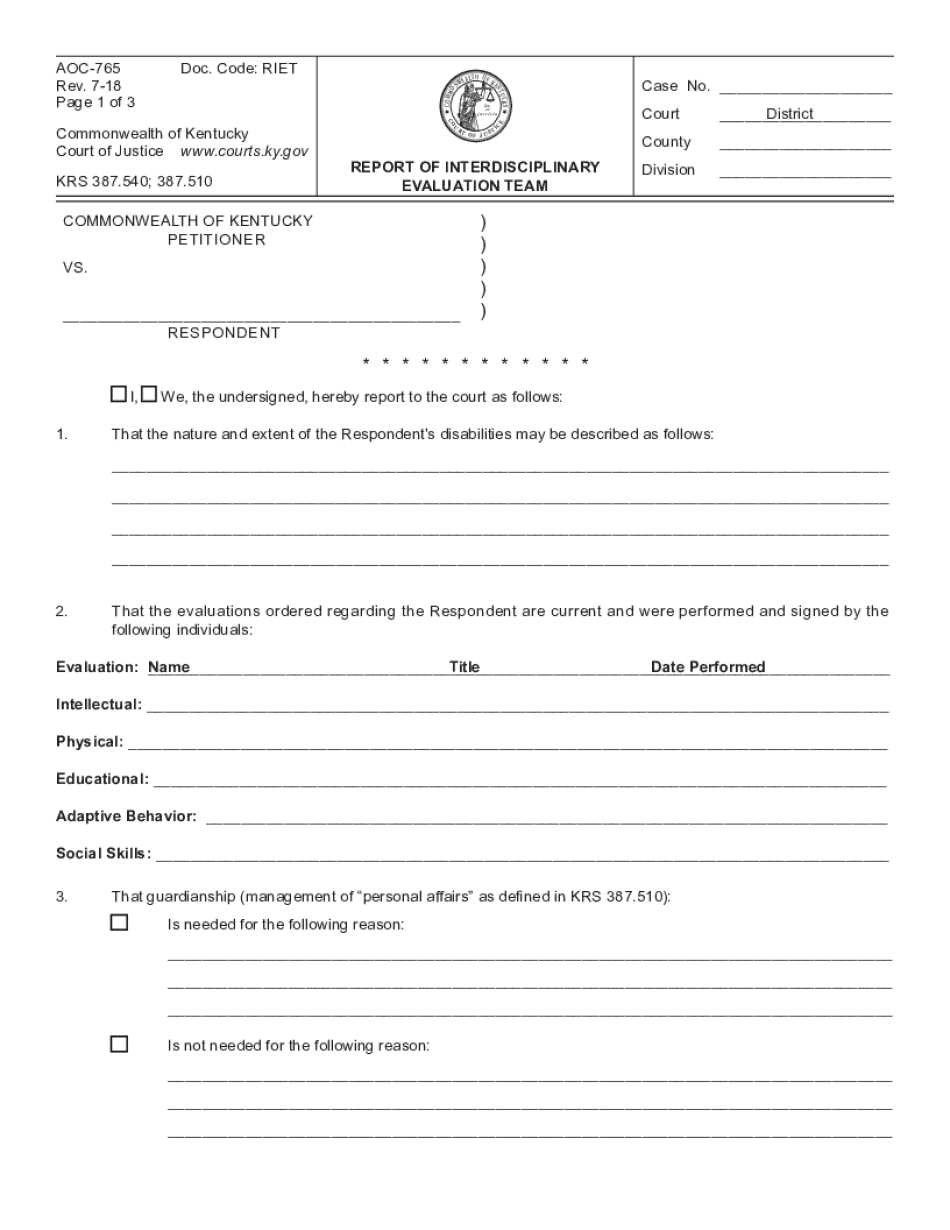
Code Riet
Use a Code RIET 2018 template to make your document workflow more streamlined.
What Code Riet is and how it works
Code Riet is a document name, but the supplied record does not identify an issuing agency, filing purpose, required fields, or statutory deadline. In signNow, upload the source file, review any detected fillable areas, add signer and date fields, and send it for completion. The signer reviews the record, provides consent and intent, and signs electronically. signNow records the transaction history and provides the completed document and audit trail. Confirm Code Riet’s governing authority and submission rules before relying on electronic execution.
Who may use Code Riet
Organizations
Organizations can use signNow to route Code Riet to designated reviewers, collect required signatures, and preserve the finished file with its audit trail. Because the supplied form name does not identify a specific agency or purpose, confirm whether the recipient, payer, regulator, or another authority requires additional fields or submission steps.
Individuals
Individuals can complete Code Riet when an authorized sender provides the document and signing instructions. Review every requested value before signing, confirm the intended recipient, and retain the final copy. signNow supports electronic completion, but it does not determine whether this particular document may be electronically filed.
How Code Riet moves through signNow
The signNow workflow keeps document preparation, signing, and evidence collection in one sequence for Code Riet.
Upload: Upload the source document Prepare: Review detected fields and add missing signer fields Send: Send Code Riet to its designated recipient Archive: Store the signed file and audit trail
Quick steps to complete Code Riet
Prepare Code Riet in signNow by checking fields, assigning the correct signer, and preserving the completed record.
Upload:
Upload the Code Riet document Check fields:
Let signNow detect fields, then correct or add them Assign signer:
Enter the signer’s email address Send:
Send and monitor completion
Recommended Code Riet workflow setup
Configure authentication, signing evidence, encryption, and retention around Code Riet’s verified legal purpose and recipient requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Legally binding eSignature |
| Audit trail | Retain completed signing history |
| Document retention | Follow the governing record rule |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security controls for Code Riet
Signer authentication:
Digital certificates:
Certificate format:
Account protection:
Identity checks:
Audit evidence:
Platform requirements for Code Riet
Use an up-to-date Chrome, Firefox, Safari, or Edge browser on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing Code Riet review and signing away from a desktop.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS Mobile systems iOS and Android
Organizations should also review managed-device controls, identity requirements, and retention policies before deployment. Enterprise teams may need SSO, API access, or stronger signer authentication; select those controls based on Code Riet’s actual data and governing authority.
Find and fill out the correct code riet
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| KY AOC-765 2018 | 4.8 Satisfied (2076 Votes) | |
| KY AOC-765 2010 | 4.8 Satisfied (2057 Votes) |
What the Code Riet audit trail records
The audit trail documents evidence around Code Riet’s signing event rather than replacing the form’s underlying legal or filing requirements.
Authenticate:
Timestamp:
Hash:
Seal:
Associate:
Export:
Best practices for Code Riet records
Use the document’s verified purpose and governing authority to control preparation, access, evidence, and retention for Code Riet.
Verify Code Riet’s issuing authority before sending
Export the audit trail with the completed record
Map retention to the governing authority
Limit access to authorized Code Riet participants
Retention periods to verify for Code Riet
Code Riet’s name does not identify a record class, so apply one of these periods only after confirming its tax, health, employment, or payroll context.
Three years: federal tax records
Six years: major tax understatement
Six years: HIPAA records
Three years: employment records
Three years: FLSA payroll records
Privacy and disclosure issues to check
Uploading Code Riet with unnecessary personal data can expose information to unintended recipients; remove irrelevant fields before sending and restrict access to authorized participants. Skipping the electronic-consent disclosure can weaken a consumer-facing transaction; provide the required paper-record and withdrawal information under 15 U.S.C. §7001(c). Sending a public signing link without recipient controls can permit an unintended person to access Code Riet; use named recipients or stronger authentication. Treating a completed signature as proof of filing can create a submission gap; confirm the actual Code Riet recipient, agency, or contractual destination separately.
Legal standing of Code Riet
A Code Riet eSignature may carry legal effect when the signer demonstrates intent, consents to electronic records, can be attributed to the signature, and the record remains reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA law. The supplied name does not establish whether a statutory exception applies, so verify the document’s purpose before relying on it.

Code Riet signing questions answered
Use these answers to resolve field, signer-access, compliance, and audit-trail questions before completing Code Riet in signNow.
Upload the original Code Riet file, then place fields manually if automatic detection does not identify its entry areas. signNow Business includes templates, audit trails, and legally binding eSignatures; verify every field before sending.
A recipient can sign Code Riet through an email invitation or signing link without creating an account in many workflows. Add SMS authentication when stronger attribution is needed, and retain the completed document with its audit trail.
The Business plan includes audit trails and legally binding eSignatures, while Business Premium adds bulk send. For a single Code Riet, prepare one template and send it to the designated signer rather than using bulk send.
Electronic signing generally requires intent, consent, signer attribution, and a reproducible retained record under ESIGN and applicable UETA provisions. signNow captures signing events in an audit trail, but the underlying Code Riet may have separate legal requirements.
If Code Riet contains personal or health information, limit access by role and confirm the applicable retention policy. signNow lists HIPAA compliance with a BAA requirement; HIPAA obligations depend on the parties and information involved.
If a signer cannot open Code Riet, resend the invitation, confirm the email address, and try a supported browser or signNow mobile app. Check authentication settings, because SMS or identity verification can block an incomplete verification attempt.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.