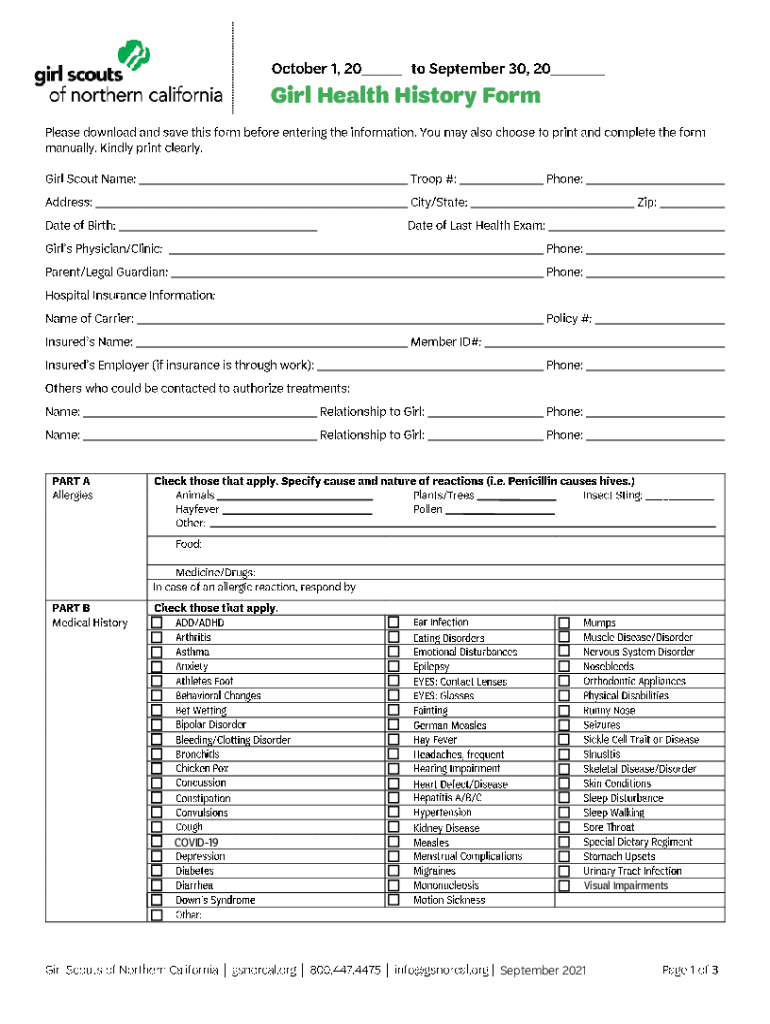
Health Information Privacy Statement
Use a Health Information Privacy Statement 2021 template to make your document workflow more streamlined.
What this privacy statement does
A Health Information Privacy Statement explains how an organization handles protected health information and records the individual’s acknowledgment or consent where required. The document may identify information practices, permitted disclosures, privacy rights, and the signer. In signNow, a sender uploads the statement, reviews or adds fillable fields, routes it to the authorized signer, and stores the completed record with an audit trail. HIPAA obligations depend on the organization and activity; electronic execution also depends on intent, consent, attribution, and reliable record retention under ESIGN and applicable state law, including UETA.
Who benefits from this privacy statement
The document is most useful when a healthcare organization must explain information practices, obtain documented consent, and preserve evidence of the patient’s response.
A solo medical practice can send the Health Information Privacy Statement before treatment or disclosure, collect patient consent remotely, and retain the signed record with its audit trail for controlled retrieval. A multi-site healthcare organization can use shared templates, role-based access, and delegated sending so registration teams collect consistent privacy acknowledgments without giving every employee administrative permissions. A healthcare enterprise can connect high-volume privacy workflows to its existing systems, apply stronger signer authentication where required, and coordinate retention and audit review across departments.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for health information privacy statements
signNow organizes completion, signer authentication, evidence capture, and protected storage around the specific consent and disclosure needs of this privacy statement.
Field detection
Upload the Health Information Privacy Statement, then use detected fields or add text, signature, initials, and date fields without rebuilding the document manually.
Signer routing
Send the privacy statement to each authorized signer in sequence or parallel, keeping signer responsibilities visible throughout the consent workflow.
Audit trail
Capture signer actions, timestamps, IP addresses, and document history so the completed statement has supporting evidence for later review.
Data protection
Protect health information in transit with TLS and at rest with AES-256 while applying access controls to completed privacy statements.
Mobile signing
Use mobile apps to collect signatures when staff and patients are not working from the same desktop or office location.
Integrations
Connect completed statements with approved business systems so teams can organize records without repeatedly downloading and re-uploading sensitive documents.
Recommended setup for this privacy statement
Use controlled signer authentication, documented consent, and protected retention for health information workflows.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Retention and encryption | Six years for HIPAA records; AES-256 at rest |
| User provisioning | Admin-managed roles with least-privilege access |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the audit trail records consent
The audit trail documents the technical events surrounding completion of the Health Information Privacy Statement, separate from preparing or routing the form.
Authenticate signer:
Capture timestamp:
Hash document:
Seal document:
Build audit trail:
Export evidence:
Find and fill out the correct health information privacy statement
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Girl CA 2021 | 4.8 Satisfied (1493 Votes) | |
| Girl CA 2021 | 4.8 Satisfied (204 Votes) | |
| Girl CA 2019 | 4.8 Satisfied (3037 Votes) |
Security and data protection
TLS 1.2/1.3 and AES-256:
HIPAA with BAA required:
SOC 2 Type II certified:
ISO 27001 certified:
GDPR compliant protections:
WCAG 2.0 Level AA:
Privacy risks when completing the statement
Including unnecessary diagnoses, treatment details, or identifiers can expose more protected health information than the privacy statement requires. A missing electronic-consent disclosure can weaken evidence that a patient agreed to receive and sign the statement electronically. Sending a statement through an unrestricted link can allow an unintended person to access private health information. Failing to preserve the signed document with its audit trail makes later verification of signer identity and consent timing more difficult.
Record-keeping practices for this statement
Retention, audit evidence, consent records, and restricted access should be managed together because this document can contain protected health information.
Set retention by governing record
Export audit evidence together
Archive protected copies securely
Record electronic consent clearly
Retention periods for related records
Keep the signed Health Information Privacy Statement according to the rule governing the record it documents. The applicable period can depend on the healthcare, tax, payroll, or safety context.
Six years for HIPAA records
Three years for tax records
Six years for major understatement
Three years for payroll records
Five years for injury records
Troubleshooting this privacy statement
These answers address field setup, signer authentication, HIPAA safeguards, electronic-consent evidence, plan limits, and retention for this statement.
On the Business plan, upload the Health Information Privacy Statement and review detected fields before adding signature, initials, date, and consent fields manually. Test the document in preview mode so a missing required field does not interrupt the signer’s session.
A HIPAA workflow requires a business associate agreement with signNow. The platform identifies HIPAA compliance as requiring a BAA, so confirm that agreement and your organization’s safeguards before sending health information through the workflow.
The Business plan is listed at $8 per user per month with annual billing and includes 100 signature invites per user annually. Review usage and applicable overage terms before sending high volumes of statements.
Use SMS OTP or another configured authentication control when email-only access does not provide enough assurance for the patient or organization. Document the selected control in the privacy workflow and preserve the resulting audit trail.
Electronic signatures generally require intent, consent to electronic records, attribution, and retention that permits accurate reproduction under ESIGN and UETA. Consumer-facing records may also require the disclosure elements in 15 U.S.C. §7001(c).
HIPAA requires covered documentation to be retained for six years from creation or its last effective date under 45 CFR §164.530(j). Apply the rule to the underlying record, then export and archive the completed statement and audit trail together.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.