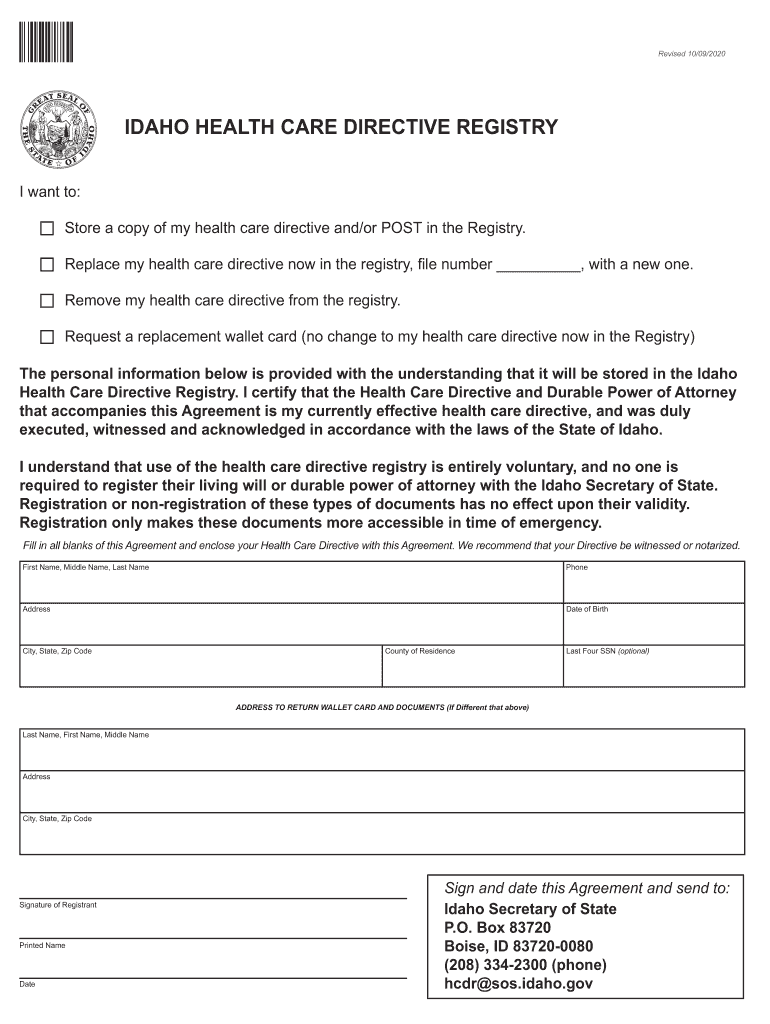
Store A Copy Of My Health Care Directive Andor Post In The Registry
Use a Store A Copy Of My Health Care Directive Andor POST In The Registry 2020 template to make your document workflow more streamlined.
What this health care directive does
Store A Copy Of My Health Care Directive Andor Post In The Registry is used to preserve a person’s signed health care instructions and make the record available to authorized recipients. In signNow, upload the directive, review automatically detected fields, add the signer, and send it for completion. The signer reviews the document and provides an electronic signature, while signNow records the signing event in an audit trail. The completed directive can then be retained or connected to authorized storage. State law may impose separate witness, notarization, registry, or disclosure requirements.
Who uses this health care directive
Individuals
Individuals organize a signed health care directive for personal records, family access, and future medical decision-making conversations.
Healthcare organizations
Healthcare organizations collect directive acknowledgments while applying HIPAA safeguards and preserving a clear signing record for authorized personnel.
Business types using this directive
The form is most useful where personal health instructions must be signed, shared with authorized parties, and preserved as a reliable record.
Solo estate-planning practitioners can prepare directive packets, collect client signatures, and retain completed records with an exportable audit trail for each matter. Regional healthcare practices can route patient directives to authorized signers, use HIPAA-compliant workflows with a BAA, and restrict access to designated staff. Enterprise hospital systems can connect directive workflows to existing platforms, apply administrator controls, and preserve signed records for coordinated patient-care processes.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for this health care directive
signNow combines document preparation, signer routing, audit evidence, encryption, and connected storage for a structured directive workflow.
Field detection
Upload the directive and let signNow identify fillable areas before you review names, dates, acknowledgments, and signature fields.
Flexible delivery
Send the prepared directive to the intended signer by email or signing link without rebuilding the document manually.
Audit trail
Capture signer actions, timestamps, and document history in an audit trail connected to the completed directive.
Mobile signing
Use mobile apps to review and sign the directive from supported iOS or Android devices.
Encrypted records
Protect health information with TLS 1.2/1.3 in transit and AES-256 encryption at rest.
System integrations
Connect completed directives with systems such as Box, Google Drive, Microsoft 365, NetSuite, or AWS.
Complete the directive in signNow
Use this sequence to prepare the specific health care directive, route it to the intended signer, and preserve its completed record.
Upload document:
Upload the directive PDF. Check fields:
Review detected fillable fields. Add signers:
Add authorized signers. Send for signing:
Send the directive for signature. Store records:
Store the completed copy and audit trail.
Recommended directive workflow setup
Configure the directive workflow around signer identity, protected health information, audit evidence, and the retention rule applicable to the record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled with certificate of completion |
| Document retention | Six years for HIPAA records (45 CFR §164.530(j)) |
| Encryption | TLS 1.2/1.3 and AES-256 encryption |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for health directive records
Data in transit:
Data at rest:
HIPAA safeguards:
Security certification:
Security management:
Privacy compliance:
How the audit trail records this directive
The audit trail documents who handled the health care directive, when each action occurred, and how the completed record can be reviewed later.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Complete certificate:
Export audit trail:
Find and fill out the correct store a copy of my health care directive andor post in the registry
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| ID Health Care Directive Registry 2020 | 4.8 Satisfied (1815 Votes) | |
| ID Health Care Directive Registry 2019 | 4.8 Satisfied (249 Votes) |



Platform requirements for this directive
Use signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, while TLS 1.2/1.3 protects the connection used to handle the directive.
Supported browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Secure connection TLS 1.2/1.3 connection required
Healthcare organizations should use managed devices, controlled accounts, and role-based access when handling this directive. Enterprise deployments may require API access, SSO provisioning, and a documented configuration for authentication, audit-trail retention, and secure archival.
Retention and record-keeping practices
A signed directive should remain accessible, reproducible, and protected throughout its useful legal and care-related life.
Match retention to the record’s legal category
Export the signed directive and audit trail
Restrict access to authorized recipients
Review changes before replacing copies
Retention periods for related records
Use the retention period tied to the directive’s actual record category; the health care record rule applies only when HIPAA-covered requirements govern it.
Six years for HIPAA records
Three years for tax records
Six years for major understatement
Three years for payroll records
Five years for injury records
State rules and excluded documents
State notarization
Wills and codicils
Court orders
Family-law documents
Real-estate deeds
Privacy and disclosure pitfalls
Uploading a directive with unnecessary diagnoses or identifiers can expose private health information to recipients who do not need it. Failing to capture electronic consent may weaken proof that the signer agreed to receive and sign the directive electronically. Giving every staff member download access can disclose a patient’s directive beyond the authorized care or administrative team. Replacing an older directive without checking revocation and distribution records can leave family members or providers relying on outdated instructions.
Legal standing and evidentiary value
An electronically signed health care directive may be recognized under ESIGN and applicable state UETA or New York ESRA rules when intent, consent, attribution, and record reproducibility are established. State-specific execution requirements still control. Wills, codicils, testamentary trusts, court orders, and family-law decrees remain excluded from these federal electronic-record rules.

Questions about signing this directive
These answers address signing, privacy, plan limits, and legal requirements that can affect this health care directive workflow.
Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR. For health information, HIPAA compliance requires a business associate agreement and appropriate configuration before sending this directive.
The Business Premium plan adds kiosk mode and quick invite links, while Enterprise adds advanced signer authentication. Choose the authentication level based on the directive’s privacy requirements and the identity evidence your organization must retain.
Consumer-facing healthcare records require electronic-record disclosures under 15 U.S.C. §7001(c), including paper-record rights, electronic access, and consent withdrawal procedures. Configure and present the disclosure before requesting the directive signature.
Use signNow’s audit trail and certificate of completion to preserve signer identity evidence, timestamps, and document history. ESIGN and UETA recognize electronic records when intent, consent, attribution, and reproducibility are established.
A directive requiring notarization cannot rely on an ordinary eSignature alone. Check the applicable state law and notary procedure; signNow’s signature workflow does not replace a required in-person or remote notarization session.
Business provides 100 signature invites per user annually when billed annually, with overage fees. The Site License is usage-based at $1.50 per signature invite for organizations handling 1,000 or more documents yearly.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.