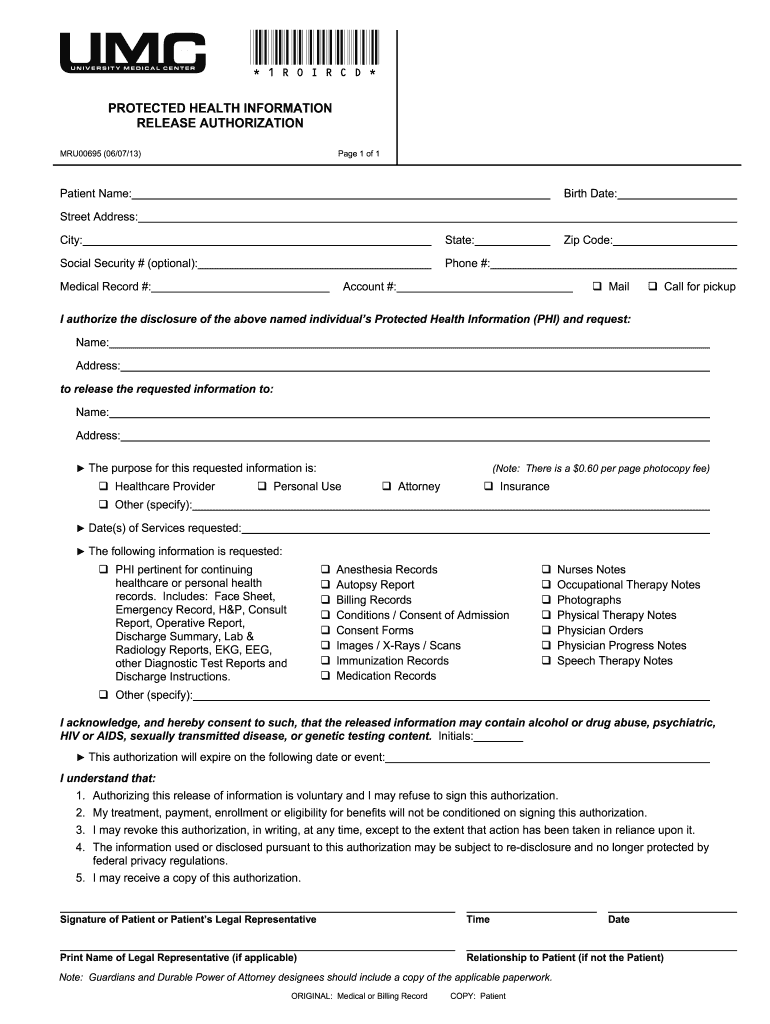
Las Vegas Nv Blank Hospital Release Form Umc
Create a custom Las Vegas Nv Blank Hospital Release Form Umc 2013 that meets your industry’s specifications.
What the UMC hospital release form does
The Las Vegas Nv Blank Hospital Release Form Umc is a patient authorization used to permit University Medical Center of Southern Nevada to disclose specified health information to an identified recipient. The completed form should identify the patient, requested records, recipient, purpose, authorization terms, and signature information. In a signNow workflow, staff upload the blank form, place fields, route it to the authorized signer, and retain the completed document with its audit trail. HIPAA governs disclosure handling; electronic signing also depends on consent, intent, attribution, and reproducible records.
Key features for UMC release forms
signNow connects the exact UMC authorization document with field preparation, signer routing, audit evidence, mobile access, and healthcare privacy controls.
Form preparation
Upload the blank UMC release form and place patient, recipient, purpose, date, and signature fields without recreating the hospital document.
Signer routing
Route the authorization to the patient or authorized representative through an email invitation or controlled signing link.
Audit evidence
Capture timestamps, signer actions, and completion evidence alongside the completed release for later review.
Mobile access
Use signNow’s mobile apps when approved staff need to review or route the UMC form from iOS or Android.
Record storage
Keep the signed PDF and certificate of completion together under the hospital’s approved records policy.
Healthcare controls
Apply HIPAA-related controls when protected health information is processed, including a required business associate agreement.
Complete the UMC release form
Use this sequence to prepare the Las Vegas UMC hospital release form, capture authorization, and preserve the signed record.
Upload form:
Upload the completed UMC release form. Review fields:
Check patient, provider, and disclosure fields. Add signer:
Add the authorized signer and recipient. Complete workflow:
Send, sign, and save the completed record.
How the UMC release workflow works
The workflow keeps the patient authorization, recipient details, and completed hospital release form together from preparation through secure archival.
Upload document: Upload the UMC hospital release form. Prepare fields: Place fields beside patient authorization details. Send securely: Route the release to authorized signers. Archive record: Store the signed PDF and audit trail.
Platform requirements for UMC forms
The Las Vegas UMC release form can be prepared in Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow mobile apps support iOS and Android, while TLS 1.2/1.3 protects data in transit.
Supported browsers Chrome, Firefox, Safari, and Edge on Windows or macOS. Mobile access signNow mobile apps for iOS and Android. Connection security TLS 1.2/1.3 protects data in transit.
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices, restrict access to authorized staff, and confirm that the selected signNow plan supports required authentication, audit-trail retention, and HIPAA workflows. A business associate agreement is required when signNow handles protected health information.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended UMC workflow setup
Configure the Las Vegas UMC release workflow around patient identity, narrow disclosure scope, auditability, and protected health information controls.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS or advanced signer authentication |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retain certificate and action history |
| Document retention | 6 years under HIPAA 45 CFR §164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
Security controls for UMC records
Stored data:
Transport security:
Health privacy:
Service controls:
Security management:
Privacy framework:
Find and fill out the correct las vegas nv blank hospital release form umc
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| UMC MRU00695 2019 | 4.8 Satisfied (62 Votes) | |
| UMC MRU00695 2016 | 4.8 Satisfied (6480 Votes) | |
| UMC MRU00695 2013 | 4.8 Satisfied (378 Votes) |
Audit trail steps for UMC releases
The audit trail records technical events that help connect the signer, completed UMC authorization, and retained evidence without changing the form’s healthcare requirements.
Authenticate signer:
Capture timestamp:
Link document:
Seal record:
Retrieve audit trail:
Control export:
Legal standing of electronic authorization
A completed UMC release may carry evidentiary value when the signer demonstrates intent, consents to electronic records, can be attributed, and the record remains reproducible under ESIGN, 15 U.S.C. chapter 96, and UETA. Those frameworks do not replace HIPAA authorization requirements or cover wills, court orders, and family-law decrees.

Nevada release form limitations
Missing patient consent
Incomplete authorization
Improper disclosure
Unnotarized deed
Retention periods for related UMC records
Match the signed release and its audit evidence to the longest applicable healthcare, tax, payroll, or occupational-record requirement.
Six years — health records
Three years — tax records
Six years — tax understatement
Three years — payroll records
Five years — injury records
Best practices for UMC authorization
Accuracy, narrow disclosure scope, complete records, and controlled access reduce errors when preparing this hospital release authorization.
Verify every UMC authorization field
Limit disclosure to stated recipients
Archive the complete release package
Control access to patient information
Privacy challenges with UMC releases
Listing an overly broad recipient or record category may disclose more protected health information than the patient intended to authorize. Leaving the purpose, expiration, or patient identifiers incomplete can make the UMC authorization difficult to validate during disclosure processing. Sending the signed release through an unapproved mailbox or storage location can expose protected health information outside hospital access controls. Failing to retain the completed PDF and audit trail can weaken the organization’s ability to reproduce the authorization and explain its disclosure decision.
Troubleshoot UMC release form workflows
These answers address field placement, signer access, healthcare privacy, plan capabilities, and the legal conditions surrounding electronic authorization.
signNow Business supports legally binding eSignatures, templates, mobile apps, and audit trails. For protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm the agreement and internal privacy review before sending patient records.
A typed or drawn signature can evidence intent under ESIGN and UETA when consent, attribution, and record retention requirements are met. If the hospital requires stronger identity proofing, use available authentication controls and document the policy applied.
Use signNow’s field placement tools to add signature, date, and text fields to the uploaded UMC form. Review every patient identifier, authorized recipient, purpose, and expiration field before sending; signNow cannot determine whether the medical authorization itself is legally complete.
The Business plan includes audit trails and templates. Business Premium adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication. Select the plan based on the hospital’s volume, identity controls, and approved HIPAA configuration.
If the signer cannot open the email, verify the address, resend the invitation, or provide a controlled signing link. Do not send the patient’s medical information through an unapproved channel; use hospital access-control procedures and retain the resulting audit trail.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and reproducible records are present. Those statutes do not replace HIPAA safeguards or hospital policy, and they do not make every healthcare disclosure valid without proper authorization.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.