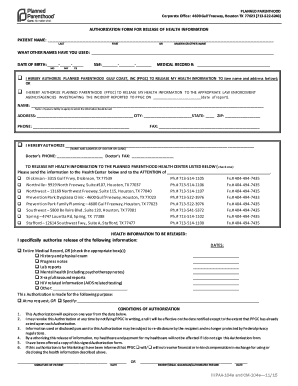
Attachment Es Authorization Form For Release Of Health Information Created
Use a Attachment ES Authorization Form For Release Of Health Information Created 2015 template to make your document workflow more streamlined.
What this health information authorization does
The Attachment Es Authorization Form For Release Of Health Information Created records a person’s permission for identified health information to be released to a named recipient for a stated purpose. The completed attachment should identify the information covered, authorization scope, signer, and any expiration terms shown on the form. In signNow, upload the attachment, review detected fields, route it to the signer, and preserve the signed document with its audit trail. HIPAA-covered records generally require six-year retention under 45 CFR §164.530(j).
Who uses this health information form
Healthcare providers
Healthcare providers, medical practices, and release-of-information teams use the attachment to document a patient’s permission before sending specified health information to a named person or organization. signNow adds fillable fields, signer routing, completion records, and an audit trail for the authorization workflow.
Patients and representatives
Patients and authorized representatives review the identified records, recipient, purpose, and expiration terms before signing. The completed attachment can accompany a controlled disclosure process, while signNow preserves evidence of the signing event and supports secure document handling.
Who benefits from this authorization workflow
The form is most useful where staff must obtain a clear patient authorization before releasing protected health information.
Solo medical practices can send the Attachment Es authorization to patients or designated representatives, collect signatures remotely, and preserve the completed release with its audit trail for records management. Hospital release-of-information teams can use reusable templates, role-based sending, and HIPAA-compliant signNow workflows when authorizations identify records, recipients, purposes, and expiration terms. Enterprise healthcare networks can connect authorization workflows to existing systems, provision users centrally, and apply consistent access controls across departments handling protected health information.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete the health information authorization
Use this workflow to prepare, sign, and retain the Attachment Es Authorization Form For Release Of Health Information Created.
Upload the attachment:
Upload the completed attachment and let signNow detect its fillable fields. Check the fields:
Review detected fields and add signature, date, and authorization fields. Add the signer:
Enter the authorized recipient’s email address and set signing order. Send and store:
Send the authorization, then download the signed copy and audit trail.
Recommended authorization workflow setup
Configure the Attachment Es authorization workflow around signer identity, protected health information, auditability, and HIPAA record retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Retain six years under HIPAA 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2 or 1.3 in transit |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Choose a signing method for this form
- Use the signNow web app when staff prepare the attachment, place fields, and send the authorization from a desktop workflow.
- Use the signNow mobile app when clinicians or release staff need to review and send the authorization from iOS or Android devices.
- Use kiosk mode when a patient or representative signs the authorization on an organization-controlled device during an in-person visit.
- Use a shareable signing link when a clinic needs to distribute the same authorization process through an approved patient or partner channel.
How the authorization audit trail works
The audit trail records evidence around the Attachment Es authorization without replacing the form’s substantive disclosure terms.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Export evidence:
Archive securely:
Find and fill out the correct attachment es authorization form for release of health information created
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Planned Parenthood Authorization Form for Release of Health Information 2015 | 4.8 Satisfied (733 Votes) | |
| Planned Parenthood Authorization Form for Release of Health Information 2011 | 4.8 Satisfied (1776 Votes) |
Security for health information authorizations
HIPAA protection:
Independent assurance:
Information security:
Stored document encryption:
Transport encryption:
Privacy frameworks:
Platform requirements for signing
Complete the Attachment Es Authorization Form For Release Of Health Information Created through Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow also provides mobile apps for iOS and Android, with TLS 1.2 or 1.3 protecting connections.
Browser support Chrome, Firefox, Safari, or Edge on Windows or macOS. Mobile access signNow mobile apps on iOS and Android devices. Connection security TLS 1.2 or 1.3 secures browser connections to signNow.
Healthcare organizations should manage Windows, macOS, iOS, and Android devices through approved policies. Enterprise deployments can connect signNow through API access, SSO provisioning, and managed identity controls. A HIPAA workflow requires a business associate agreement with signNow and organizational procedures for access, disclosure, and retention.



Privacy pitfalls when using this form
Sending the signed attachment to an unintended recipient can expose protected health information beyond the authorization’s stated disclosure scope. Leaving the purpose, records, expiration, or recipient incomplete can make the authorization unsuitable for the planned release. Allowing unrestricted staff access to completed authorizations can create an avoidable privacy and access-control weakness. Retaining only the signed page without its audit trail can weaken evidence of signer identity, timing, and document history.
Record-keeping practices for this authorization
Retain the signed attachment with evidence that the authorization was completed, delivered, and protected throughout its lifecycle.
Set retention using HIPAA and state rules
Export the audit trail with the document
Restrict access to protected information
Verify scope before releasing records
Troubleshooting this authorization workflow
Resolve field, signer, privacy, and retention questions before sending the Attachment Es authorization for release of health information.
A Business plan workflow can upload the attachment, place fields, send it for signature, and retain an audit trail. For protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement, so the organization should confirm the BAA before use.
Business is listed at $8/user/month with annual billing and includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, and SOC 2. Business Premium is listed at $15/user/month annually and adds bulk send and kiosk mode.
If detected fields are misplaced, inspect the uploaded PDF and manually adjust signature, date, and text fields before sending. Confirm that the recipient, purpose, records description, and expiration remain readable and correctly associated with the authorization.
A completed authorization should be stored with its audit trail rather than only as a downloaded PDF. signNow audit trails record actions and timestamps; healthcare organizations must also apply their HIPAA and state retention policies.
ESIGN and UETA generally support electronic signatures when intent, consent, attribution, and record retention are established. Consumer-facing electronic records may require the disclosure and access procedures in 15 U.S.C. §7001(c).
The signNow pricing reference lists 100 signature invites per user per year for subscription plans, with overage fees. Confirm the current allowance and any healthcare agreement terms before selecting a plan for recurring authorization volume.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.