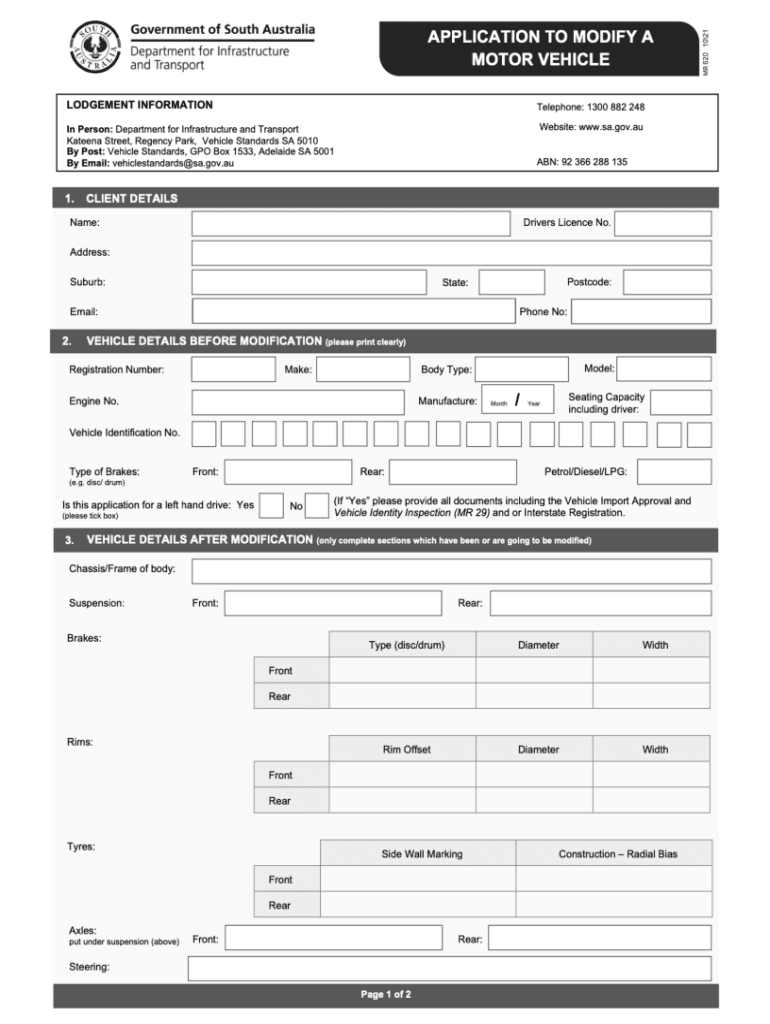
MR620
Use a Mr620 2021 template to make your document workflow more streamlined.
What MR620 is and how it works
MR620 is the specific form identified by that reference, completed by entering its required information and obtaining the signatures its instructions call for. Because the supplied form record does not identify an issuing agency, filing deadline, field list, or submission destination, those details must be confirmed from the authoritative MR620 instructions before completion. In signNow, a sender uploads the source file, reviews detected fillable fields, assigns signer roles, sends the document, and retains the completed copy with its audit trail. ESIGN and applicable state electronic-transaction law may support electronic signing when their requirements are satisfied.
How MR620 moves through signNow
MR620 follows a controlled digital workflow from document preparation through signature completion and audit-trail retention.
Upload document: Upload the MR620 file to signNow. Prepare fields: Review detected fields and add missing inputs. Send for signature: Assign signer roles and send securely. Store record: Complete signatures and retain the audit trail.
Risks of incomplete MR620 records
Disclosure exposure
Consent evidence
Access control
Evidence gaps
What the MR620 audit trail records
The audit trail records technical evidence around MR620 signing, separate from the form’s substantive answers and business review.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Audit history:
Trail retrieval:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended MR620 workflow setup
Configure MR620 around signer identity, electronic consent, audit evidence, secure transmission, and the retention rule governing the underlying transaction.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and action history |
| Document retention | Follow the transaction’s governing retention rule |
| Encryption | Use TLS in transit and AES-256 at rest |
Find and fill out the correct mr620
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| AU MR620 2021 | 4.8 Satisfied (1287 Votes) | |
| AU MR620 2013 | 4.8 Satisfied (1908 Votes) |
Best practices for completing MR620
A careful MR620 workflow combines source-file validation, controlled access, signer consent, and evidence preservation.
Validate every MR620 page before sending
Limit access to authorized MR620 recipients
Retain the form with evidence
Document electronic-record consent clearly
Security controls for MR620
Data in transit:
Stored data:
Service assurance:
Security management:
U.S. eSignature:
Protected health information:
Platform requirements for MR620
MR620 can be prepared in a supported desktop browser such as Chrome, Firefox, Safari, or Edge on Windows or macOS. Signers can also use signNow mobile apps on iOS or Android, subject to current app and operating-system support. Use an encrypted connection when uploading or signing.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Mobile signing signNow mobile apps
Organizations deploying MR620 at scale should confirm managed-device controls, identity provisioning, and any required API or SSO configuration with their signNow administrator. Regulated workflows should also verify access restrictions, audit-trail export, and retention controls before production use.



MR620 troubleshooting questions
These answers address document preparation, signer access, evidence, consent, plan selection, and mobile completion for MR620 in signNow.
Upload the authoritative MR620 file again and inspect every page after automatic field detection. signNow can identify fillable areas, but the sender remains responsible for correcting missing, misplaced, or incorrectly assigned fields before delivery.
Review the recipient address, signer order, and assigned fields. Send a fresh signNow invitation when the original link has expired or the wrong signer received it; retain the corrected completion record with the MR620 file.
Use signNow’s audit trail and completion certificate to review timestamps, delivery events, signer actions, and authentication details. Under ESIGN and UETA, these records help demonstrate intent and attribution but do not replace form-specific legal requirements.
For consumer-facing MR620 transactions, provide the ESIGN electronic-record disclosure and confirm access to the electronic format. The disclosure and consent requirements arise under 15 U.S.C. §7001(c), not from the signNow platform itself.
The signNow Business plan is listed at $8 per user per month with annual billing and includes audit trails and templates. Business Premium is $15 and adds bulk send; plan limits and overage terms should be reviewed before launch.
Signers can review and sign MR620 through signNow’s mobile apps or browser workflow. If a signer cannot access the document, verify the invitation, device connection, assigned fields, and authentication method before resending.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.