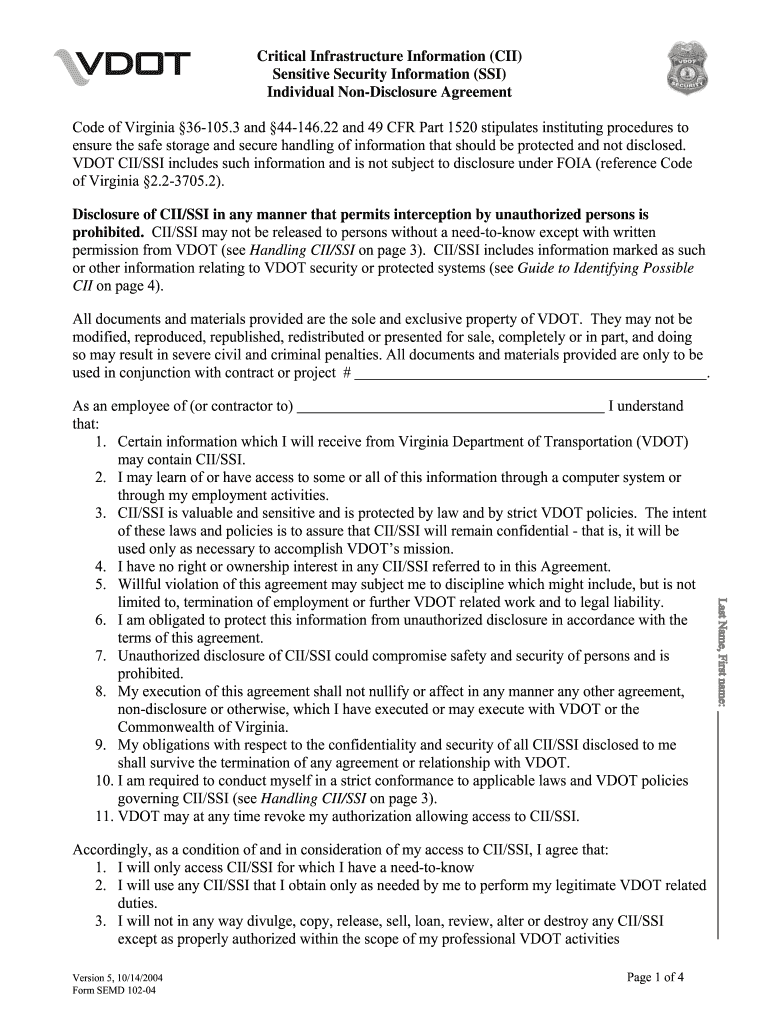
Vendor Confidentiality Statement For Access To Virginia Department Of Transportation Vdot Information And Security Systems V
Use the Vendor Confidentiality Statement For Access To Virginia Department Of Transportation VDOT Information And Security Systems V 2004 template to automate your RMV workflows and close deals faster.
What this VDOT confidentiality statement does
This statement records a vendor’s confidentiality obligations before access to Virginia Department of Transportation information and security systems. The vendor identifies its organization, authorized representative, access purpose, and covered VDOT information or systems, then signs to acknowledge restricted use and disclosure. The agency can use the completed record alongside contract and security approvals when deciding whether access is appropriate. It is not a substitute for VDOT authorization, least-privilege controls, background checks, or a separate agreement required by the project.
How the VDOT statement workflow works
The signNow workflow turns the VDOT confidentiality statement into a traceable electronic record from upload through controlled archival.
Upload: Upload the VDOT statement to signNow. Prepare: Review detected fields and add missing approvals. Send: Send it to the authorized vendor signer. Archive: Store the signed record with its audit trail.
What the VDOT audit trail records
A signNow audit trail shows how the VDOT statement moved from delivery to authenticated completion and controlled record retrieval.
Authenticate signer:
Capture timestamps:
Seal evidence:
Retrieve records:
Control retrieval:
Connect authorization:
Best practices for VDOT confidentiality access
Use precise system descriptions, verified signers, controlled disclosure, and complete records when preparing this VDOT vendor statement.
Limit disclosure to approved VDOT access
Describe systems and information precisely
Verify the authorized vendor signer
Preserve authorization evidence together
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for VDOT statements
Configure the workflow around verified signer identity, traceable completion evidence, controlled retention, and encrypted handling of VDOT information.
| Setting | Recommendation |
|---|---|
| Authentication method | Verified email with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with completed statement |
| Document retention | Follow VDOT records schedule |
| Encryption | TLS 1.2/1.3 and AES-256 |
Security for VDOT access records
Transport encryption:
Storage encryption:
Security certification:
Information security:
Electronic signatures:
Signer authentication:
Find and fill out the correct vendor confidentiality statement for access to virginia department of transportation vdot information and security systems vdot
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2004 VA SEMD 102-04 [2004-10-14] 2004 | 4.7 Satisfied (12594 Votes) |



Processing stages for VDOT access statements
Move from scope review to delivery, signature, and controlled archival without separating the statement from its completion evidence.
Prepare the statement
Deliver to signers
Track signer turnaround
Complete and archive
Virginia rules and document limits
Missing authorization
No audit trail
Overbroad permissions
Required notarization
Privacy and disclosure pitfalls
Including vendor employee details or system credentials beyond the approved VDOT access scope can expose sensitive information in the executed statement. Sending the statement to an unverified address can prevent VDOT from reliably attributing the authorization to the intended vendor representative. Granting access before the signed statement and review record are complete can create an authorization gap during a security investigation. Sharing the completed PDF without its audit trail can make it harder to establish delivery, signer identity, and the timing of consent.
Troubleshooting VDOT statement workflows
Resolve field, signer, plan, and evidence issues by checking the document scope and signNow record before granting VDOT system access.
Upload the original PDF or source document in signNow, then inspect automatically detected fields before sending. Add missing signature, date, initials, or acknowledgment fields manually so the VDOT statement captures every required approval.
Use an authorized vendor representative’s email address and confirm the recipient before sending. signNow’s Business plan includes templates and audit trails; the completed record should identify the actual signer rather than a shared mailbox.
signNow supports ESIGN and UETA compliance, but legal effect still depends on intent, consent, attribution, and record retention under 15 U.S.C. §§ 7001 and 7006. Preserve the signed statement and its completion evidence.
Business Premium includes bulk send and kiosk mode, while Business provides legally binding eSignatures, audit trails, templates, and mobile apps. For one VDOT vendor statement, upload and send a single document instead of using bulk workflows.
If a signer cannot open the request, verify the email address, resend the invitation, or provide a controlled signing link. Do not forward an untracked copy when the VDOT workflow requires documented signer attribution.
After every signer completes the VDOT statement, download the signed PDF and completion certificate or audit evidence from signNow. Store them together with the access decision, limiting access to authorized contract and security personnel.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.