Notice Of Privacy Practices
Get the Notice Of Privacy Practices Template 2003 template, fill it out, eSign it, and share it in minutes.
What a Notice Of Privacy Practices does
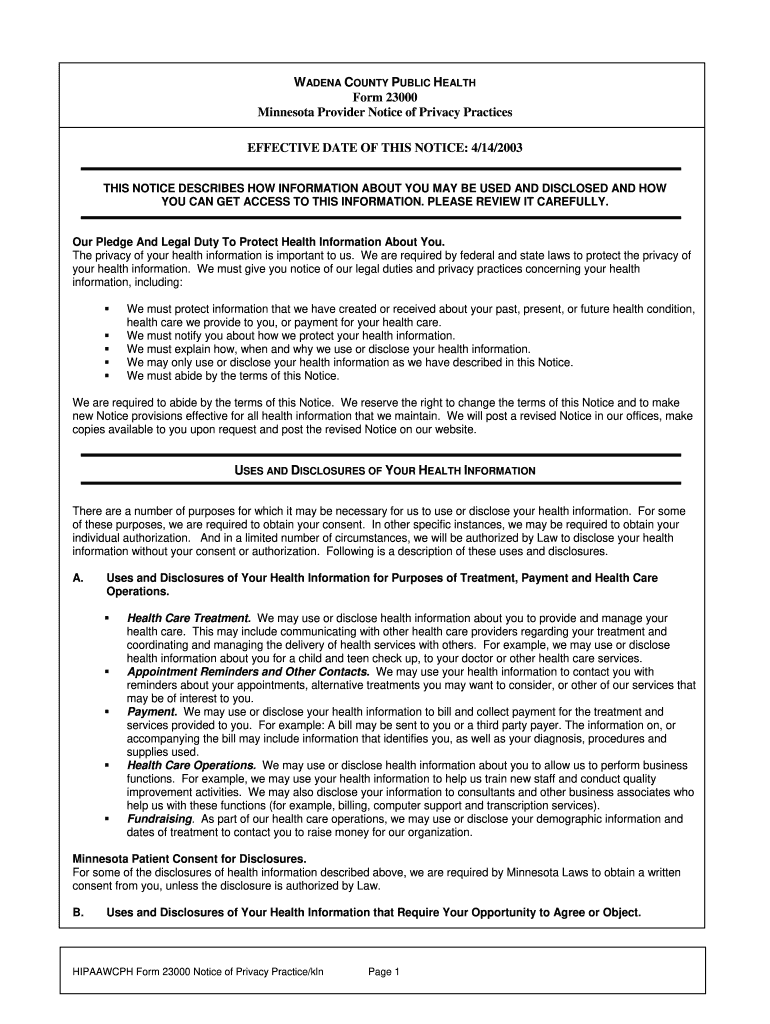
A Notice Of Privacy Practices tells a patient how a HIPAA covered entity may use and disclose protected health information and explains the patient’s privacy rights. The healthcare organization prepares the notice, gives it to the individual, and documents the organization’s good-faith effort to obtain written acknowledgment when required. The notice is not a general consent form or treatment authorization. Its content should reflect the organization’s actual privacy practices, uses, disclosures, contact information, and effective date under the HIPAA Privacy Rule, including 45 CFR 164.520.
Who uses this privacy notice
Healthcare providers
Healthcare providers use the Notice Of Privacy Practices for patient-facing privacy disclosures, acknowledgment records, and documented refusal workflows. The notice should reflect the provider’s actual uses and disclosures of protected health information under HIPAA.
HIPAA covered entities
Health plans and healthcare clearinghouses use the notice to explain privacy rights, permitted disclosures, complaint contacts, and how individuals can request access or amendments to protected health information.
Business types that use privacy notices
The right workflow depends on the organization’s size, patient volume, privacy office structure, and need to document each Notice Of Privacy Practices response.
Solo medical practices can use a controlled privacy-notice template to collect patient acknowledgments, record refusals, and retain delivery evidence without maintaining paper routing between staff members. Hospital and clinic groups can assign privacy-office ownership, delegate sending to approved teams, and preserve each patient response against the effective version used at that location. Healthcare enterprises can connect signNow with systems such as NetSuite, Microsoft 365, or cloud storage while applying role-based access, audit trails, and a six-year HIPAA retention baseline.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How a patient acknowledgment workflow works
A Notice Of Privacy Practices workflow connects the organization’s approved notice to a documented patient acknowledgment or refusal.
Upload notice: The healthcare organization uploads the current privacy notice and checks its effective date. Detect fields: signNow identifies fillable acknowledgment, refusal, date, and signature fields. Send notice: The organization sends the notice to the patient through the selected workflow. Capture acknowledgment: The patient reviews the disclosure and signs or records a refusal.
How the Notice Of Privacy Practices audit trail works
A signNow audit trail records identity, timing, document integrity, and retrieval events around each completed Notice Of Privacy Practices.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Notice Of Privacy Practices setup
Configure the workflow around patient acknowledgment, protected health information, controlled access, and HIPAA record retention requirements.
| Configuration | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP for sensitive workflows |
| Signature type | Typed or drawn acknowledgment signature |
| Audit trail | Capture timestamps, IP address, and completion history |
| Retention and encryption | Retain six years under 45 CFR 164.530(j); use AES-256 and TLS |
| User provisioning | Assign role-based access to privacy and compliance staff |
Security controls for protected health information
Data encryption:
Transport security:
HIPAA coverage:
Control assurance:
Security management:
Electronic signatures:
Platform requirements for privacy workflows
Staff can prepare and manage the Notice Of Privacy Practices in supported browsers on Windows or macOS, while patients can review and acknowledge it using supported desktop browsers or signNow mobile apps on iOS and Android. Use current browser versions with TLS-enabled connections and organization-approved devices for protected health information.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Mobile apps signNow mobile apps
Healthcare organizations should also confirm managed-device controls, role-based access, and any required API or single sign-on configuration before production use. A HIPAA workflow requires a business associate agreement where applicable, documented access governance, and retention procedures aligned with 45 CFR 164.530(j).
Find and fill out the correct notice of privacy practices form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2003 MN HIPAAWCPH 23000 [2003-04-14] 2003 | 4.8 Satisfied (4620 Votes) |



Privacy and disclosure pitfalls to avoid
Patient acknowledgment may be missing even when the Notice Of Privacy Practices was delivered electronically. A notice can expose unnecessary protected health information when staff attach patient-specific details to the workflow. Outdated effective dates or contact details can make the notice inconsistent with the organization’s current privacy practices. Shared administrator access can prevent reliable attribution of who sent, changed, or retrieved the notice.
Record-keeping practices for privacy notices
Use a documented retention, export, and access-control process for each Notice Of Privacy Practices acknowledgment and related audit record.
Apply the HIPAA six-year retention rule
Export the full audit trail
Archive records securely
Preserve version history
Healthcare examples for privacy notices
Healthcare organizations can connect patient-facing privacy disclosures with controlled signing, acknowledgment capture, and auditable record management.
Fertility healthcare
Fertility Centers of Illinois uses signNow for healthcare documents that require patient-facing workflows and controlled electronic records.
- Healthcare patient documents
The organization’s founder, John Butler, described signNow’s API and responsiveness positively. For a Notice Of Privacy Practices workflow, the relevant application is operational: connect the approved notice to patient delivery, capture acknowledgment activity, and preserve the resulting record under the organization’s HIPAA retention and access policies.
Healthcare operations
A healthcare practice can use the same signNow workflow for privacy notices across clinic locations while keeping the effective version controlled.
- Multi-location clinics
An anonymized clinic workflow can separate template ownership from sending permissions, reducing the risk that staff distribute an outdated notice. Each completed acknowledgment can remain associated with the notice version, patient response, timestamps, and audit trail required for internal review. No patient-specific outcome is assumed.
Notice Of Privacy Practices processing timeline
The workflow moves from content review through delivery, patient acknowledgment, and controlled archival without importing unrelated filing deadlines.
Prepare the notice
Deliver to patient
Record patient response
Archive completed record
Risks when privacy notices are mishandled
Patient receives obsolete version
Delivery evidence becomes incomplete
Unnecessary PHI enters workflow
Unauthorized staff view records
Notice Of Privacy Practices troubleshooting
Resolve the specific field, HIPAA, signature, plan, audit-trail, and retention questions that arise when managing this privacy notice.
signNow can use templates and fillable fields for the organization’s approved notice. Check that the effective date, privacy contact, acknowledgment field, refusal option, and patient-facing disclosures match the current version before sending.
A HIPAA workflow requires appropriate safeguards and a business associate agreement where applicable. signNow identifies HIPAA compliance as requiring a BAA; confirm the account configuration and organizational responsibilities before processing protected health information.
Electronic signatures may satisfy ESIGN and applicable state law when intent, consent, attribution, and record retention are established. HIPAA still governs the notice’s content, delivery, and documentation requirements under 45 CFR 164.520.
The Business plan is listed at $8 per user per month with annual billing and includes audit trails and templates. Subscription plans include 100 signature invites per user per year; review plan limits before scaling patient workflows.
Use signNow’s audit trail to review timestamps, delivery events, authentication information, and signer activity. Export the completed record and audit history together so the organization can reproduce the acknowledgment evidence during a compliance review.
HIPAA requires the notice and related documentation to be retained for six years from creation or the last effective date under 45 CFR 164.530(j). State law or organizational policy may require a longer period.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.