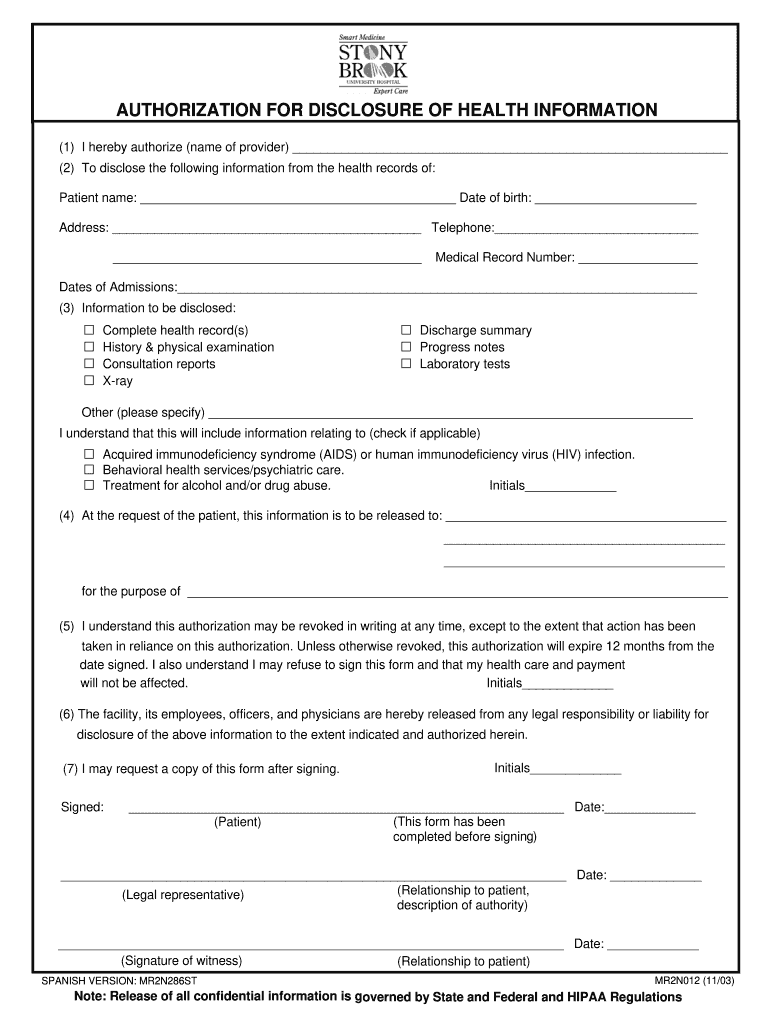
Authorization For Disclosure Of Health Information Stony Brook Medicalcenter Stonybrook
Create a custom Authorization For Disclosure Of Health Information Stony Brook Medicalcenter Stonybrook 2003 that meets your industry’s specifications.
What this Stony Brook authorization does
The Authorization For Disclosure Of Health Information Stony Brook Medicalcenter Stonybrook is a patient consent document that permits Stony Brook Medical Center to disclose specified health information to a named recipient for a stated purpose. The signer identifies the patient, recipient, records or information covered, purpose, expiration, and signature details. In signNow, upload the form, review detected fields, add or correct fields, send it to the authorized signer, and retain the completed PDF with its audit trail. HIPAA documentation generally requires six-year retention under 45 CFR 164.530(j).
Who uses the Stony Brook authorization
Patients
Patients authorize Stony Brook Medical Center to disclose specified health information to a named recipient for a defined purpose.
Records staff
Release-of-information staff prepare, route, verify, and archive the signed authorization before disclosure.
Who benefits from this authorization workflow
The form serves patients, authorized representatives, and healthcare records teams coordinating a defined disclosure from Stony Brook Medical Center.
Stony Brook Medical Center release-of-information staff can use a reusable authorization template to collect patient consent, route it to the signer, and preserve the completed record with its audit trail. Healthcare providers and authorized representatives can review the named recipient, purpose, and information scope before signing, reducing ambiguity when records must be shared with another provider, insurer, or legal representative. Enterprise health-information teams can administer templates, permissions, and signing workflows centrally while applying HIPAA controls and retaining authorization evidence for the required six-year documentation period.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features that fit this disclosure form
signNow connects the form’s patient-consent fields with controlled signing, audit evidence, and HIPAA-focused document handling.
Field review
Upload the Stony Brook PDF and review signNow’s detected fields before adding missing patient, recipient, purpose, expiration, or signature fields.
Signer routing
Route the authorization to the designated signer by email or controlled signing link, keeping the intended recipient and signer distinct.
Audit evidence
Capture the signer’s intent, timestamp, and document history in an audit trail associated with the completed authorization.
HIPAA workflow
Use HIPAA-compliant signNow workflows with a BAA to protect private health information during electronic processing.
Reusable templates
Apply templates and administrator permissions so records staff handle the same Stony Brook authorization consistently across disclosure requests.
Mobile completion
Complete the authorization on desktop or mobile, then preserve the signed PDF and audit trail in an approved records repository.
Complete the Stony Brook authorization in four steps
Use signNow to prepare the named authorization, capture the required consent, and preserve completion evidence for the disclosure file.
Upload form:
Upload the Stony Brook authorization PDF. Check fields:
Review detected fields and add missing patient, recipient, purpose, and signature fields. Send securely:
Enter the authorized signer’s email or create a controlled signing link. Archive evidence:
Verify the completed document and download its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for this health authorization
Configure the Stony Brook Medical Center authorization around identifiable health information, signer attribution, and HIPAA recordkeeping requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export the completed audit trail |
| Document retention | 6 years under 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
How signNow records the authorization audit trail
The audit trail documents the signing event separately from the form’s clinical and disclosure fields, giving Stony Brook staff evidence of actions and timing.
Authenticate signer:
Capture timestamp:
Seal document history:
Export evidence:
Archive securely:
Retrieve history:
Find and fill out the correct authorization for disclosure of health information stony brook medicalcenter stonybrook
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Stony Brook MR2N012 2023 | 4.8 Satisfied (585 Votes) | |
| Stony Brook MR2N012 2013 | 4.8 Satisfied (7171 Votes) | |
| Stony Brook MR2N012 2003 | 4.7 Satisfied (489 Votes) |



Security controls for protected health information
HIPAA protection:
Data in transit:
Stored data:
Security assurance:
Information security:
Electronic signatures:
Privacy pitfalls in health-information disclosure
Entering the wrong patient or recipient can authorize disclosure to an unintended party, even when the electronic signature and delivery record are complete. A vague description of records or purpose can make the Stony Brook authorization difficult to apply consistently and increase disclosure-review questions. Sending protected health information before confirming signer identity, consent, and access permissions can expose records beyond the authorized recipient. Failing to preserve the signed authorization and audit trail leaves Stony Brook Medical Center without clear evidence of consent, scope, timing, or signer attribution.
Recordkeeping practices for health authorizations
Preserve the signed Stony Brook Medical Center authorization with evidence showing who signed, what was authorized, and when the record was completed.
Retain the authorization and audit trail
Export completion evidence promptly
Archive records with restricted access
Validate scope before disclosure
Retention schedule for related records
Apply the rule that matches the record class actually stored with this authorization; HIPAA documentation is the directly relevant baseline for health-information disclosures.
Six years for HIPAA records
Three years for tax records
I-9-specific retention rule
Five years for OSHA injuries
Thirty years for exposure records
Risks from incomplete authorization records
Unauthorized release
Overbroad authorization
Attribution dispute
Record challenge
Troubleshooting this health-information authorization
Resolve field, identity, HIPAA, plan, and electronic-signature questions before releasing records under the Stony Brook Medical Center authorization.
Upload the original Stony Brook Medical Center PDF again, then inspect each detected field. signNow templates and field placement can be adjusted before sending, so verify patient, recipient, purpose, and signature locations manually.
A signer can use the email invitation or a signNow signing link without creating an account when the sender permits it. If identity assurance is insufficient, add SMS OTP or another available authentication control before sending.
For protected health information, signNow states HIPAA compliance requires a business associate agreement. Confirm the BAA and organizational configuration before using the platform for this Stony Brook authorization.
The Business plan includes legally binding eSignatures and audit trails. Business Premium adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication for higher-control workflows.
A completed signature does not correct an inaccurate scope. Reopen the authorization, verify the patient, recipient, records, purpose, expiration, and consent language, then send a corrected version and retain the superseded record according to policy.
Electronic signatures generally receive legal recognition under ESIGN and applicable UETA rules when intent, consent, attribution, and record retention are demonstrated. Consumer-facing records also require the ESIGN disclosure and access requirements in 15 U.S.C. §7001(c).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.