Ucla Release Of Records Forms
Create a custom Ucla Release Of Records Forms 2011 that meets your industry’s specifications.
What UCLA release forms do
UCLA Release Of Records Forms are authorization documents used to approve disclosure of specified records to a named recipient. A signer identifies the permitted disclosure, reviews the information, and signs the authorization. With signNow, upload the UCLA form, auto-detect fillable fields, add signature and consent fields, send it to the authorized person, and retain the completed document with its audit trail. The form’s exact disclosure scope and processing rules should follow the UCLA version being used and applicable HIPAA requirements.
Who uses UCLA release forms
Patients and representatives
Patients and authorized representatives can complete the UCLA release, identify the records covered, name the recipient, and provide consent before the health-information department processes disclosure.
Healthcare organizations
UCLA clinics, health-information departments, researchers, insurers, and attorneys can use the completed release to support a defined records-disclosure request with documented authorization.
Business types using UCLA release forms
UCLA release-of-records forms are most useful where authorized disclosure, recipient identity, and patient consent must remain clearly documented.
✓ UCLA-affiliated private practices use these release-of-records forms to document a patient’s authorization before sharing specified medical records with another provider, insurer, attorney, or designated recipient. ✓ University research teams use UCLA records-release forms to capture a participant’s permission, define the approved recipient and record scope, and preserve signed evidence for study administration or care coordination. ✓ Enterprise health systems use standardized UCLA release workflows across clinics, compliance teams, and health-information departments, reducing manual routing while maintaining controlled access to sensitive patient records.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for UCLA record authorizations
The most useful signNow features for UCLA releases connect form preparation, signer consent, controlled delivery, evidence capture, and health-information recordkeeping.
Field detection
Upload the UCLA form and detect existing fields before adding signature, date, and electronic-consent fields, reducing manual preparation for a patient or authorized representative.
Controlled routing
Route the release directly to the intended signer by email or signing link, keeping the authorization request separate from unrelated documents and recipients.
Audit trail
Capture signer actions, timestamps, and completion details in an audit trail that can accompany the UCLA release during internal review.
HIPAA workflow
Use signNow’s HIPAA compliance with a required BAA when the workflow handles protected health information and the organization’s compliance program requires that arrangement.
Secure storage
Keep the signed UCLA authorization and completion record available for authorized health-information staff without relying on paper routing or manual scanning.
Reusable template
Use templates for recurring UCLA release requests while preserving the approved disclosure language and recipient-specific fields required by the institution.
How UCLA release forms work online
signNow turns the UCLA release form into a controlled sequence from upload through consent, signature, completion, and record storage.
Upload form: Upload the UCLA release form and inspect its pages. Map fields: Auto-detect fields, then add consent and signature fields. Send request: Send the release to the authorized signer securely. Archive record: Store the completed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete a UCLA release
Use this sequence to prepare, sign, and preserve the UCLA authorization without changing its approved disclosure language.
Upload form:
Upload the exact UCLA release version. Review details:
Confirm recipient, scope, and required fields. Send request:
Send the authorization to the signer. Save evidence:
Store the signed release and audit trail.
Recommended UCLA records-release setup
Configure the UCLA release workflow around verified signer identity, documented consent, controlled access, and an exportable record of every signing event.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Retain six years when HIPAA applies |
| Encryption | TLS 1.2 or 1.3 in transit |
What the UCLA audit trail records
The audit trail documents technical evidence around the UCLA release, helping reviewers connect signer identity, document integrity, and each recorded action.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident seal:
Event history:
Audit export:
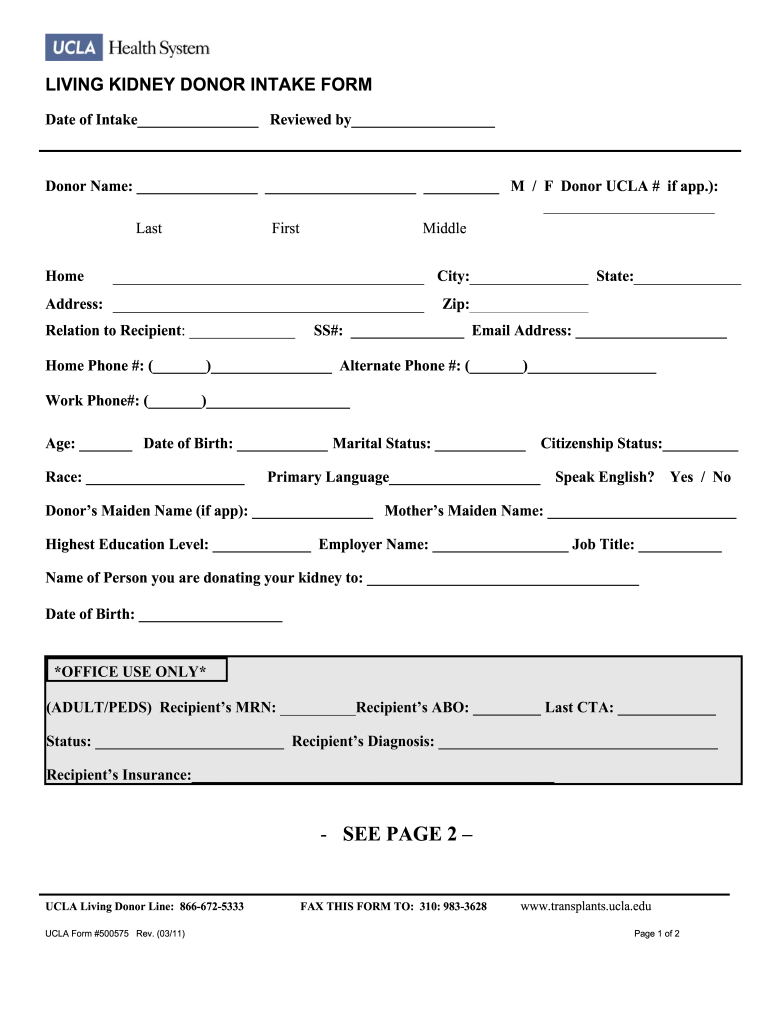
Find and fill out the correct donor intake form ucla
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| 2011 UCLA Form 500575 [2011-03] 2011 | 4.8 Satisfied (2833 Votes) |
Security for UCLA records disclosures
Encrypted data:
Health information:
Control assurance:
Security management:
Privacy controls:
Signature framework:
Privacy pitfalls in UCLA releases
Including an entire medical chart when the UCLA release authorizes only specified dates, providers, or record categories can exceed the signer’s stated consent. Sending a completed UCLA release to an unintended recipient can expose protected health information and create an unauthorized-disclosure investigation. Failing to preserve the signer’s electronic consent disclosure may weaken evidence that the person agreed to transact and receive records electronically. Allowing broad team access to completed UCLA releases can expose patient identifiers beyond the staff members assigned to process the request.
Legal standing of UCLA release forms
A signed UCLA release can provide evidence of consent when the signer intends to approve the electronic record, consents to electronic records, and the record remains reproducible. ESIGN and applicable state law support electronic signatures, but wills, court orders, and certain family-law documents remain excluded.

Best practices for UCLA record releases
Accurate scope, controlled access, and preserved evidence help a UCLA release remain usable throughout the disclosure process.
Keep the release and audit trail together
Match disclosure scope to consent
Export and restrict completed records
Check UCLA and state retention rules
Retention periods for UCLA release records
Retention depends on the records connected to the UCLA release and the organization’s applicable legal obligations; HIPAA documentation is the most direct healthcare reference.
Six years: HIPAA documentation
Three years: federal tax records
Six years: tax understatement
Three years: FLSA payroll
Five years: OSHA injuries
Examples of UCLA release workflows
Healthcare organizations can adapt the signing sequence to patient authorizations while preserving a clear record of consent and completion.
Fertility healthcare
Fertility Centers of Illinois uses signNow in a healthcare setting where patient-facing documents require secure electronic handling and dependable API-supported workflows.
- Collect patient approvals electronically
- Maintain auditable completion records
Fertility Centers of Illinois selected airSlate SignNow for its API and responsive support. The customer story illustrates how a healthcare organization can connect electronic document workflows with patient-facing operations while keeping security and compliance considerations central to records-related signing.
Outpatient records
A UCLA-affiliated outpatient clinic can route a records-release request to a patient or authorized representative without requiring an in-person appointment.
- Limit disclosure to named recipients
- Retain the completed release
The clinic can use signNow to upload the UCLA form, identify its fields, send it to the intended signer, and retain the signed document with an audit trail. The clinic must still verify authorization, disclosure scope, and any UCLA-specific processing requirements.
Troubleshooting UCLA release forms
Resolve field, signer-access, compliance, plan, and retention questions before the UCLA authorization is used to disclose records.
Upload the approved UCLA release as a PDF, then inspect every detected field. signNow’s field detection does not replace a manual check of disclosure scope, recipient details, or institution-required language before sending.
Use signNow’s email verification or SMS OTP when the signer’s identity needs stronger evidence than an email link. The organization should select authentication appropriate to its UCLA policy and disclosure risk.
A UCLA release involving protected health information requires organizational compliance controls, including a business associate agreement where applicable. signNow identifies HIPAA compliance, but the healthcare organization remains responsible for its authorization process.
If a signer cannot access the document, confirm the email address, resend the invitation, or provide a controlled signing link. Do not send patient records or completed releases through an unapproved alternate channel.
The Business plan includes audit trails and templates at $8/user/month when billed annually. Business Premium adds bulk send at $15/user/month; choose based on the UCLA team’s actual volume and routing needs.
A completed UCLA release should retain the final document and its audit trail together. HIPAA documentation generally requires six years under 45 CFR §164.530(j), but UCLA policy, state law, or a hold may require longer.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.