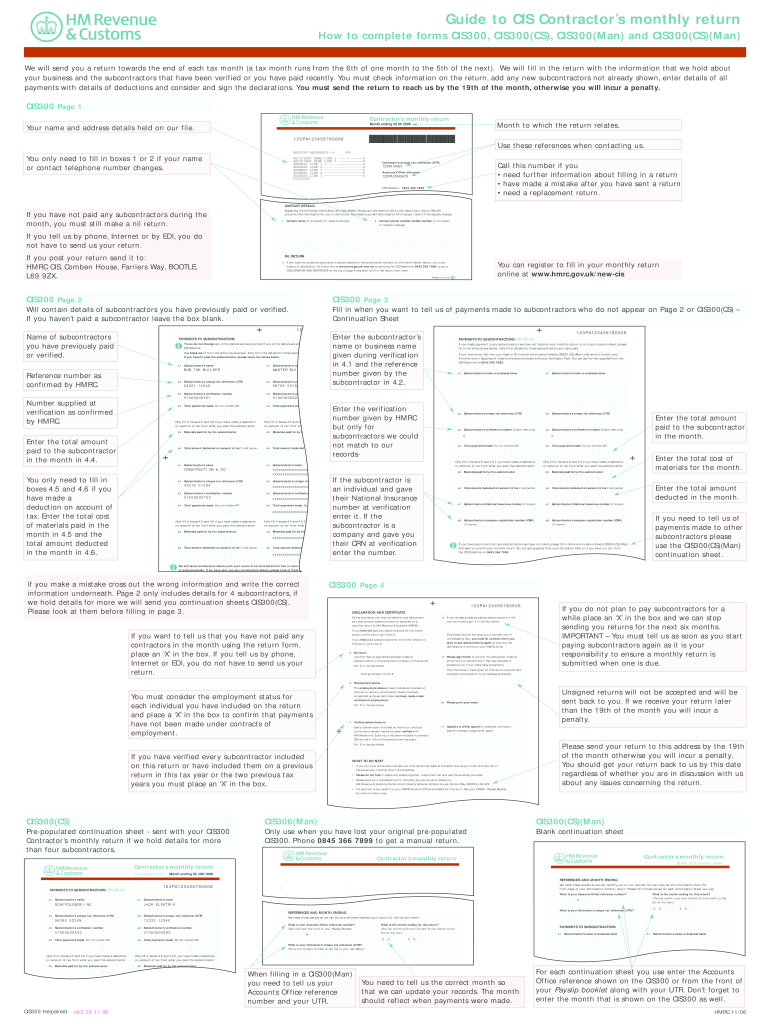
CIS300
Simplify the creation of a Cis300 2006 via a ready-made template.
What CIS300 is and how it works
CIS300 is a U.S. form that can be completed and routed electronically when its recipient, issuing authority, and transaction rules permit electronic records. In signNow, upload the CIS300 file, let the platform detect fillable areas, review and place signer fields, then send it by email or signing link. Each signer reviews the populated form, provides the required electronic signature, and receives the completed record. signNow preserves timestamps, signer actions, document history, and an audit trail for later review.
Who can use CIS300 workflows
Business teams
Use CIS300 for agreements, NDAs, HR forms, invoices, or consent forms when its fields match the transaction and the recipient can review and sign electronically.
Regulated workflows
Legal, financial, healthcare, and operations teams can route CIS300 to designated signers, preserve the audit trail, and apply access controls to completed records.
How to complete CIS300 in signNow
Use this sequence to turn the CIS300 source file into a controlled electronic signing record.
Upload: Upload the CIS300 file Prepare: Review detected fields Route: Assign each signer Finish: Complete and archive
Privacy challenges when handling CIS300
CIS300 may expose taxpayer or business information when completed copies are emailed without access controls. Missing electronic-consent language can weaken evidence that a CIS300 signer agreed to transact electronically. Unrestricted template access can let unauthorized users alter CIS300 fields before signature collection. Sending a completed CIS300 to the wrong recipient can disclose sensitive identifying information.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the CIS300 audit trail works
signNow records the evidence surrounding CIS300 completion so reviewers can connect the signed document with signer actions and document history.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Action history:
Audit export:
Security controls for CIS300 documents
Data encryption:
Security certification:
Security management:
Privacy compliance:
Healthcare compliance:
Transport security:
Find and fill out the correct cis300 adittional sheets form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2006 UK CIS300 Helpsheet [2006-11] 2006 | 4.8 Satisfied (6802 Votes) |
Legal standing of CIS300 signatures
A completed CIS300 may be admissible when the signer shows intent, consents to electronic records, can be identified, and the record remains reproducible under ESIGN, 15 U.S.C. chapter 96, and applicable UETA rules. Wills, codicils, testamentary trusts, court orders, and certain family-law documents remain statutory exceptions.

Best practices for preparing CIS300
Accurate field review, documented consent, controlled access, and secure archival reduce avoidable errors when CIS300 moves through an electronic signing workflow.
Confirm the current CIS300 version
Review every detected field
Capture electronic consent clearly
Archive the signed record securely
Platform requirements for completing CIS300
CIS300 can be prepared in signNow through Chrome, Firefox, Safari, or Edge on Windows and macOS. Mobile access is available through iOS and Android apps, with TLS 1.2/1.3 protecting transmitted information.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile systems iOS and Android mobile access
Organizations should use managed Windows, macOS, iOS, or Android devices when CIS300 contains sensitive information. Confirm browser updates, mobile-app permissions, API access, SSO provisioning, and any certificate or long-term-validation configuration required by internal policy before deployment.



CIS300 signing and compliance questions
These answers address field detection, electronic consent, audit evidence, security configuration, and statutory limits affecting CIS300 workflows in signNow.
Upload CIS300 to signNow, allow field detection to identify fillable areas, then manually review every detected field. If the document is image-only or fields are misplaced, replace the source file or correct the fields before sending.
Business includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, SOC 2, and GDPR support. Business Premium adds bulk send, while Enterprise adds advanced signer authentication and conditional fields.
signNow states that HIPAA compliance requires a business associate agreement. If CIS300 contains protected health information, confirm the BAA and configure access, authentication, and retention controls before sending the document.
For a consumer-facing electronic CIS300 transaction, provide the ESIGN consumer disclosure, explain the right to paper records, confirm electronic access, and provide a method to withdraw consent under 15 U.S.C. §7001(c).
A signNow audit trail records timestamps, signer actions, and document history. Export the completed CIS300 with its audit evidence, then retain both under the applicable transaction, tax, or organizational rule.
Electronic signatures do not override ESIGN exceptions. Wills, codicils, testamentary trusts, court orders, and specified family-law documents require separate legal review and may require paper or in-person procedures.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.