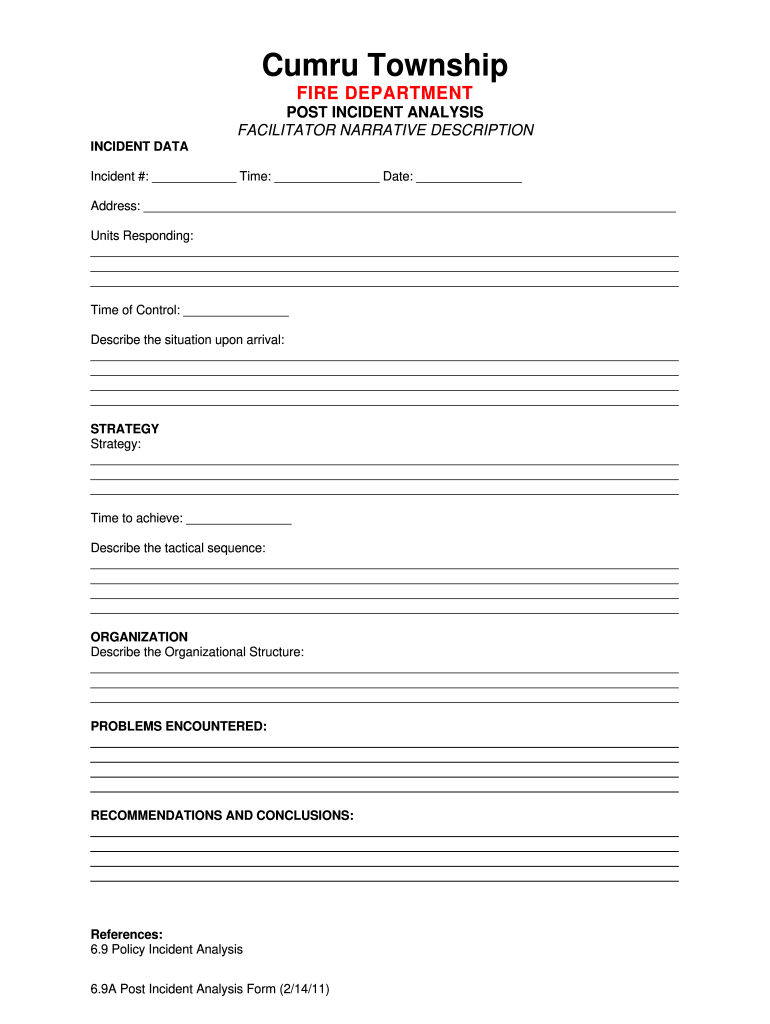
Post Incident Analysis (2011 2026)
Use a Post Incident Analysis Template 2011 template to make your document workflow more streamlined.
What Post Incident Analysis means
Post Incident Analysis (2011 2026) is a structured record for examining what happened after an incident, why it happened, and what corrective actions follow. It typically captures the incident description, timeline, findings, contributing factors, assigned owners, approvals, and follow-up evidence. With signNow, a sender uploads the document, reviews detected fillable fields, assigns reviewers, sends it for signature, and stores the completed record with an audit trail. ESIGN and UETA can support electronic execution when intent, consent, attribution, and record retention requirements are satisfied.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Complete the post-incident analysis
Use signNow to prepare, route, sign, and preserve Post Incident Analysis (2011 2026) with a documented signing sequence.
Upload document:
Upload the completed Post Incident Analysis document. Review fields:
Let signNow detect fields and review placement. Send for signature:
Assign signers and send the analysis securely. Archive record:
Complete signatures and store the audit trail.
Recommended workflow setup
Configure Post Incident Analysis (2011 2026) around signer identity, document integrity, review evidence, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Detailed action log and completion certificate |
| Document retention | Apply documented organizational retention policy |
| Encryption | TLS 1.2 or 1.3 and AES-256 encryption |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The signNow audit trail documents the technical events that connect each signature to Post Incident Analysis (2011 2026).
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Build certificate:
Retrieve audit trail:
Find and fill out the correct post incident analysis form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2011 PA Post Incident Analysis - Cumru Township [2011-02-14] 2011 | 4.8 Satisfied (1817 Votes) |
Signer authentication and certificates
PKI certificates:
X.509 authentication:
Two-factor authentication:
SMS OTP:
ID verification:
Audit evidence:
Record-keeping practices for incident analyses
Preserve the completed analysis, signing evidence, access history, and retention decision as one controlled record.
Set the retention period before signing
Export the audit trail with the record
Restrict access to sensitive findings
Validate fields before distribution
State rules and document limits
State notarization
Wills excluded
Family law
Real-estate deeds



Troubleshoot Post Incident Analysis workflows
Resolve field, signer, plan, legal, retention, and privacy questions before distributing Post Incident Analysis (2011 2026).
Upload the source PDF again, then confirm that each detected field matches the Post Incident Analysis (2011 2026) page and intended signer. signNow templates can preserve corrected field placement for later analyses.
Use signNow SMS OTP or another configured authentication method when the analysis contains sensitive incident details. Authentication strengthens attribution, while the audit trail records the signer’s actions and timestamps.
Business includes legally binding eSignatures, audit trails, templates, and mobile apps. Business Premium adds bulk send and kiosk mode; choose based on the number and routing pattern of analyses.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. Consumer-facing workflows also require the ESIGN disclosure and access requirements under 15 U.S.C. §7001(c).
Export the completed document and audit trail from signNow, then store both under the organization’s incident-record policy. Do not assume a platform setting replaces regulatory or contractual retention duties.
If the analysis includes protected health information, use a signNow HIPAA workflow with a BAA. HIPAA records generally require six years from creation or the last effective date under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.