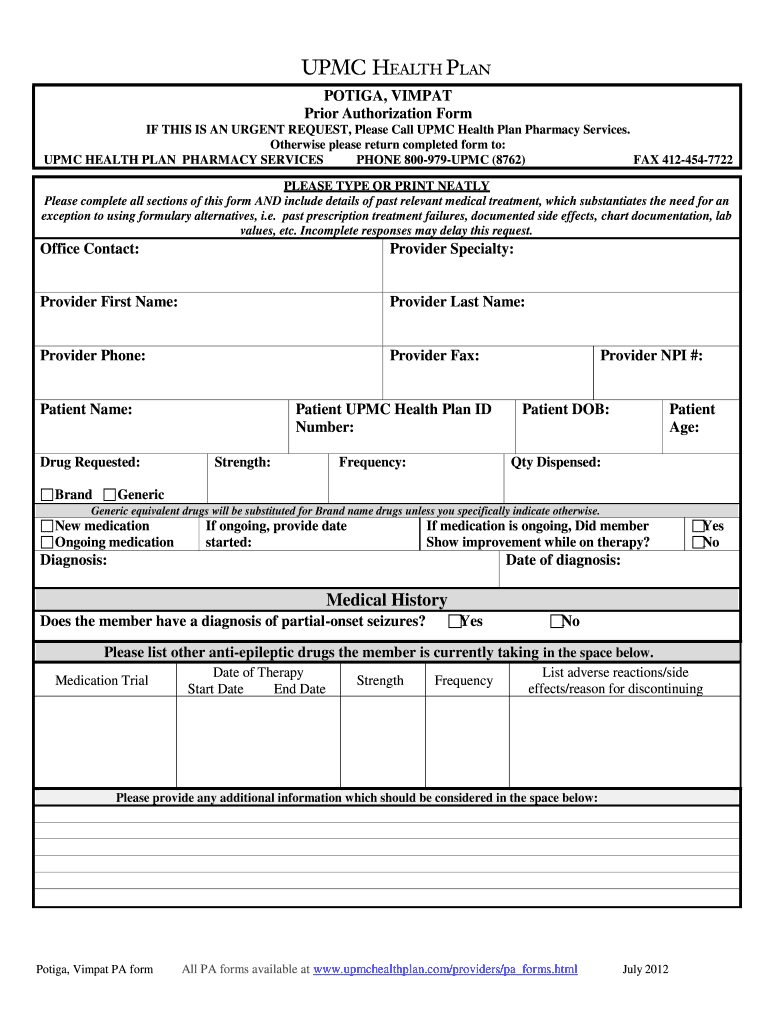
Upmc Prior Auth Form (2012 2026)
Create a custom Upmc Prior Auth Form 2012 that meets your industry’s specifications.
What the Upmc prior authorization form does
The Upmc Prior Auth Form (2012 2026) is a healthcare authorization document used to request approval for a covered service, medication, or treatment before care proceeds. A provider records patient identifiers, diagnosis or clinical justification, requested services, and supporting information for review by the payer. The completed form is routed to the appropriate healthcare organization for a determination. With signNow, a sender can upload the form, detect fillable fields, assign signer roles, collect signatures, and preserve the completed record with an audit trail. Submission requirements remain determined by Upmc and the applicable plan.
Who uses the Upmc authorization form
Healthcare providers
Clinicians and utilization-review staff use the form for treatment approvals, medication requests, clinical attachments, and provider signatures.
Authorization participants
Patients, specialty pharmacies, and payer reviewers receive assigned fields, sign where required, and access only the authorization information relevant to their role.
Organizations that use prior authorization workflows
The form is most useful where clinical documentation, patient consent, and payer review must move together in a traceable process.
Outpatient clinics use the form to request approval for planned treatments, attach clinical justification, and route provider signatures before scheduling care. Pharmacy and specialty-care teams prepare medication authorization requests, collect required approvals, and preserve completed records for patient and payer follow-up. Hospital revenue-cycle departments coordinate provider, utilization-review, and payer-facing tasks while centralizing authorization documents under role-based administrative controls.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete the Upmc authorization form online
Prepare the Upmc Prior Auth Form (2012 2026) in signNow by following the document-specific workflow from upload through secure record storage.
Upload form:
Upload the current Upmc form. Add fields:
Place patient and provider fields. Set roles:
Assign each required signer. Send request:
Send the authorization request. Store record:
Review the signed record and audit trail.
How the audit trail protects authorization records
The audit trail documents who handled the Upmc Prior Auth Form (2012 2026), what changed, and when the completed authorization record was preserved.
Authenticate signer:
Capture timestamp:
Hash document:
Seal document:
Log actions:
Retrieve evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features that support authorization processing
signNow connects the Upmc Prior Auth Form (2012 2026) to a controlled workflow for field completion, signatures, evidence, and protected record handling.
Field detection
Upload the Upmc form and use field detection to prepare patient, provider, service, and signature fields without recreating the document manually.
Signer roles
Assign provider, patient, and reviewer roles so each participant receives only the fields and actions required for authorization completion.
Remote signing
Collect required signatures remotely while preserving the submitted clinical information in one completed authorization record.
Audit trail
Capture timestamps, signer actions, and delivery events to support review of how the authorization form was completed.
Reusable templates
Use templates for repeated authorization requests while retaining the specific patient and treatment information for each submission.
HIPAA workflows
Keep patient information protected with access controls and HIPAA-compliant signNow workflows when a business associate agreement is required.



Platform requirements for prior authorization
Complete and e-sign the Upmc Prior Auth Form (2012 2026) through supported desktop or mobile browsers using a secure TLS connection.
Desktop browsers Chrome, Firefox, Safari, and Edge on Windows or macOS Mobile browsers Safari on iOS and Chrome on Android Secure connection TLS 1.2 or later for secure access
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices when handling patient information. Configure access controls, SSO, and audit-trail retention according to organizational policy and HIPAA obligations. Test browser permissions before sending the form, and confirm that recipients can open and sign the document without exposing protected health information.
Find and fill out the correct upmc auth form for drug
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2012 UPMC Health Plan Prior Authorization Form [2012-07] 2012 | 4.8 Satisfied (10094 Votes) |
Security controls for authorization documents
Healthcare privacy:
Business associate agreement:
Independent controls:
Information security:
Transit encryption:
Stored encryption:
Privacy and disclosure pitfalls to prevent
Patient names, member IDs, diagnoses, or medication details may appear in the wrong recipient’s copy or email notification. A provider may send the authorization request before obtaining the patient’s required electronic-record consent disclosure. Shared accounts or unrestricted templates can let an unauthorized employee view or modify patient information. Incomplete clinical justification or missing attachments can delay Upmc’s review even when every signature is present.
Best practices for Upmc authorization records
Use a controlled preparation, signing, submission, and retention process for every Upmc Prior Auth Form (2012 2026).
Verify the current form and payer instructions
Restrict protected health information access
Archive the completed record and audit trail
Check clinical content before submission
Recommended setup for authorization workflows
Configure the Upmc authorization workflow around patient privacy, signer identity, audit evidence, and the applicable HIPAA record-retention policy.
| Setting | Recommended configuration |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
Legal standing of electronic authorization records
Electronic signatures on a business authorization record can receive legal recognition under the federal ESIGN Act, 15 U.S.C. ch. 96, and applicable state law, including UETA or New York ESRA. Validity depends on intent, consent, attribution, and reliable record retention. Wills, court filings, and certain family-law documents remain excluded.

Prior authorization workflow examples
Healthcare teams can adapt signNow’s document workflow to authorization requests while keeping the form’s clinical and payer requirements intact.
Fertility care
Fertility Centers of Illinois uses signNow in a healthcare setting where patient-facing documents require responsive support and an API-enabled workflow.
- Patient signatures collected electronically
- Healthcare documents routed through API
The customer story identifies Fertility Centers of Illinois as a signNow customer and describes satisfaction with the API and support. That experience is relevant to authorization workflows requiring repeated patient-document routing, although it does not establish a specific Upmc form outcome or payer decision.
Outpatient clinic
A regional outpatient clinic prepares the Upmc form for provider review and sends the patient’s assigned consent fields separately.
- Clinical justification attached before sending
- Completed record retained for follow-up
This anonymized workflow illustrates how a clinic can separate clinical preparation from signature collection while preserving one authorization record. The clinic must still follow Upmc’s submission channel, verify required fields and attachments, and apply its HIPAA policies before releasing protected health information.
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting Upmc authorization workflows
Resolve document-preparation, signer-access, HIPAA, plan, and submission questions without confusing a completed signature with payer approval.
Upload the current form again and inspect its PDF permissions before placing fields. signNow’s field-detection workflow can identify fillable areas, but a scanned or restricted PDF may require manual placement. Confirm that patient identifiers and clinical sections remain readable after preparation.
Use signNow’s signer roles to assign provider, patient, and reviewer actions separately. If a signer cannot access the document, verify the email address, resend the invitation, or use a controlled signing link. Do not forward a link containing protected health information without access controls.
A signNow Business plan includes legally binding eSignatures and audit trails; Business Premium adds bulk send, while Enterprise adds advanced signer authentication. Select the plan based on workflow requirements, not on a claim that every plan includes identical controls.
signNow states that HIPAA use is compliant when a business associate agreement is required. The clinic remains responsible for minimum-necessary access, recipient verification, disclosures, retention, and Upmc’s submission rules; platform compliance does not replace those obligations.
Review the completed PDF and audit trail separately before submission. A signature proves the signing event, but it does not establish that diagnosis, requested treatment, provider credentials, attachments, or payer-specific fields are complete or accurate.
Electronic signatures can be recognized under ESIGN and applicable state law when intent, consent, attribution, and record reproduction are established. Healthcare organizations should also provide required consumer disclosures under 15 U.S.C. §7001(c) when the transaction is consumer-facing.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.