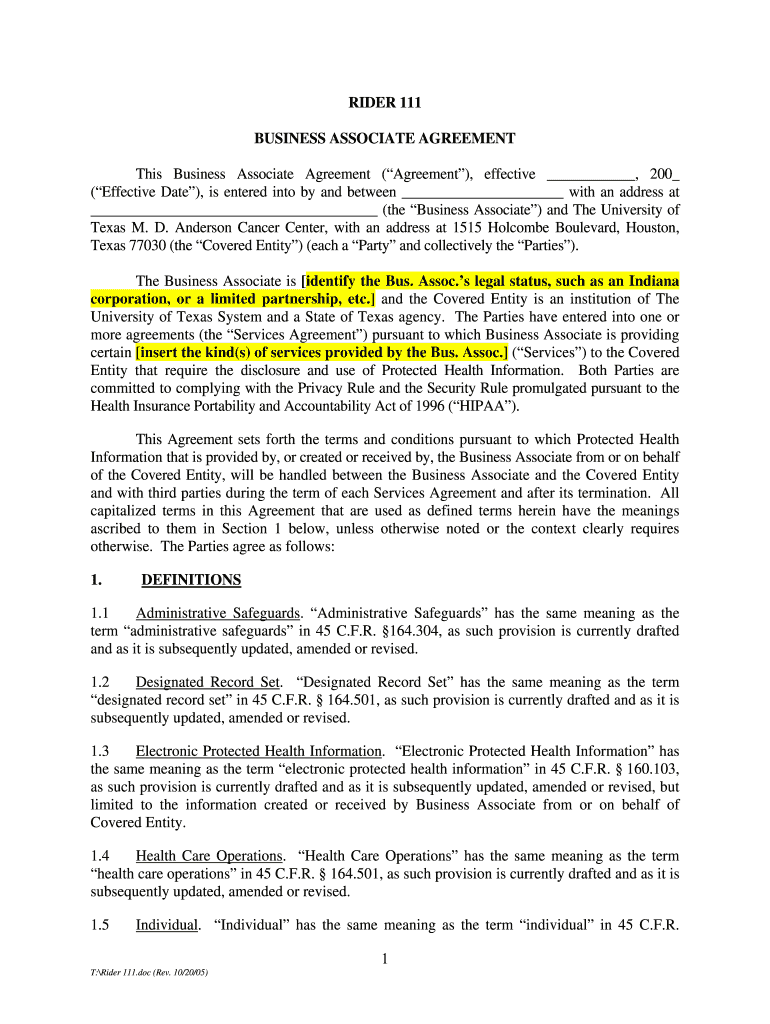
What Is A Business Associate Agreement
Get a What Is A Business Associate Agreement 2005 template with airSlate SignNow and complete it in a few simple clicks.
What a business associate agreement means
A business associate agreement is a written contract between a HIPAA-covered entity and a service provider that handles protected health information for the covered entity. It identifies permitted PHI uses and disclosures, requires appropriate safeguards, addresses breach reporting, extends relevant duties to subcontractors, and explains what happens to PHI when services end. The agreement does not replace HIPAA policies or security controls; it records each party’s responsibilities. Before a business associate receives PHI, the covered entity should establish the required contractual terms under 45 CFR 164.502(e) and 164.504(e).
Who uses a business associate agreement
Healthcare providers
Covered entities use business associate agreements when vendors create, receive, maintain, or transmit protected health information. The agreement defines permitted uses, safeguards, breach reporting, subcontractor duties, and return or destruction obligations for PHI handled during services.
Service providers
Business associates such as billing companies, cloud providers, and legal consultants use the agreement to document HIPAA responsibilities before accessing a covered entity’s PHI. It supports vendor review, role clarity, and evidence that required contractual safeguards were addressed.
Business types that use these agreements
A business associate agreement fits organizations that handle PHI through outsourced healthcare, technology, billing, or administrative services.
Solo medical practices use a business associate agreement before granting billing, transcription, or IT vendors access to PHI, documenting safeguards without building a separate procurement department. Regional health systems use agreements to standardize vendor onboarding, breach-notice duties, subcontractor controls, and return-or-destruction terms across multiple departments and facilities. Enterprise technology vendors use agreements to define HIPAA obligations for cloud, analytics, or support services, while coordinating security review, legal approval, and subcontractor oversight.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key features for agreement workflows
A business associate agreement workflow should make responsibilities clear, capture authorized signatures, and preserve evidence that the final contract was completed.
Field detection
Upload the agreement and let signNow identify fillable areas before you review, correct, and assign signature, date, and initials fields to authorized representatives.
Signing order
Send the contract in a defined signing order so the covered entity and business associate approve the same final terms without manual email coordination.
Audit trail
Capture signer identity, timestamps, IP information, and document actions in an audit trail that accompanies the completed agreement.
Record storage
Store the executed agreement and completion certificate together, supporting retrieval when a vendor review, audit, or dispute requires evidence of execution.
Reusable templates
Use templates for recurring vendor agreements while reviewing each vendor’s services, PHI access, subcontractors, and negotiated terms before sending.
Business integrations
Connect signed agreements with systems such as Salesforce, NetSuite, Google Drive, or Box to reduce duplicate entry and improve retrieval.
How to complete the agreement
Use this signNow sequence to prepare, execute, and retain a business associate agreement without changing its negotiated terms.
Upload:
Upload the agreement PDF. Check fields:
Review detected fields. Add signers:
Assign representatives. Send:
Send for signatures. Archive:
Store the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Ways to complete the agreement
- Open the signNow web app to upload the business associate agreement, review detected fields, and prepare the document when working from a desktop or browser.
- Use the signNow mobile app to review, complete, or sign the agreement from an iOS or Android device when participants work away from the office.
- Use kiosk mode when multiple authorized representatives sign at one controlled location, with the workflow configured for sequential or assigned signing.
- Generate a shareable signing link when approved recipients need access without individualized email invitations; restrict distribution and verify each signer’s identity.



Find and fill out the correct business associates agreement form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2005 The University of Texas MD Anderson Cancer Center Rider 111 [2005-10] 2005 | 4.8 Satisfied (6636 Votes) |
Recommended agreement setup
Configure the agreement workflow around signer identity, evidence preservation, HIPAA documentation, and controlled access to the completed contract.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enabled with completion certificate |
| Document retention | 6 years under 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 |
Security for PHI agreements
HIPAA compliance:
Independent assurance:
Security management:
Stored data:
Transport security:
Electronic signatures:
What the audit trail records
The audit trail provides execution evidence for the business associate agreement beyond the signature image itself.
Signer authentication:
Timestamp capture:
Document integrity:
Sealing:
Audit history:
Retrieval and export:
Retention periods for related records
Retention depends on the record class surrounding the agreement; apply the rule that governs the underlying healthcare, tax, employment, payroll, or audit record.
6 years for HIPAA records
3 years for tax records
Later of two I-9 dates
3 years for payroll records
7 years for SOX records
Agreement mistakes to avoid
Including PHI in a vendor agreement without confirming the vendor’s role, permitted uses, safeguards, and breach-notification responsibilities. Using an agreement that omits subcontractor obligations, leaving downstream service providers outside documented HIPAA responsibilities. Retaining the signed contract without its audit trail, making it harder to demonstrate signer identity, timing, and document history. Giving a vendor access to PHI before both parties execute the required written agreement under 45 CFR 164.504(e).
Business associate agreement troubleshooting
Resolve signing, HIPAA, and recordkeeping questions before a vendor receives protected health information.
A business associate agreement is not itself a HIPAA certification. Use signNow to document the contract, but separately assess safeguards, risk analysis, workforce controls, and breach procedures required by the HIPAA Security and Privacy Rules.
The signNow Business plan includes audit trails and templates. A BAA does not automatically add HIPAA safeguards to every workflow; signNow identifies HIPAA compliance as requiring a BAA, so confirm the applicable arrangement before sending PHI.
Use signNow’s signer authentication options, including SMS or stronger verification where configured, and preserve the audit trail. The agreement should identify authorized representatives and the business associate’s specific services.
Upload the agreement to signNow, review detected fields, place signature and date fields for each party, send it, and retain the completed document with its audit trail. Confirm the PDF reproduces the final terms accurately.
The agreement should address breach notification, permitted uses, safeguards, subcontractors, access or amendment requests, and return or destruction of PHI. Ask counsel to review terms against 45 CFR 164.504(e).
The HIPAA Privacy Rule requires relevant documentation retention for six years from creation or last effective date under 45 CFR 164.530(j). Set organizational retention controls accordingly and consider longer state or contractual requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.