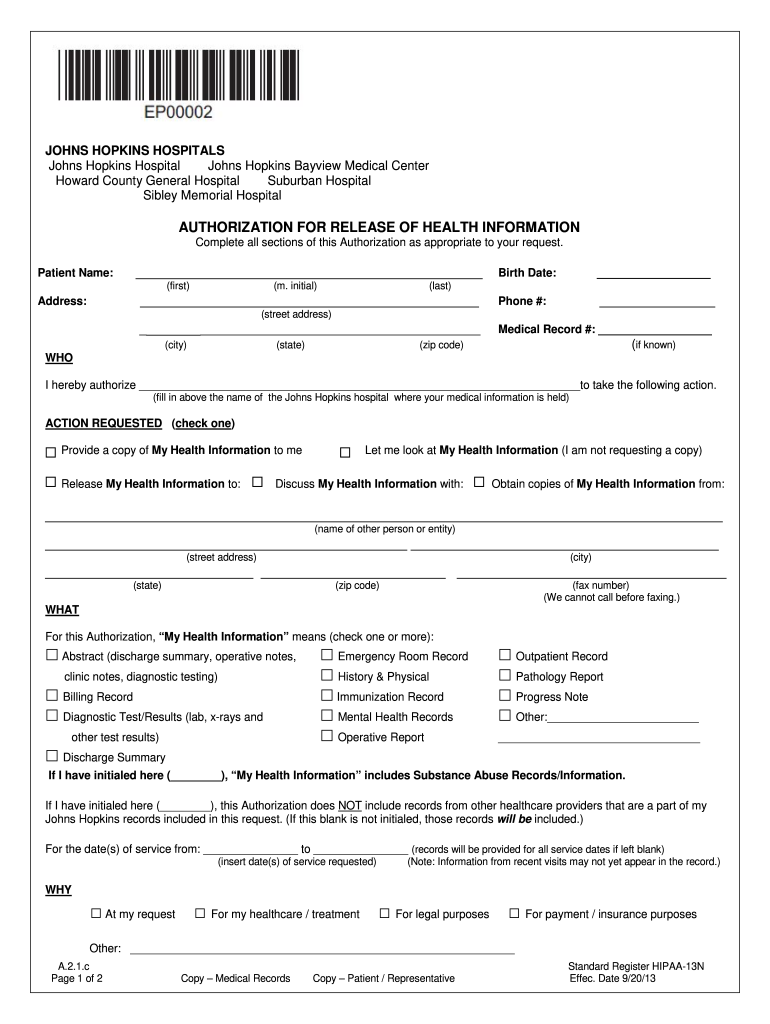
Authorization For Release Of Health Information Johns Hopkins Hopkinsmedicine
Create a custom Authorization For Release Of Health Information Johns Hopkins Hopkinsmedicine 2013 that meets your industry’s specifications.
What this health information authorization does
The Authorization For Release Of Health Information Johns Hopkins Hopkinsmedicine is a patient permission form that allows Johns Hopkins Medicine to disclose specified health information to named recipients. The patient identifies the records, purpose, recipient, expiration or event, and signature details before authorizing release. A completed form helps the provider verify consent and limit disclosure to the scope described. HIPAA governs covered entities’ use and disclosure of protected health information, while state privacy rules may impose additional requirements. Review every field before signing or sending.
Who uses this Johns Hopkins authorization
Patients and representatives
Patients or their legally authorized representatives complete the Johns Hopkins authorization to direct specified health records to another person, provider, insurer, attorney, or organization.
Receiving organizations
Healthcare, legal, and insurance teams use the signed form to document a defined disclosure request while limiting access to the recipient and records identified by the patient.
Features that support this authorization
The workflow combines field preparation, patient signing, disclosure controls, and evidence preservation for the Johns Hopkins release form.
Field detection
Upload the Johns Hopkins PDF and let signNow identify fillable areas before you review, correct, or add fields for the patient and recipient.
Signer routing
Route the authorization to the patient or legally authorized representative with defined signature, date, and acknowledgment fields.
Audit trail
Capture timestamps, signer activity, and document history so the completed release has supporting evidence for later review.
Mobile signing
Use mobile apps for patient-facing completion when a desktop workflow would delay a time-sensitive records request.
HIPAA controls
Protect health-information workflows with HIPAA compliance and a business associate agreement where the covered-entity arrangement requires one.
Secure records
Store the signed authorization and exported audit trail together for controlled retrieval and retention review.
How to complete the Johns Hopkins form
Complete the Johns Hopkins authorization by preparing the release scope, assigning the signer, and preserving the signed record with its audit trail.
Upload form: Upload the Johns Hopkins authorization PDF to signNow. Check fields: Review detected fields and add missing signature or date fields. Send request: Enter the authorized recipient’s email and send the request. Archive record: Store the signed authorization and audit trail securely.
Ways to send and sign the form
- Use the signNow web app when staff upload the Johns Hopkins authorization, place fields, and route it from a workstation.
- Use the signNow mobile app when a patient or representative reviews and signs the authorization from an iOS or Android device.
- Use kiosk mode at a supervised intake desk when a patient completes the Johns Hopkins release on an organization-managed device.
- Use a shareable signing link when the authorized signer must open the prepared Johns Hopkins form without a separate account.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended signNow setup
Use a controlled workflow that connects signer identity, the Johns Hopkins release scope, audit evidence, and protected retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with the completed authorization |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
Security for protected health information
HIPAA alignment:
Stored encryption:
Transit encryption:
Control assurance:
Security certification:
Electronic signatures:
Find and fill out the correct authorization for release of health information johns hopkins hopkinsmedicine
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2013 Standard Register HIPAA-13N [2013-09-20] 2013 | 4.8 Satisfied (8566 Votes) |
Privacy pitfalls to check before release
Selecting “all records” without a defined purpose can disclose more protected health information than the patient intended or the recipient needs. Entering an incorrect recipient email can expose the signed Johns Hopkins authorization and create an avoidable disclosure incident. Omitting an expiration date or event may leave staff uncertain about whether a later disclosure remains authorized under the form. Saving the signed PDF without its audit trail can weaken evidence showing who signed, when the authorization was completed, and whether the record changed.
Record-keeping practices for this authorization
Preserve the signed release, disclosure scope, audit evidence, and retention decision together so the authorization can be reviewed later.
Apply the six-year HIPAA documentation rule
Preserve the stated disclosure scope
Export and protect the audit trail
Control archival and secure disposal
What the audit trail records
The audit trail documents signing events and record history separately from the form’s substantive health-information authorization fields.
Authenticate signer:
Capture timestamps:
Track document history:
Seal record:
Export evidence:
Archive securely:



Healthcare authorization workflow examples
Healthcare teams can use a controlled electronic workflow for patient-directed disclosures while preserving the exact scope of the Johns Hopkins authorization.
Healthcare provider
Fertility Centers of Illinois needed a secure way to collect and manage patient-facing documents across its healthcare operations.
- Patient authorization routing
- Signed records with audit evidence
Fertility Centers of Illinois is a real signNow customer whose director described the platform’s API and responsiveness positively. For a Johns Hopkins health-information authorization, a comparable healthcare workflow can route the form electronically while preserving signer activity and supporting a documented HIPAA-compliant process when a BAA and proper controls are in place.
Healthcare legal review
A regional healthcare legal team needed patient-directed records for an authorized review without relying on paper routing between offices.
- Defined recipient and purpose
- Controlled disclosure documentation
An anonymized healthcare legal workflow can use signNow to upload the Johns Hopkins authorization, assign the patient or representative, capture the completed signature, and export the audit trail. The receiving team must still verify the release scope, applicable HIPAA requirements, state privacy law, and any separate authorization requirement.
Risks from incomplete authorization
Invalid consent
Excess disclosure
Privacy incident
Unauthorized release
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting the Johns Hopkins form
Resolve field, signer, privacy, and retention questions before releasing the completed authorization or using it to request protected health information.
The signNow Business plan includes templates and audit trails at $8 per user per month with annual billing. Upload the Johns Hopkins PDF, review detected fields, and add any missing patient, recipient, signature, or date fields before sending.
A signed release does not automatically authorize every disclosure. HIPAA requires the authorization to identify the information, recipient, purpose, and expiration or event. Confirm the Johns Hopkins form contains those elements and follow any stricter state privacy rule.
signNow is HIPAA compliant when the required business associate arrangement and configured safeguards apply. Confirm that the account, users, storage, and disclosure process are covered by the organization’s BAA and privacy policies before routing protected health information.
The Business Premium plan is listed at $15 per user per month with annual billing and includes bulk send. Bulk sending should not be used to distribute a patient-specific authorization unless each recipient and disclosure scope is independently verified.
If the signer cannot open the request, verify the email address, resend the invitation, or provide a controlled signing link. For health information, avoid forwarding the authorization through an unapproved channel and preserve the final audit trail.
signNow provides ESIGN and UETA support, but electronic validity does not replace HIPAA content requirements or state law. The signer must demonstrate intent, consent to electronic records, attribution, and access to a reproducible completed record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.