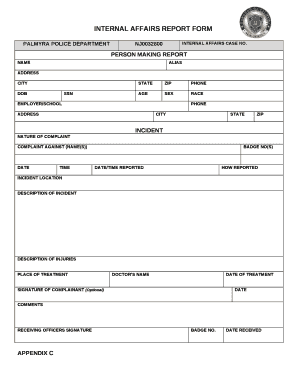
Internal Affairs Report Form
Use a Internal Affairs Report Template template to make your document workflow more streamlined.
What the Internal Affairs Report Form does
The Internal Affairs Report Form records an organization’s internal review, incident details, findings, and authorized approvals in one controlled document. Because the exact fields depend on the organization using it, the completed report should identify the matter, relevant dates, participants, supporting facts, and required reviewers without adding unsupported conclusions. With signNow, a sender uploads the report, checks detected fillable fields, adds signature or date fields, routes it to designated reviewers, and stores the completed document with its audit trail. Internal policy determines access, escalation, and retention.
Who uses the Internal Affairs Report Form
Internal affairs teams
Internal affairs units can use the form for incident narratives, interview summaries, evidence reviews, findings, and approval records. signNow helps route the report to authorized reviewers, capture signatures, and retain the completion history without changing the organization’s investigative policy.
Compliance departments
HR, compliance, and government departments can use the form for employee-related investigations, policy reviews, and sensitive administrative findings. Access controls, reviewer order, and retention should follow the organization’s privacy rules, state law, and any applicable federal requirements.
Who benefits from internal affairs reports
The form is most useful where an investigation requires structured facts, designated reviewers, and a defensible record of approval.
Internal affairs teams use the form to document allegations, interview findings, evidence reviewed, and final approvals while keeping each matter distinct and access-controlled. Human resources and compliance departments use it to coordinate investigations, obtain designated sign-offs, and preserve a traceable record for policy or regulatory review. Government and regulated organizations use controlled signing workflows when internal reports contain sensitive information requiring identity checks, limited access, and documented retention.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the internal report workflow works
Complete the Internal Affairs Report Form, route it to authorized reviewers, and preserve the signed record with its audit history.
Upload report: Upload the completed report and confirm its required fields. Place fields: Review detected fields and add signature or date fields. Send for review: Send the report to authorized internal reviewers. Archive record: Store the signed report with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The signNow audit trail connects reviewer identity, report actions, timestamps, document integrity, and retrievable completion evidence.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Link history:
Export evidence:
Key features for internal affairs reporting
signNow organizes the report from field preparation through review, signature, audit evidence, and controlled record storage.
Field preparation
Upload the Internal Affairs Report Form and review detected fields before adding signatures, dates, or approval fields required by your organization’s procedure.
Reviewer routing
Route the report to named reviewers in the required order, reducing uncertainty about who must examine or approve each internal finding.
Audit evidence
Capture signer identity, timestamps, actions, and document history in an audit trail that stays associated with the completed report.
Reusable templates
Use templates for recurring internal report formats while preserving the specific incident facts entered for each matter.
Mobile signing
Review and sign the report from a supported mobile app when authorized personnel work away from a desktop.
Record control
Keep the signed report and completion evidence together for controlled access, later review, or organizational recordkeeping.
Recommended report workflow setup
Configure the Internal Affairs Report Form around reviewer identity, signing evidence, secure transmission, and the organization’s approved retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Verified email with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Retain completion certificate and action history |
| Document retention | Follow organizational policy and state law |
| Encryption | TLS 1.2 or TLS 1.3 and AES-256 |
Mobile options for internal reports
The signNow mobile apps support Internal Affairs Report Form workflows on iOS and Android, including document capture and signing when users are away from a desktop.
iOS app iOS 15 or later Android app Android 10 or later Mobile tools Offline signing and camera capture
Teams should manage mobile access through approved devices and organizational policies. Camera capture can digitize a paper report, while offline signing supports work without connectivity before synchronization and audit-trail completion.
Legal standing of internal reports
A completed Internal Affairs Report Form can support a U.S. business record when signer intent, consent, attribution, and reliable retention are demonstrated under ESIGN and applicable UETA rules. Those frameworks do not cover wills, codicils, testamentary trusts, court orders, or specified family-law documents.

Security for internal reports
Transit encryption:
Storage encryption:
Security certification:
Management standard:
Health data protection:
U.S. eSignature law:
Recordkeeping practices for internal reports
Use a documented review, access, and retention process so every completed Internal Affairs Report Form remains understandable and traceable.
Verify report completeness before routing
Preserve the audit trail with the report
Apply the correct retention rule
Restrict access after completion
Challenges when completing internal reports
Sensitive allegations or identifying details may be exposed when a completed report is shared through an unrestricted link or forwarded outside the approved review group. Missing reviewer signatures, dates, or consent evidence can make the report’s approval history difficult to establish during an internal investigation. Copying unverified conclusions into the report can compromise fairness, accuracy, and the organization’s ability to distinguish facts from allegations. Keeping the signed report without its audit trail can weaken the evidence connecting the final document to the recorded review event.
Troubleshooting Internal Affairs Report Form
Resolve field, authentication, plan, and compliance questions before distributing the completed Internal Affairs Report Form.
Business includes legally binding eSignatures, templates, and audit trails. Check that the Internal Affairs Report Form is uploaded as a supported document, then confirm required signature fields before sending it for review.
The Business plan supports audit trails, while Business Premium adds bulk send and kiosk mode. For a single Internal Affairs Report Form, verify the document fields manually; bulk-send tools are not required for one report.
signNow supports ESIGN and UETA requirements, including signer intent, attribution, and record retention. Organizational policy and state requirements still determine whether this internal report needs additional approvals, notarization, or access controls.
Use signNow authentication options available to your plan, such as email delivery or stronger signer authentication where configured. Confirm the reviewer’s identity and preserve the completed report and audit trail together.
Business includes audit trails, and Enterprise adds advanced signer authentication. If a report requires stronger identity controls, administrators should select an appropriate plan configuration and document the approval policy separately.
signNow encrypts data in transit with TLS 1.2 or TLS 1.3 and at rest with AES-256. HIPAA workflows require a business associate agreement, and regulated teams should confirm their own retention and access policies.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.