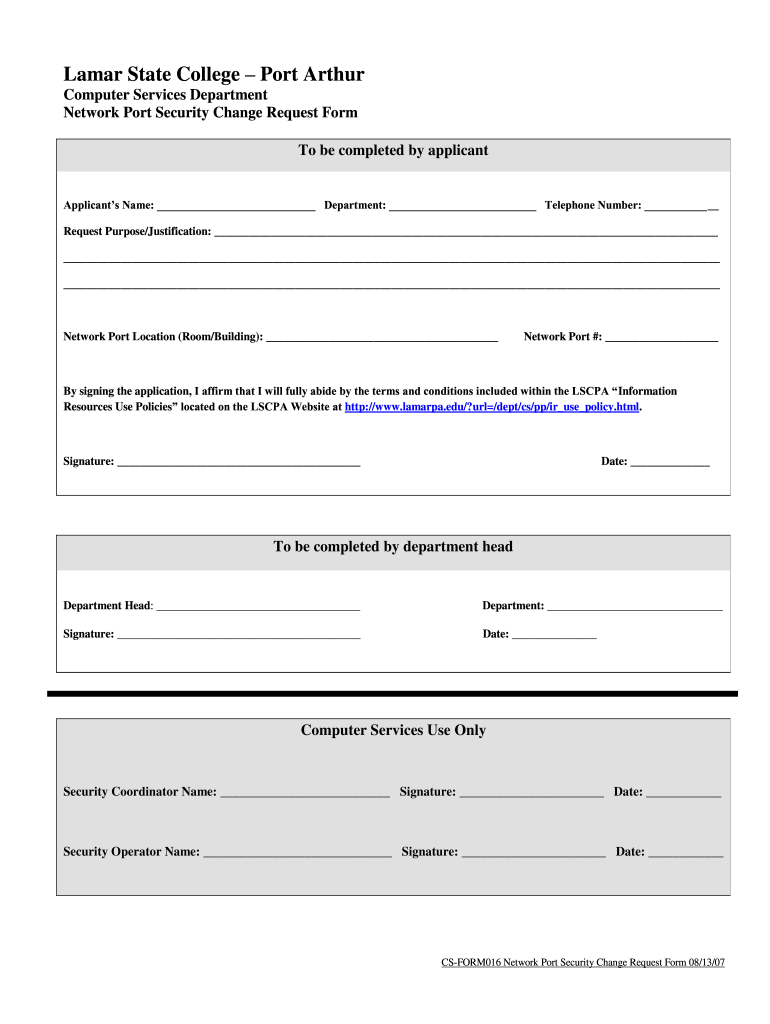
Network Port Security Change Request Form Lamarpa
Create a custom Network Port Security Change Request Form Lamarpa 2007 that meets your industry’s specifications.
What this network port request does
The Network Port Security Change Request Form Lamarpa records a proposed network-access change for review and approval. It gives network and security teams a controlled place to document the affected systems, ports, protocols, direction, business justification, requested timing, and responsible approvers. In signNow, the uploaded request can be checked for fillable fields, routed to designated signers, completed electronically, and stored with an audit trail. The form name does not identify a federal filing deadline or issuing agency, so internal security policy governs submission and implementation timing.
Who uses this network change form
Network operations
Network administrators complete requested port, protocol, source, destination, and justification fields before routing security approval.
Security teams
Security teams review authorization, apply required authentication, and retain the signed request with its audit trail.
Features for network port change approvals
signNow connects the Lamarpa request’s network details, reviewer sequence, signer authentication, and final audit record into one documented workflow.
Field detection
Upload the Lamarpa request and review detected fields before adding missing network details, reducing manual recreation of the original document.
Approval routing
Route the request to named network and security reviewers in sequence, keeping approval responsibilities visible before implementation begins.
Audit trail
Capture timestamps, signer actions, and document history so the completed request retains supporting evidence for later change review.
Signer authentication
Use SMS OTP or other configured authentication controls when the organization requires stronger attribution for sensitive network changes.
Secure storage
Keep the signed request and completion record together in a controlled workspace, supporting consistent retrieval during audits or incident reviews.
Reusable templates
Use templates for recurring port-change requests while preserving the specific ports, protocols, systems, and justification for each submission.
Complete the network port request online
Upload the form, verify its network-change fields, route it to authorized reviewers, and preserve the completed record with its audit trail.
Upload form:
Upload the Network Port Security Change Request Form Lamarpa PDF. Check fields:
Review detected fields and add missing port-change details. Assign reviewers:
Assign network, security, and business approvers in order. Send request:
Send the request and monitor completed signatures. Archive record:
Store the signed PDF with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Audit trail for network port approvals
The audit trail documents who handled the Lamarpa request, when actions occurred, and how the completed record can be retrieved after approval.
Authenticate signer:
Capture timestamps:
Record document history:
Seal completion:
Store certificate:
Export audit trail:
Processing stages for network port requests
Processing depends on accurate network details, assigned reviewers, and each signer’s response; no form-specific statutory deadline is provided.
Prepare request
Deliver to signers
Collect signatures
Complete and archive
Find and fill out the correct network port security change request form lamarpa
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2007 Lamar State College CS-Form016 Network Port Security Change Request Form [2007-08-13] 2007 | 4.8 Satisfied (5076 Votes) |
Retention rules for signed network records
Keep the completed request and audit trail together. Apply the governing rule for the record’s business context, and document any longer state or industry requirement.
Three years for change records
Six years for HIPAA records
Three years for payroll records
Five years for injury records
Thirty years for exposure records
Common network request pitfalls
Missing source and destination ports can prevent reviewers from determining the requested firewall or access-control change. Unclear business justification may delay approval because security reviewers cannot connect the requested change to an operational need. Incorrect approver routing can leave a network change unsigned by the person responsible for security authorization. Separating the signed request from its audit trail can weaken the record’s evidentiary context during later review.
Risks of incomplete network approvals
Approval gap
Weak attribution
Missing audit trail
Incorrect port details
Platform requirements for signing requests
Use signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. Mobile signing is available through iOS and Android apps, while TLS 1.2/1.3 protects data in transit.
Browser support Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Transport security TLS 1.2/1.3 protects data in transit
Organizations handling network-change records should use managed devices, controlled account access, and documented provisioning procedures. Enterprise deployments may require API access, SSO provisioning, or certificate configuration; select those controls according to internal security policy and the sensitivity of the requested port change.
Legal standing of signed network requests
For U.S. business transactions, an electronic Network Port Security Change Request Form Lamarpa may be admissible when intent, consent, signer attribution, and reliable record retention are demonstrated under ESIGN and applicable state law, including UETA or New York’s ESRA. ESIGN exclusions include wills, certain court orders, and family law decrees.

Troubleshoot this network change request
Resolve field, routing, authentication, plan, and compliance questions before the Network Port Security Change Request Form Lamarpa is finalized.
If field detection misses a port or protocol field, open the uploaded PDF in the editor and place the required fields manually before sending. signNow Business includes templates and audit trails for preserving the corrected request.
If an approver cannot access the request, confirm the recipient email address, resend the invitation, or provide a controlled signing link. Business Premium includes quick invite links, while every paid plan includes mobile signing access.
If stronger identity proof is required, configure advanced signer authentication available with Enterprise. SMS verification can add a second factor, but organizational policy should define when it is mandatory.
For consumer-facing records, ESIGN requires disclosure of the right to paper records, electronic access, and consent withdrawal procedures under 15 U.S.C. §7001(c). Configure and retain that disclosure with the request when applicable.
Business costs $8/user/month with annual billing and includes legally binding eSignatures, audit trails, templates, and mobile apps. The plan includes 100 signature invites per user annually, with overage fees.
If the request contains protected health information, signNow identifies HIPAA compliance as requiring a Business Associate Agreement. Confirm the organization’s BAA and six-year retention obligation under 45 CFR 164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.