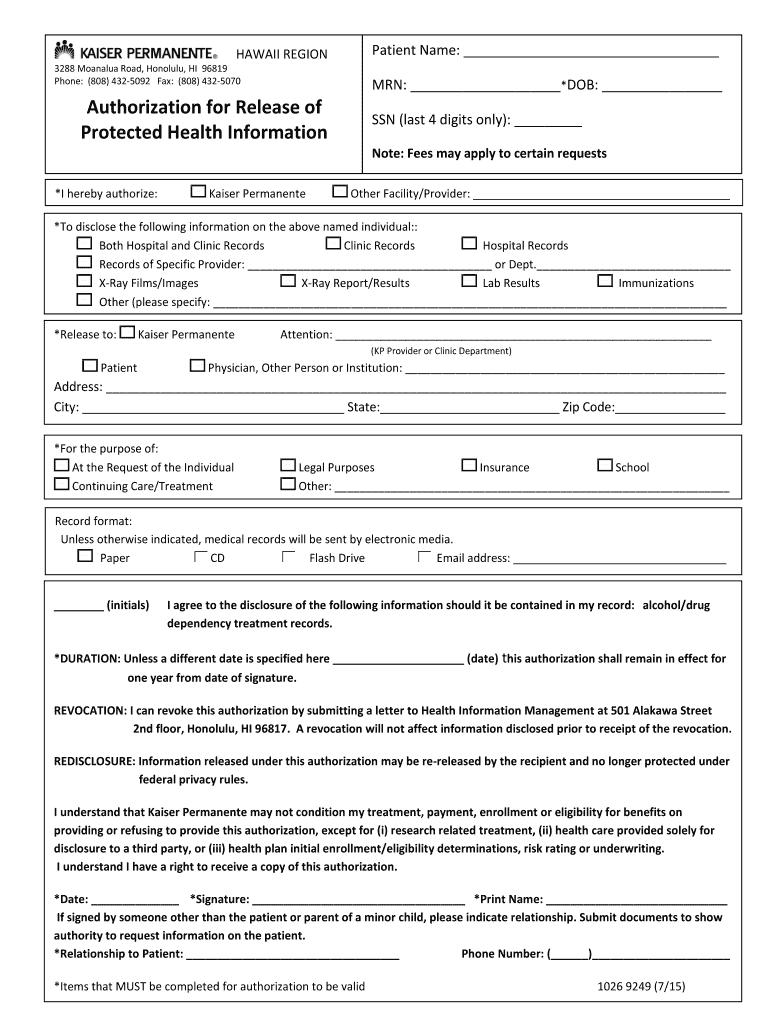
Kaiser Hawaii Medical Records Form
Get the Kaiser Hawaii Medical Records 0 template, fill it out, eSign it, and share it in minutes.
What the Kaiser Hawaii Medical Records Form does
The Kaiser Hawaii Medical Records Form is a written authorization used to request, disclose, or direct access to a patient’s medical information through Kaiser Permanente’s Hawaii operations. It identifies the patient, the records or date range involved, the recipient, the purpose, and the authorization period. The patient or legally authorized representative signs the form, then the request is reviewed under HIPAA and Kaiser’s release procedures. Use the current Kaiser instructions to confirm required fields, delivery options, and whether a representative’s documentation is needed.
Who uses this medical-records form
Healthcare release teams
Healthcare release coordinators use the form to document patient-authorized disclosures, confirm the recipient, and retain evidence that the request matched the signed authorization. They should limit the record scope, verify identity, and follow Kaiser’s current Hawaii release instructions before transmitting information.
Patients and representatives
Patients and authorized representatives use the form when directing Kaiser Hawaii to send records to another provider, attorney, insurer, employer, or personal address. The signer should review the purpose, recipient, information categories, expiration terms, and any representative documentation before signing.
Features that support Kaiser records requests
signNow connects form preparation, controlled signing, audit evidence, and protected storage for Kaiser Hawaii medical-record authorizations.
Form preservation
Upload the Kaiser authorization PDF and prepare it without recreating the form. The original layout remains available for review while required signature and date fields are added.
Field preparation
Auto-detect fillable areas, then check patient, recipient, purpose, and authorization fields manually before sending. This reduces omissions without changing Kaiser’s underlying document.
Signer routing
Send the authorization to the patient or representative by email, or use a controlled signing link when the workflow requires it. Each signer receives the assigned fields.
Audit evidence
Capture signer actions, timestamps, and document history in an Audit Trail. Export the completed evidence with the authorization for release-team review and records management.
HIPAA workflow
Use HIPAA-compliant signNow workflows with a business associate agreement when protected health information is handled. Compliance still depends on configuration, access controls, and Kaiser procedures.
Secure storage
Keep the signed authorization and completion evidence in a restricted repository such as Box, Egnyte, or Google Drive, subject to the organization’s access policy.
How the Kaiser form workflow works
Complete the Kaiser Hawaii authorization through four controlled stages, from document preparation to protected storage of the signed record.
Upload form: Upload the Kaiser authorization PDF to signNow. Prepare fields: Review detected fields and add missing signer fields. Send securely: Send the authorization to the patient or representative. Archive evidence: Store the signed form with its Audit Trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for records authorizations
Configure the Kaiser authorization workflow around verified identity, limited access, audit evidence, and HIPAA recordkeeping requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export certificate and action history |
| Document retention | Six years under 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 encryption |
What the signNow audit trail records
The audit trail documents the technical history of a Kaiser authorization from signer verification through retrieval of the completed evidence.
Signer authentication:
Timestamp capture:
Document integrity:
Tamper evidence:
Delivery history:
Audit export:



Security controls for medical records
HIPAA protection:
Transport encryption:
Storage encryption:
SOC 2 controls:
ISO 27001 controls:
Audit history:
Privacy and disclosure pitfalls
Attaching the wrong patient’s records or leaving unrelated diagnoses visible can disclose protected health information beyond the authorization’s stated scope. A missing patient signature, representative authority, purpose, or recipient may prevent Kaiser from processing the medical-record request. Sending a signed authorization to an unverified email address can expose sensitive information before the intended recipient confirms access. Leaving completed forms available to every workspace user can exceed the minimum-necessary access expected under HIPAA.
Record retention and archival practices
Preserve the authorization, disclosure evidence, and audit history as one controlled record set.
Apply the six-year HIPAA retention rule
Export the audit trail with the record
Archive records in a restricted location
Track authorization scope and expiration dates
Retention periods for related records
Apply the retention rule that matches the underlying record, and confirm Kaiser or state requirements before deleting a medical-record authorization.
Six years for HIPAA records
Three years for tax records
Three years for payroll records
Five years for injury records
Thirty years for exposure records
State and document limitations
Processing delay
Unauthorized disclosure
Release limitation
Authority dispute
Kaiser records form troubleshooting
Use these answers to resolve field, consent, authentication, audit, and compliance questions before releasing medical records.
Upload the original Kaiser Hawaii Medical Records Form as a PDF, then use signNow’s field detection and manually review every required patient, recipient, purpose, and signature field. Auto-detection prepares fields but does not determine whether Kaiser’s current form instructions are satisfied.
A signNow Business subscription includes templates and audit trails, while Business Premium adds bulk send. Choose the plan based on workflow volume, but confirm that the selected configuration includes the controls required for protected health information and a BAA.
HIPAA compliance does not make every disclosure permissible. Verify the patient’s identity, authorization scope, recipient, purpose, and expiration before sending. signNow states HIPAA compliance requires a BAA, while the organization remains responsible for minimum-necessary access and release procedures.
Use signNow’s SMS OTP or stronger authentication options when the organization requires more than email verification. Confirm the signer’s phone number independently, and do not treat an OTP as proof that the requested record scope is correct.
Export the completed document and Audit Trail after all signers finish. The Audit Trail records actions and timestamps, but it should be stored with the Kaiser authorization in a restricted repository rather than left only in an inbox.
Electronic signatures generally receive legal recognition under ESIGN, 15 U.S.C. chapter 96, and applicable UETA law when intent, consent, attribution, and record reproduction are established. Confirm Kaiser’s current process for any request requiring a different signature or delivery method.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.