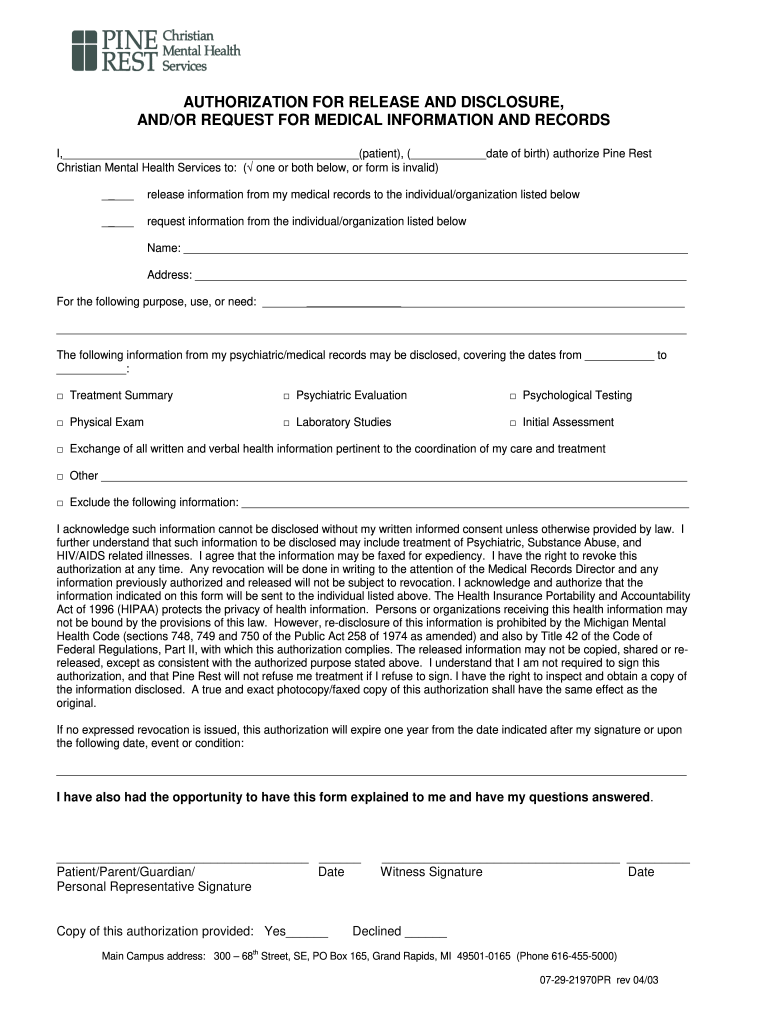
Pinerest Release Of Information
Create a custom Pinerest Release Of Information 2003 that meets your industry’s specifications.
What Pinerest Release Of Information does
Pinerest Release Of Information is an authorization used to permit a named recipient to receive specified information about the individual identified in the document. The signer reviews the records, recipient, purpose, and expiration, then signs to record consent. With signNow, a sender uploads the release, places or confirms fillable fields, routes it to the authorized signer, and retains the executed PDF with an Audit Trail. If protected health information is involved, HIPAA requirements, organizational policy, and applicable state law govern the disclosure and retention process.
Who uses this release and why
Healthcare providers
Healthcare providers and medical-records departments use the release to authorize disclosure of patient records to a named recipient, including another provider, insurer, attorney, or representative.
Authorized signers
Patients, authorized representatives, and recipients review the information scope, purpose, expiration, and signature fields before the completed authorization is used for disclosure.
Who works with this release
A clinic’s health-information coordinator uses the release to collect patient or representative authorization before sending records to a named provider, insurer, attorney, or other recipient. The coordinator checks scope and expiration, then preserves the signed document and audit evidence with the disclosure record for later review if questions arise over consent or access control. A medical-records administrator manages multiple release requests across departments and uses reusable signNow templates to standardize names, dates, recipient details, and signature fields. The administrator can route the completed authorization to approved staff while limiting access to patient information according to the organization’s privacy policy and HIPAA obligations.
Features that fit this release workflow
Pinerest Release Of Information workflows need clear authorization fields, verified routing, evidence of consent, and controlled storage for sensitive records.
Fillable fields
Upload the Pinerest release as a PDF and use detected or placed fields for names, recipient details, authorization dates, signatures, and required acknowledgments. This keeps the document structure visible while preparing it for electronic completion.
Signer routing
Send the authorization to the named signer by email or signing link after reviewing recipient identity and field assignments. The signer can open the document, review its scope, and apply the requested signature electronically.
Audit trail
Capture timestamps, signer actions, delivery events, and document history in a signNow Audit Trail. These records provide supporting evidence when staff need to explain how the authorization was completed and returned.
Authentication
Use two-factor authentication or SMS OTP when stronger signer verification is required by the organization’s release process. HIPAA-covered workflows should also account for the required business associate agreement and access controls.
Secure storage
Retain the completed PDF and audit evidence in an approved repository with restricted permissions. For health information, align the archive with HIPAA 45 CFR 164.530(j) and any longer state retention requirement.
Reusable template
Use templates for recurring release requests while preserving recipient, record-scope, expiration, and signature fields for each individual authorization. Templates reduce rework without turning one patient’s authorization details into another patient’s document.
Recommended setup for this release
Configure the authorization workflow around signer identity, consent evidence, protected information, and retention requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with intent |
| Audit trail | Export with completed PDF |
| Document retention | Six years under 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS in transit |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete this release in signNow
Use signNow to prepare the release, capture the required authorization, and preserve a reviewable record of the completed disclosure permission.
Upload:
Upload the release PDF Detect fields:
Let signNow detect fields Review:
Review names and scope Send:
Send to the authorized signer Complete:
Collect the completed release Archive:
Store the PDF and audit trail
What the audit trail records
The audit trail separates the authorization workflow from the release content and preserves technical evidence about how the document was signed.
Authenticate signer:
Timestamp event:
Hash document:
Seal history:
Log activity:
Export trail:
Find and fill out the correct release of information form pine rest
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2003 Pine Rest 07-29-21970PR [2003-04] 2003 | 4.8 Satisfied (6656 Votes) |
Security controls for this release
Data at rest:
Data in transit:
Health information:
Independent controls:
Information security:
Privacy controls:
Document retention practices for this release
Preserve the signed authorization, evidence of consent, and disclosure history under the applicable health-information retention rule.
Apply the six-year HIPAA retention period
Export the signed release and audit trail
Archive releases with restricted access
Verify scope before sending records
Privacy and disclosure pitfalls
Including a broad record category without naming the intended recipient can make the authorization difficult to review before disclosure. Sending the release to an unverified email address can expose personal health information before the signer’s identity is confirmed. Leaving the purpose, expiration, or representative authority incomplete creates uncertainty about whether the requested disclosure matches the signed authorization. Saving only the signed PDF without its Audit Trail removes useful evidence about delivery, signer actions, timestamps, and document history.
Risks from mishandling this release
Disclosure challenge
Scope error
Evidentiary gap
Privacy exposure
Authorization lapse



Troubleshooting Pinerest Release Of Information
Resolve authorization, identity, privacy, and archival issues before the release is used to disclose information.
signNow can route the release to the intended signer and preserve the completed PDF with an Audit Trail. Before sending, verify the email address, representative status, recipient, record categories, expiration, and signature fields. If the release covers protected health information, confirm that the workflow uses an appropriate HIPAA configuration and BAA.
A signed release may be insufficient if it does not identify the information, recipient, purpose, or expiration required by the organization’s authorization policy. Update the template or fields before sending, then have the signer complete a fresh document. Do not edit the executed PDF to repair missing authorization terms.
signNow Business includes legally binding eSignatures, templates, mobile apps, and audit trails at $8/user/month with annual billing. Business Premium is $15/user/month annually and adds bulk send. Choose a plan based on the release volume and required controls rather than assuming every feature appears on Business.
HIPAA compliance requires a business associate agreement when signNow handles protected health information for a covered entity or business associate. The product-side compliance status does not replace your privacy, access, minimum-necessary, retention, or disclosure procedures under HIPAA.
The signNow Audit Trail records signing activity, timestamps, delivery events, and document history. Export it with the completed release and preserve both files in an access-controlled archive. For HIPAA-related records, apply the six-year rule in 45 CFR 164.530(j), unless state law or policy requires longer retention.
If a signer cannot complete the document, check field assignments, email delivery, browser access, and authentication requirements. Resend only after confirming the recipient identity and authorization scope. A new request should use the corrected release rather than relying on an incomplete or altered signing session.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.