HIPAA Authorization Form (2003 2026)
Create a custom Sample Hipaa Authorization Form 2003 that meets your industry’s specifications.
What the HIPAA Authorization Form does
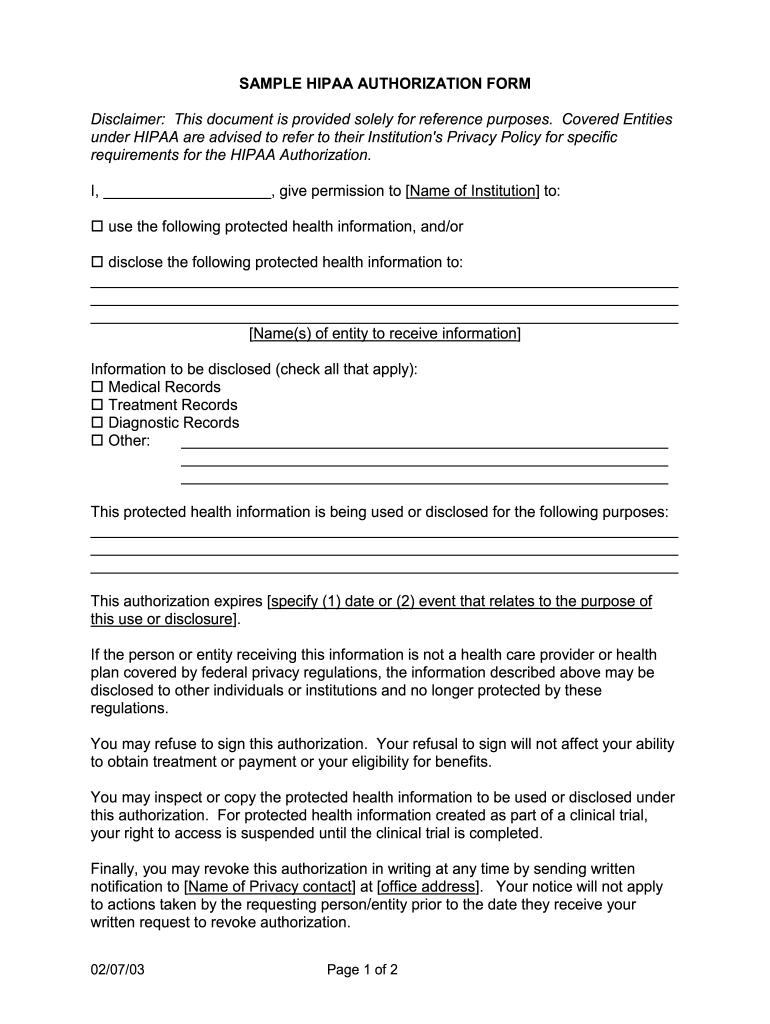
A HIPAA Authorization Form lets a patient authorize a covered entity to disclose specified protected health information to a named person or organization. It identifies the information covered, the recipient, the purpose, the patient’s signature, and an expiration date or event. Under 45 CFR §164.508, the authorization also addresses required statements about revocation, conditioning treatment or payment, and redisclosure. With signNow, the sender uploads the form, places fields, routes it to the patient, and stores the completed record with an audit trail.
Business types using this form
Healthcare organizations use this form when a patient’s written permission is needed before specified protected health information is disclosed.
Solo healthcare practitioners can send a patient-specific authorization for records disclosure, collect the signature remotely, and retain the completed form with an audit trail instead of coordinating repeated paper exchanges. Regional clinics can standardize authorization fields across departments, route forms to patients and representatives, and control access while processing releases for treatment, payment, operations, or another stated purpose. Enterprise health systems can connect authorization workflows with managed users, templates, and integrations, while requiring a BAA, role-based access, and six-year HIPAA documentation retention under 45 CFR §164.530(j).
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who completes and receives this form
Healthcare providers
Healthcare providers use the HIPAA Authorization Form for patient-approved disclosure requests, including releases to attorneys, insurers, family representatives, or other named recipients. The form should identify the information, recipient, purpose, expiration, revocation statement, and patient signature before staff release the records.
Patients and representatives
Patients and personal representatives use the form to authorize a defined disclosure. The recipient receives only the information and access described in the authorization, subject to HIPAA, state privacy law, and the covered entity’s release procedures.
Key features for HIPAA authorization workflows
A HIPAA Authorization Form must identify the information, recipient, purpose, and signer clearly; signNow keeps those details together through completion and storage.
Reusable template
Upload the HIPAA Authorization Form once, then reuse its fields and signer roles for patient, provider, or representative authorization workflows without rebuilding the document.
Required fields
Place required authorization fields for the patient, recipient, information scope, expiration date, and signature so incomplete disclosures are easier to identify before sending.
Signer routing
Route the form to patients, personal representatives, or healthcare organizations in the intended order, keeping each signer’s responsibility visible throughout completion.
Audit trail
Capture email, timestamps, IP details, and document history in an audit trail that helps demonstrate how the HIPAA Authorization Form was completed.
HIPAA controls
Use signNow’s HIPAA-compliant workflow with a business associate agreement where required, helping organizations manage protected health information during electronic signing.
Secure recordkeeping
Store the completed authorization and its audit trail together so staff can retrieve the signed disclosure record when a patient or compliance reviewer requests it.
How the authorization workflow works
The workflow preserves the form’s disclosure details while moving it from preparation through signing, completion, and audit-ready storage.
Upload form: Upload the HIPAA Authorization Form Place fields: Detect and place patient authorization fields Route signing: Send to each required signer Archive record: Store signed record and audit trail
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the signNow audit trail records
The audit trail documents the signing event around this authorization, helping staff connect the patient’s action with the final disclosure permission.
Authenticate signer:
Capture timestamps:
Track document history:
Seal record:
Store completion proof:
Export audit trail:
Choose the right signing method
- Use the signNow web app when staff prepare the HIPAA Authorization Form, place patient and recipient fields, and send it from a desktop workflow.
- Use the signNow mobile app when clinicians or patients need to review and sign the HIPAA Authorization Form on iOS or Android away from a workstation.
- Use kiosk mode for an in-person intake desk where a patient completes the HIPAA Authorization Form on an organization-controlled device with staff assistance.
- Use a shareable signing link when a clinic needs to distribute the same HIPAA Authorization Form through a patient portal, website, or secure message.
Find and fill out the correct sample hipaa form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2003 Sample HIPAA Authorization Form [2003-07-02] 2003 | 4.8 Satisfied (2057 Votes) |
Platform requirements for signing
The HIPAA Authorization Form can be prepared through signNow’s web experience using Chrome, Firefox, Safari, or Edge on Windows 10 or macOS 12 and later. signNow also provides mobile apps for iOS, iPadOS, and Android, subject to current app support.
Supported browsers Chrome, Firefox, Safari, Edge Desktop systems Windows 10, macOS 12 Mobile systems iOS, Android, iPadOS
Regulated deployments should use managed Windows, macOS, iOS, iPadOS, or Android devices with current security updates. Administrators should confirm TLS 1.2 or 1.3 transport, access permissions, SSO or API requirements, and the certificate or long-term validation settings required by organizational policy.
Signer authentication and certificates
PKI signatures:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Document integrity:
Compare electronic authorization tools
signNow, DocuSign, and Adobe Acrobat Sign can support electronic authorization workflows; confirm each vendor’s current plan, BAA terms, and healthcare configuration before deployment.
| signNow | DocuSign | Adobe Acrobat Sign | |
|---|---|---|---|
| HIPAA authorization workflows | Yes | Yes | Yes |
| Electronic signature support | Yes | Yes | Yes |
| Audit trail availability | Yes | Yes | Yes |
| HIPAA compliance conditions | BAA required | BAA available | BAA available |
Privacy pitfalls to prevent
Listing a broad recipient without identifying the person or class of persons may make the authorization unsuitable for the intended disclosure. Describing protected health information vaguely can create uncertainty about whether the requested medical records fall within the patient’s consent. Omitting the purpose, expiration date, or revocation instructions can weaken the authorization’s operational usefulness and complicate release decisions. Sharing the completed form through uncontrolled email or assigning excessive workspace permissions can expose protected health information beyond the intended care or payment workflow.
Recordkeeping practices for HIPAA forms
Good recordkeeping connects the signed authorization, audit trail, disclosure scope, and retention decision without expanding access to protected health information.
Retain authorization records for six years
Export the audit trail with each form
Limit access to disclosure records
Track revocation and expiration events
Retention schedule for authorization records
HIPAA documentation has a six-year federal retention rule, while state law and organizational policy may require longer preservation for specific healthcare records.
Six years for HIPAA records
Six years for authorization copies
Six years for audit trails
State period may exceed six years
Policy-defined revocation record
Troubleshoot HIPAA authorization workflows
Most issues involve missing authorization elements, signer access, BAA configuration, or retention controls rather than the signature itself.
The HIPAA Authorization Form should identify the person or class of persons authorized to disclose information, the recipient, the information covered, the purpose, and an expiration date or event. Review those fields before sending through signNow.
signNow identifies HIPAA compliance as requiring a business associate agreement. A healthcare organization should confirm the applicable BAA and plan configuration before placing protected health information into an electronic authorization workflow.
The signNow Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps. The product ground truth does not state that every HIPAA add-on is included, so verify plan eligibility and BAA terms.
If a signer cannot open the form, check the invitation address, browser session, and signing link. signNow supports web and mobile workflows; resend the invitation after confirming the signer’s identity and access route.
For stronger identity assurance, use signNow authentication options available to the selected plan, including SMS-based verification where configured. Match the method to organizational policy and the sensitivity of the protected health information.
HIPAA requires covered entities to retain required documentation for six years from creation or the last effective date under 45 CFR §164.530(j). Configure archival procedures so the signed form and audit trail remain reproducible.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.