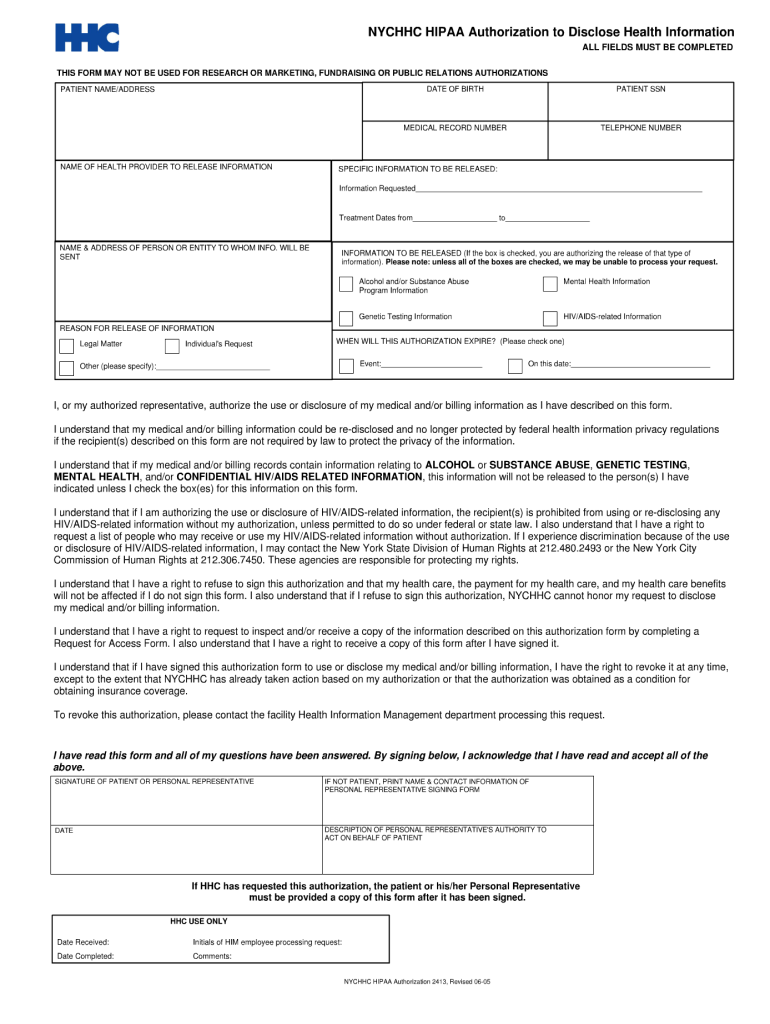
HIPAA Authorization
Get the Hipaa Authorization Fillable 2005 template, fill it out, eSign it, and share it in minutes.
What HIPAA Authorization does
HIPAA Authorization is a patient’s written permission for a covered entity or business associate to use or disclose specified protected health information for a stated purpose. It identifies the information, recipient, purpose, expiration, and signer. A healthcare organization uses it when disclosure is not otherwise permitted by HIPAA. The signed record demonstrates the patient’s authorization and supports controlled release. Electronic signing may be recognized under ESIGN and state electronic-transactions law when intent, consent, attribution, and record retention are established.
Who benefits from HIPAA Authorization
HIPAA Authorization is most useful when a healthcare organization must document a patient’s specific permission before releasing protected health information.
Solo behavioral-health practices use HIPAA Authorization to obtain patient permission before disclosing records to another provider, attorney, insurer, or family member, while preserving a signed copy and audit evidence. Regional medical groups use reusable authorization templates for referrals, care coordination, and records requests, giving compliance staff consistent fields, signer routing, and controlled access across multiple clinics. Enterprise health systems use role-based administration and delegated sending to manage authorizations across departments, connect records workflows, and retain signed documents with audit trails for compliance review.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who completes HIPAA Authorization
Healthcare providers
Healthcare providers, clinics, and medical groups use HIPAA Authorization to document patient permission before releasing specified protected health information to another person or organization.
Patients and representatives
Patients and their authorized representatives review the information scope, recipient, purpose, expiration, and signature before a covered entity processes the requested disclosure.
How to complete HIPAA Authorization
Use signNow to prepare the patient authorization, route it to the required signer, and preserve the completed record for later disclosure review.
Upload form:
Upload the authorization PDF Prepare fields:
Detect or place patient fields Route form:
Add recipients and signing order Complete authorization:
Review and sign electronically Retain copy:
Store the signed record securely
How HIPAA Authorization works online
The signNow workflow moves the authorization from document preparation through patient signing and auditable record storage.
Upload document: Upload the HIPAA Authorization Prepare fields: Place required patient and recipient fields Send request: Send for electronic signature Retain record: Store the completed authorization
Recommended HIPAA Authorization setup
Configure authentication, signatures, audit evidence, retention, encryption, and access before sending patient authorization forms.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture IP, timestamps, and action history |
| Document retention | 6 years under 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.


Features that support HIPAA Authorization
These signNow capabilities map directly to preparing, signing, reviewing, and retaining a patient authorization for protected health information.
Defined scope
Capture the patient’s permission, recipient, purpose, information scope, and expiration in one controlled document before disclosure processing.
Fillable fields
Upload the HIPAA Authorization and use detected or placed fields for patient, representative, recipient, date, and signature information.
Signer routing
Route the authorization to the patient or personal representative and monitor completion without exchanging editable files by email.
Audit trail
Preserve signing events, timestamps, IP details, and action history with the completed authorization for later review.
Secure retention
Keep the signed authorization with restricted access and a documented retention decision under 45 CFR §164.530(j).
HIPAA controls
Use a HIPAA workflow with a Business Associate Agreement when signNow processes protected health information for the covered entity.
Find and fill out the correct hipaa authorization form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2005 NYC NYCHHC HIPAA Authorization 2413 [2005-06] 2005 | 4.8 Satisfied (2180 Votes) |
Legal standing of HIPAA Authorization
A HIPAA Authorization can provide admissible evidence when it shows signer intent, consent, attribution, and a reproducible retained record under ESIGN and applicable state law. Electronic-signature rules do not cover wills, codicils, testamentary trusts, certain court orders, or specified family-law documents.

Security for HIPAA Authorization records
HIPAA:
BAA requirement:
Transport encryption:
Storage encryption:
Security certification:
Information security:
What the HIPAA Authorization audit trail records
A signNow Audit Trail documents the technical events that connect the patient’s electronic signature with the completed authorization.
Authenticate signer:
Record timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
HIPAA Authorization pitfalls to avoid
Leaving the recipient or purpose blank can make the patient’s permission too unclear for the requested disclosure. Including more protected health information than necessary increases exposure if the completed authorization is misrouted or accessed improperly. Allowing broad staff access can weaken control over who prepares, sends, or retrieves a patient authorization. Using an expired authorization for a new disclosure can exceed the permission the patient actually granted.
Best practices for retaining HIPAA Authorization
Accurate fields, controlled access, an exported audit trail, and documented retention decisions make each HIPAA Authorization easier to review.
Apply the six-year HIPAA retention rule
Export the signed record and audit trail
Archive authorization records with restricted access
Verify scope before releasing protected information
HIPAA Authorization retention schedule
Retain HIPAA Authorization records according to the federal HIPAA Privacy Rule and check whether state law or organizational policy requires longer preservation.
6 years for authorization records
6 years from creation or effective date
6 years for related documentation
Longer state period if required
Retain accessible reproducible copies
Check exclusions before relying on electronic signing
Verify state rule
Not covered by ESIGN
Use applicable state process
Not this authorization form
HIPAA Authorization troubleshooting
Resolve field, signing, BAA, audit-trail, and retention questions before using a completed HIPAA Authorization to disclose protected health information.
Yes, when the workflow establishes signer intent, consent, attribution, and a reproducible retained record. ESIGN and applicable state electronic-transactions law support electronic signatures, while HIPAA still governs the authorization’s required content and disclosure purpose.
A signNow HIPAA workflow requires a Business Associate Agreement when signNow handles protected health information for a covered entity. The BAA addresses the platform relationship; it does not replace the authorization’s required scope, recipient, purpose, or expiration.
Upload the HIPAA Authorization PDF, let signNow detect fillable fields when available, or place fields manually. Confirm patient, representative, recipient, purpose, expiration, and signature fields before sending the document for completion.
The Business plan is listed at $8/user/month when billed annually and includes audit trails, templates, and mobile apps. Confirm the HIPAA BAA and any required compliance add-ons before processing protected health information.
Use signNow’s Audit Trail to review signer activity, timestamps, IP details, and the document’s event history. Export the completed authorization and audit evidence together so the disclosure decision remains reviewable.
HIPAA requires records to be retained for six years from creation or the last effective date under 45 CFR §164.530(j). Keep the signed authorization and related audit evidence accessible, reproducible, and protected from unauthorized access.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.