Service Consent
Automate complex legal workflows with a Service Consent 2007 template.
What Service Consent means
Service Consent is a record showing that a person agreed to a stated service, transaction, or electronic process. The document normally identifies the consenting party, explains what is accepted, and records a signature or affirmative action. With signNow, upload the Service Consent file, let the platform detect fillable fields, place signature and date fields, send it to the intended signer, and store the completed document with an audit trail. ESIGN and UETA can recognize the resulting electronic signature when intent, consent, attribution, and record retention requirements are satisfied.
Who uses Service Consent
Healthcare providers
Healthcare providers use Service Consent for patient acknowledgments and treatment-related approvals, keeping signer identity, consent language, and completion evidence together. If protected health information is involved, apply HIPAA safeguards and confirm whether a business associate agreement is required. signNow supports HIPAA-compliant workflows when the required agreement is in place.
Business teams
Legal, financial, construction, and service businesses use Service Consent for client approvals, contracts, invoices, and permission records. Teams can upload the specific document, place required fields, route it to named signers, and preserve the completed record with its audit trail for later review.
Legal standing and evidence
Service Consent can support a U.S. business transaction when the signer intends to sign, consents to electronic records, can be identified, and the completed record remains reproducible. ESIGN and UETA recognize qualifying electronic signatures, while wills, codicils, testamentary trusts, and certain court filings remain excluded under federal law.

How Service Consent works
The signNow workflow connects the Service Consent document, signer, electronic action, and retained evidence in four traceable stages.
Upload: Upload the Service Consent file. Prepare: Auto-detect and review consent fields. Route: Send to the named signer. Archive: Store the signed record with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete Service Consent
Prepare Service Consent in signNow by uploading the document, checking its fields, routing it to the signer, and preserving completion evidence.
Upload document:
Upload the Service Consent document to signNow. Check fields:
Review detected fields and add missing signature, date, or consent fields. Add signer:
Enter the intended signer’s email address. Send and track:
Send the document and monitor completion in the audit trail.
Recommended Service Consent setup
Configure Service Consent around signer attribution, reproducible records, controlled access, and the retention rule governing the underlying transaction.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with recorded intent |
| Audit trail | Enable completion certificate and activity history |
| Document retention | 6 years for HIPAA records under 45 CFR §164.530(j) |
| Encryption and provisioning | AES-256 storage with role-based user access |
Find and fill out the correct service consent form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
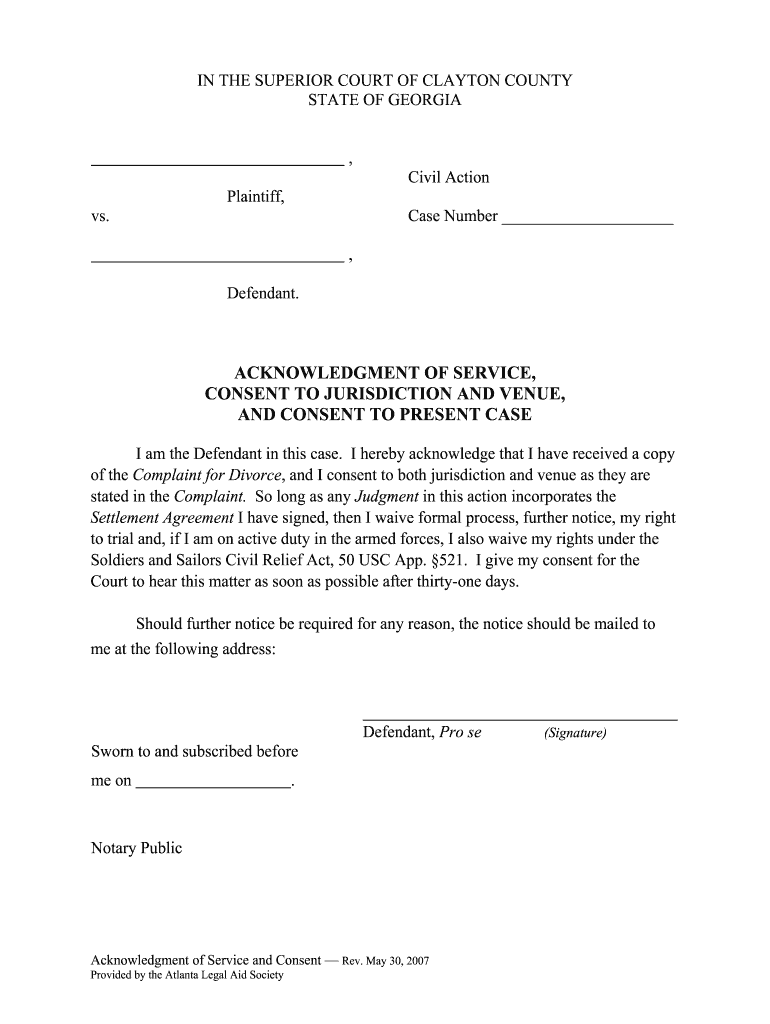
| *2007 GA Acknowledgement of Service and Consent [2007-05-30] 2007 | 4.8 Satisfied (2404 Votes) |
Signer authentication and security
PKI support:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit trails:
Inside the Service Consent audit trail
The audit trail records evidence around the Service Consent event, separate from preparing fields or configuring the document workflow.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Export evidence:
Service Consent retention schedule
Keep Service Consent for the period required by the record’s underlying business, tax, healthcare, or employment rule.
3 years: federal tax records
6 years: tax understatement
6 years: HIPAA records
3 years: payroll records
30 years: exposure records
Retention and record-keeping practices
Preserve Service Consent with its evidence of intent, identity, delivery, and completion, applying the rule that matches the underlying transaction.
Set a documented retention rule
Export the audit trail
Restrict access to records
Verify reproducibility and consent
Privacy and disclosure pitfalls
Placing full patient or client details in a broadly shared Service Consent exposes personal data beyond the people who need access. Skipping the electronic-record disclosure can weaken consumer consent when Service Consent is used in a covered consumer transaction. Sending Service Consent from a shared account makes signer attribution and responsibility harder to establish during a dispute. Failing to preserve the signed document and audit trail can impair proof that consent was given and the record was unchanged.
Service Consent troubleshooting
Use these answers to resolve field, signer, disclosure, plan, privacy, and enforceability questions before completing Service Consent.
Upload the original Service Consent PDF and confirm that detected fields match the document. signNow Business includes templates and audit trails; manually review field placement before sending so consent language is not covered or omitted.
A signer can often complete Service Consent without a signNow account through the email invitation or signing link. If stronger attribution is required, configure SMS OTP or advanced signer authentication available through applicable signNow plans.
For consumer-facing Service Consent, provide the electronic-record disclosure required by 15 U.S.C. §7001(c). Explain paper-record rights, electronic access, and withdrawal procedures before asking for consent; signNow records the transaction but does not replace the required disclosure.
signNow Business is listed at $8 per user per month with annual billing and includes legally binding eSignatures, templates, and audit trails. The Business plan includes 100 signature invites per user per year, with overage fees applying afterward.
If Service Consent includes protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm the BAA and configure access controls before sending patient-related consent documents.
ESIGN and UETA recognize electronic signatures when intent, electronic consent, attribution, and reproducible records are established. They do not remove exclusions for wills, codicils, testamentary trusts, or certain court orders and official filings.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.