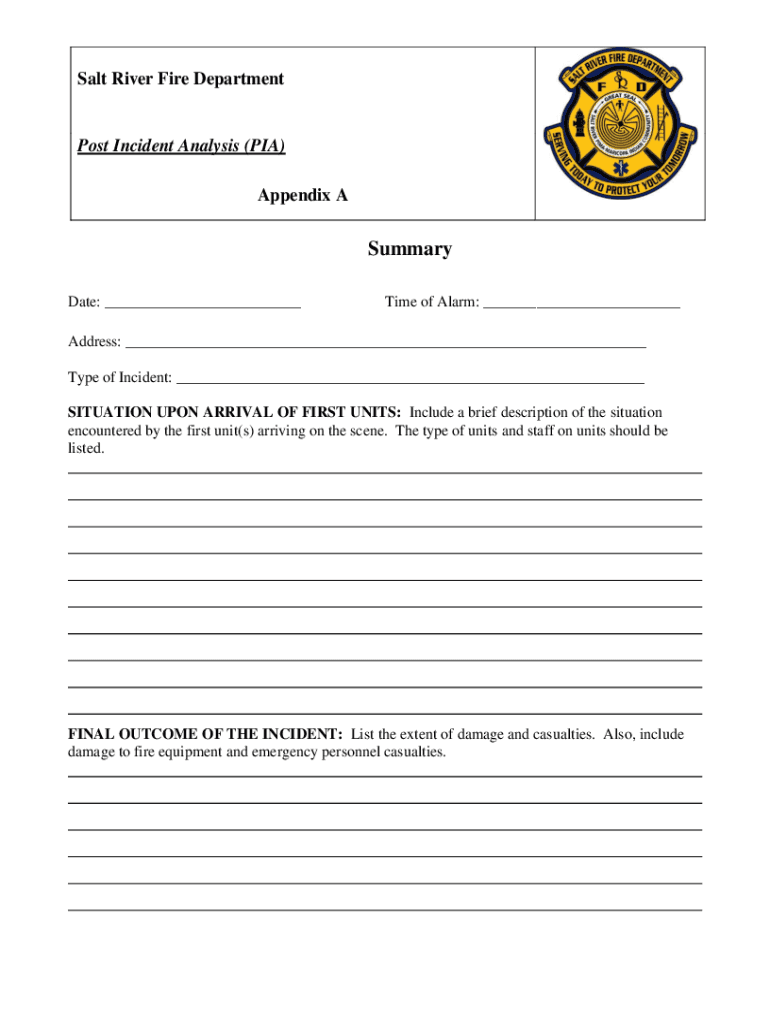
Post Incident Analysis (2000 2026)
Use a Post Incident Analysis Template 2000 template to make your document workflow more streamlined.
What Post Incident Analysis covers
Post Incident Analysis is a business record used to document what happened after an incident, why it occurred, and which corrective actions follow. It normally captures the incident date, affected process, factual findings, contributing causes, assigned owners, target dates, approvals, and follow-up evidence. The 2000–2026 reference identifies the period covered by the analysis rather than a federal filing form or issuing agency. In the United States, electronic execution can be supported by ESIGN and applicable state law when intent, consent, attribution, and record retention are demonstrated.
Who uses this incident analysis
Operations teams
Operations, compliance, and quality teams use the analysis to document incident facts, assign corrective actions, and obtain accountable approvals without circulating paper copies.
Industry teams
Healthcare, financial, legal, construction, and technology organizations adapt the template to their own incident procedures and evidence requirements.
Complete Post Incident Analysis in signNow
Upload the Post Incident Analysis template, verify fields, route responsibilities, collect signatures, and preserve the completed record.
Upload template:
Upload the Post Incident Analysis template to signNow. Check fields:
Review detected fields and add missing dates or initials. Assign reviewers:
Assign each analysis section to the responsible reviewer. Send for signing:
Send the completed analysis for electronic signatures. Archive record:
Store the signed document with its audit trail.
How the Post Incident Analysis audit trail works
The audit trail records the signing events that establish who handled the Post Incident Analysis, when actions occurred, and how the final record was completed.
Signer authentication:
Timestamp capture:
Document integrity:
Tamper evidence:
Completion certificate:
Audit export:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Platform requirements for incident analysis
Complete Post Incident Analysis in signNow through Chrome, Edge, or Safari on supported Windows, macOS, iOS, and Android devices. The signNow mobile apps support document review and signing, while camera capture can help digitize paper evidence before attaching it to the analysis.
Desktop browsers Chrome and Edge on Windows 10 or later Apple devices Safari on macOS and iOS Android app Android app with camera capture
Teams should manage signNow access through approved devices and identity controls. Confirm that incident evidence can be uploaded, viewed, and exported under organizational policy, especially when records include protected health information, confidential investigations, or other restricted data.
Features for Post Incident Analysis workflows
signNow organizes the Post Incident Analysis from template preparation through approval, signature collection, audit evidence, and controlled record storage.
Template preparation
Upload the Post Incident Analysis template and prepare its incident details, findings, owners, and approvals in one controlled document.
Role assignment
Assign fields and signing responsibilities so each reviewer receives only the information and action required for their role.
Electronic routing
Send the analysis through signNow and monitor completion without manually tracking email attachments or paper copies.
Audit trail
Capture signer actions, timestamps, and completion evidence in an audit trail connected to the final analysis.
Mobile access
Use signNow mobile apps to review or sign the analysis when incident response occurs away from the office.
Record preservation
Store the completed analysis and certificate of completion for controlled retrieval during reviews, audits, or corrective-action follow-up.
Find and fill out the correct post incident analysis form example
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2000 Post Incident Analysis (PIA) [2000-12] 2000 | 4.8 Satisfied (5882 Votes) |



Security for incident records
Encryption:
Security certification:
Information security:
Health data:
Electronic signatures:
Privacy controls:
Record-keeping practices for incident analysis
Preserve the analysis, evidence, approvals, and signing history under a documented retention and access policy.
Preserve the complete incident record
Export the audit trail
Apply the governing retention rule
Secure and review archived files
Retention periods for related records
Post Incident Analysis has no universal federal retention period; apply the rule governing the records and evidence attached to it.
Internal policy schedule
Six years for HIPAA records
Three years for tax records
Seven years for audit records
Thirty years for exposure records
Legal standing of Post Incident Analysis
A signed Post Incident Analysis can support business evidence when the signer shows intent, consents to electronic records, can be identified, and the record remains accurate and reproducible. ESIGN, 15 U.S.C. chapter 96, and applicable UETA or New York ESRA rules provide the framework; wills, court orders, family-law decrees, and other statutory exceptions remain outside that framework.

Post Incident Analysis troubleshooting
Resolve routing, compliance, field, and retention questions before treating a Post Incident Analysis as complete.
Business includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, SOC 2, and GDPR support at $8 per user monthly when billed annually. It includes 100 signature invites per user per year; overage fees may apply.
Yes. Business Premium is $15 per user monthly when billed annually and adds bulk send, kiosk mode, request payments, and quick invite links. Use bulk send only when separate Post Incident Analysis records require the same routing structure.
A HIPAA workflow requires signNow’s HIPAA compliance configuration and a business associate agreement. The Post Incident Analysis should contain only necessary protected health information, with access limited to authorized personnel and retention governed by 45 CFR 164.530(j).
signNow supports ESIGN and UETA compliance, but the laws do not make every document electronically signable. Wills, court orders, family-law decrees, and other statutory exceptions require separate legal procedures and should not be routed as ordinary e-signature records.
Verify the template after upload: compare incident dates, factual findings, corrective-action owners, due dates, and approval fields against the source document. Auto-detected fields reduce setup work, but the sender remains responsible for accuracy before sending.
Export the completed Post Incident Analysis and its audit trail from signNow, then store both under the applicable organizational or legal retention schedule. For HIPAA records, retain six years from creation or the last effective date under 45 CFR 164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.