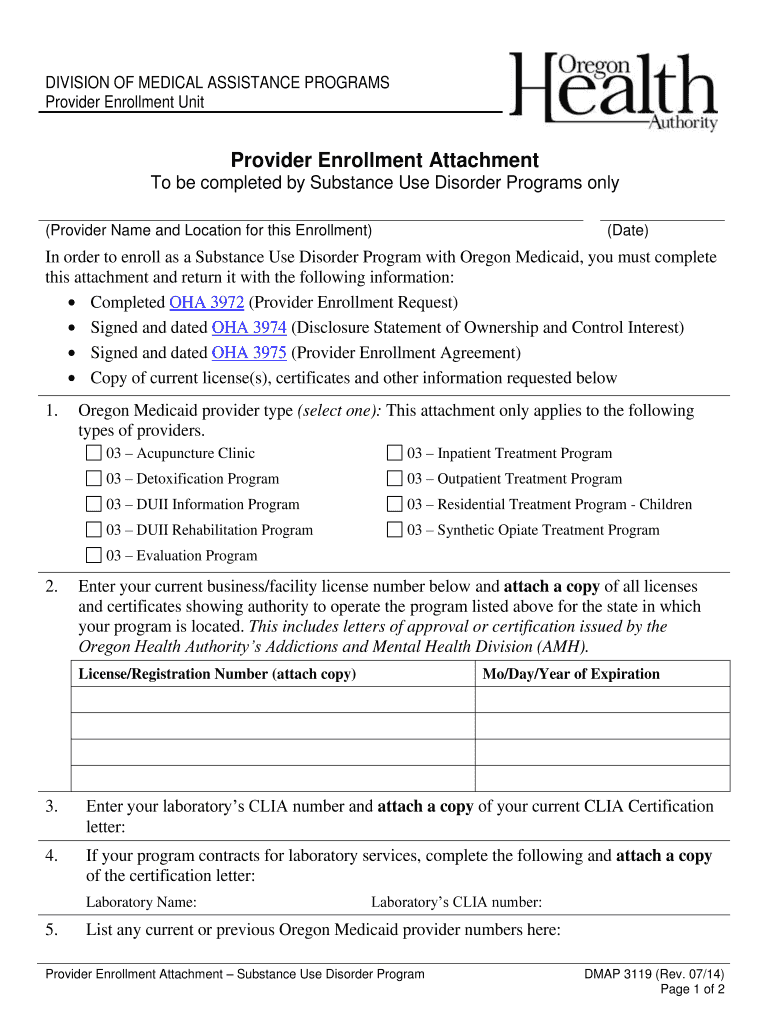
Dmap 3119 Enrollment Attachment For Chemical Dependency Providers Apps State Or
Get the DMAP 3119 Enrollment Attachment For Chemical Dependency Providers Apps State Or 2014 template, fill it out, eSign it, and share it in minutes.
About the Dmap 3119 attachment
The Dmap 3119 Enrollment Attachment For Chemical Dependency Providers Apps State Or is a provider-application attachment used in a chemical dependency services enrollment workflow. Because the supplied form record does not identify its issuing agency, field list, filing deadline, or state-specific submission rule, verify those details on the official application instructions before signing. signNow can upload the attachment, detect or add fillable fields, route it to the provider and authorized reviewer, capture electronic signatures, and preserve the completed document with an Audit Trail.
Who uses this enrollment attachment
Treatment providers
Chemical dependency providers use this attachment to organize application information, authorization details, and supporting records before review. Administrative staff can complete identified fields, route the document to an authorized signer, and preserve the finished attachment with related application materials. HIPAA safeguards apply when the attachment contains protected health information.
State programs
State-facing behavioral-health organizations can use signNow to prepare the attachment, collect required signatures, and maintain a reproducible electronic record. The workflow helps separate preparation from approval, while access controls and audit trails document who handled the application and when.
How signNow handles the attachment
The Dmap 3119 workflow moves from document preparation to authenticated signing and controlled record storage without changing the attachment’s substantive application information.
Upload attachment: Upload the Dmap 3119 attachment as a PDF or supported document. Prepare fields: Review detected fields and add missing text, date, initials, or signature fields. Assign recipients: Assign the provider and reviewing organization to the required fields. Complete and store: Send the attachment, collect signatures, and preserve the completed record with its Audit Trail.
Complete the attachment in signNow
Use this sequence to prepare, route, sign, and preserve the Dmap 3119 Enrollment Attachment For Chemical Dependency Providers Apps State Or.
Upload:
Upload the completed attachment template. Prepare:
Review and place required fields. Route:
Assign the provider and reviewer. Send:
Send the signing request. Archive:
Download the signed record and Audit Trail.
Choose the right way to sign
- Use the signNow web app when administrators need to upload the Dmap 3119 attachment, place fields, assign recipients, and monitor completion from a managed desktop workflow.
- Use the signNow mobile app when authorized staff review or sign the attachment from an iOS or Android device while working away from the office.
- Use kiosk mode for an in-person intake desk where a provider completes the Dmap 3119 attachment on a controlled device without managing an individual account.
- Create a shareable signing link when a department repeatedly collects the same attachment from eligible providers and needs a controlled distribution method.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended attachment workflow setup
Configure the Dmap 3119 workflow around authenticated recipients, preserved signing evidence, and healthcare record safeguards.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with completion evidence |
| Audit trail | Enable and export with signed PDF |
| Document retention | Six years for PHI under 45 CFR §164.530(j) |
| Encryption | TLS in transit and AES-256 at rest |
What the signing record captures
The signNow Audit Trail records the events surrounding this attachment’s electronic signing, helping administrators demonstrate who acted, when, and which completed document was preserved.
Authenticate signer:
Capture timestamps:
Track document identity:
Seal completion:
Review events:
Export evidence:
Find and fill out the correct dmap 3119 enrollment attachment for chemical dependency providers apps state or
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2014 OR DMAP 3119 [2014-07] 2014 | 4.8 Satisfied (7864 Votes) |
Retention periods to verify
Use the six-year HIPAA period when this attachment contains protected health information, then check state behavioral-health and program-specific rules for longer requirements.
Six years: PHI records
Three years: IRS records
Three years after hire: I-9
Three years: payroll records
State-specific period: verify rule
Challenges when completing the attachment
Application staff may complete provider identifiers or program information inconsistently, creating mismatches between the attachment and the main enrollment application. Multiple reviewers can overwrite fields or signatures when the Dmap 3119 attachment lacks clearly assigned roles and signing order. Protected health information may be copied into email threads or shared folders without the access controls required for the organization’s HIPAA workflow. A completed attachment without its certificate of completion or Audit Trail may provide weaker evidence about signer identity, timing, and document integrity.
Security controls for PHI
Healthcare compliance:
Independent controls:
Security management:
Encryption at rest:
Transport security:
Signer verification:
Who benefits from this workflow
The attachment is most useful where provider applications require repeatable review, authorized signatures, and controlled records containing healthcare information.
A solo chemical dependency provider can complete the attachment from a mobile device, sign electronically, and return the finished record without arranging an office appointment. A behavioral-health clinic can route provider attachments through administrative review, authorized signature, and secure archival while limiting access to protected health information. A state-contracted treatment network can standardize the attachment across locations with reusable templates, delegated sending, and Audit Trails for application oversight.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.



Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting the Dmap 3119 workflow
Use these answers to resolve field, authentication, privacy, retention, and enforceability questions before submitting the completed attachment.
The Dmap 3119 attachment contains protected health information, so configure signNow for the organization’s HIPAA workflow and obtain the required Business Associate Agreement. HIPAA compliance does not replace the provider’s duties to limit access, use appropriate permissions, and follow its own privacy and security policies.
A signNow Business plan includes legally binding eSignatures and Audit Trails, while HIPAA compliance requires the appropriate arrangement and configuration. Confirm plan capabilities and contractual terms before routing protected health information through the workflow.
Review the uploaded PDF before sending. signNow can detect fillable fields, but staff should verify every detected field against the actual Dmap 3119 attachment and add missing signature, date, or provider-information fields manually.
Use signNow’s recipient roles and field assignments to separate provider completion from organizational approval. A recipient should not be asked to sign fields intended for another party, because incorrect attribution can complicate application review.
Export both the signed attachment and its Audit Trail after completion. The audit record supports evidence of delivery, signer actions, timestamps, and completion; retain it with the attachment under the organization’s HIPAA and state-program records policy.
Electronic signatures generally receive legal recognition under ESIGN, 15 U.S.C. chapter 96, and applicable UETA provisions when intent, consent, attribution, and record reproduction are established. Confirm any state-program rule requiring notarization, wet ink, or a specific submission method.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.