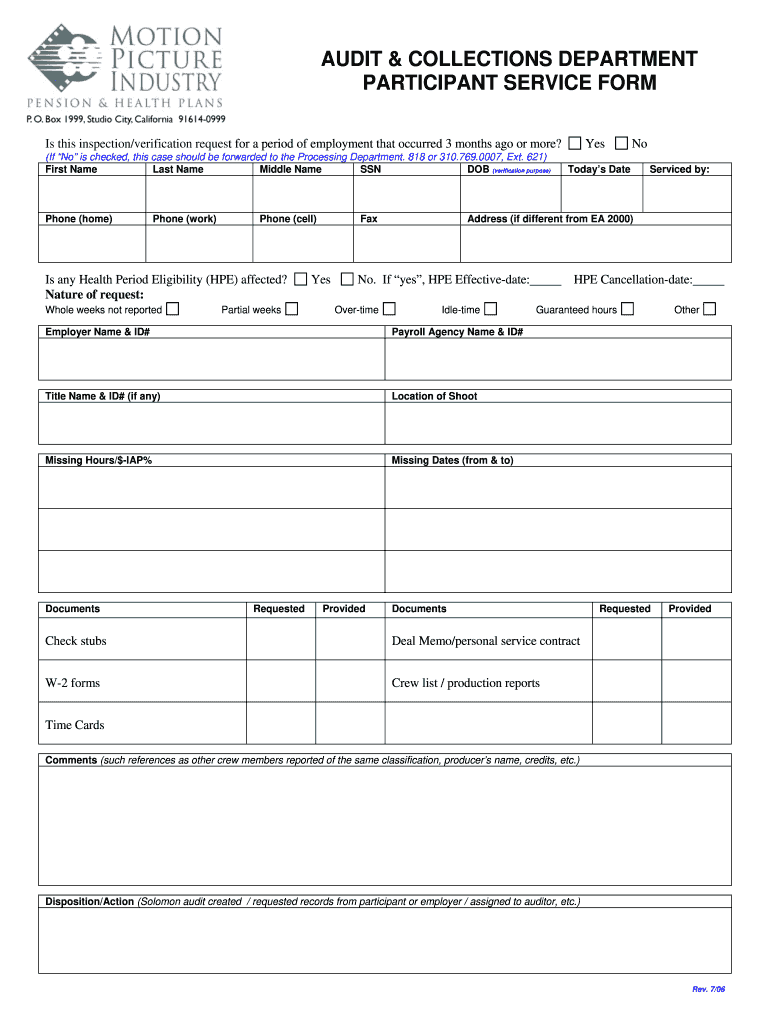
MPIPHP
Create a custom Mpiphp 2006 that meets your industry’s specifications.
What MPIPHP is and how it works
MPIPHP is a form document that can be prepared, routed, signed, and retained electronically when its issuing or receiving organization permits electronic processing. With signNow, upload the MPIPHP file, review detected fillable fields, add signer information, and send the document for completion. Signers review the assigned fields and apply an electronic signature. signNow then provides the completed document and audit trail. Confirm the form’s official instructions, required attachments, filing method, and deadline before relying on an electronic workflow.
How MPIPHP works in signNow
The MPIPHP workflow moves from source document to verified fields, assigned signers, completed signatures, and preserved evidence.
Upload: Upload the MPIPHP source document. Review: Review detected fields and required entries. Route: Send MPIPHP to assigned signers. Preserve: Store the signed record and audit trail.
How to complete MPIPHP in signNow
Follow the MPIPHP workflow from source-file upload through signer routing, completion, and evidence preservation.
Add the source file:
Upload MPIPHP Check every field:
Review detected fields Set roles and order:
Assign signers Route the document:
Send for signature Save the signed file:
Export records
What the MPIPHP audit trail records
The audit trail connects MPIPHP’s signer activity, timestamps, document history, and exported completion evidence.
Authenticate signer:
Timestamp activity:
Link document:
Seal history:
Log actions:
Retrieve evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended MPIPHP workflow setup
Configure MPIPHP around signer identity, documented intent, secure transmission, and the retention rule governing the underlying record.
| MPIPHP setting | Recommended configuration |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Retain completion certificate and event history |
| Document retention | Follow the underlying record rule |
| Encryption | TLS 1.2 or 1.3 and AES-256 protection |
MPIPHP processing and completion stages
Use this sequence to prepare, route, sign, and preserve an MPIPHP record through signNow.
Prepare the document
Deliver to signers
Complete signer review
Archive completed records
Find and fill out the correct audit amp collections department participant service form mpiphporg
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2006 Motion Picture Industry Participant Service Form [2006-07] 2006 | 4.8 Satisfied (7339 Votes) |
Security controls for MPIPHP records
Transport encryption:
Stored encryption:
Security certification:
Management standard:
Health information:
Electronic signatures:
Best practices for completing MPIPHP
Accurate field review, controlled routing, and complete record preservation reduce avoidable problems when MPIPHP is completed electronically.
Verify every MPIPHP field
Confirm signer responsibilities before sending
Preserve the completion evidence
Apply the governing retention rule
Key signNow features for MPIPHP
signNow combines document preparation, signer routing, audit evidence, security controls, and integrations for organizations processing MPIPHP electronically.
Field detection
Upload MPIPHP, review detected fields, and prepare the document without rebuilding its existing layout. Field review keeps the electronic copy aligned with the source file before signer routing.
Signer routing
Assign MPIPHP fields to named recipients and define the order in which they act. This reduces misrouted signatures and makes each signer’s responsibility visible before delivery.
Remote signing
Collect electronic signatures through a browser or mobile workflow while preserving the document’s completion history. The process supports remote review when the responsible organization permits electronic completion.
Audit evidence
Keep the signed MPIPHP document with its completion certificate and audit trail. The combined record helps demonstrate who acted, when the action occurred, and which version was completed.
Data protection
Protect MPIPHP data with TLS 1.2 or 1.3 in transit and AES-256 at rest. These controls address transmission and storage security for the electronic workflow.
System integration
Connect MPIPHP workflows with services such as Google Drive, Box, Microsoft 365, or NetSuite when the organization’s plan and process require integrated storage or business-system routing.



MPIPHP privacy and disclosure pitfalls
Personal information entered into MPIPHP can be exposed when recipients, permissions, or shared storage locations are configured incorrectly. Missing consent language can weaken the evidence supporting an electronic MPIPHP transaction, especially when a consumer receives the record. Assigning a signature field to the wrong recipient can leave MPIPHP incomplete or create uncertainty about signer attribution. Keeping the signed MPIPHP file without its audit trail can make later reconstruction of the signing event more difficult.
MPIPHP signing and troubleshooting questions
These answers address field detection, signer delivery, authentication, plan selection, electronic-signature validity, and retention issues for MPIPHP workflows.
Upload the official MPIPHP file again, then inspect detected fields before sending. signNow’s Business plan includes templates and audit trails; field detection does not determine whether a field is legally required, so compare the result with the source instructions.
Check the recipient address, signer order, and assigned fields before resending. A signer can often complete MPIPHP without creating an account, but the sender should verify identity controls and retain the resulting audit trail.
Use SMS OTP or another configured authentication control when the MPIPHP transaction requires stronger signer attribution. signNow supports authentication options, but the required method depends on the organization’s policy and the underlying record.
The Business plan is listed at $8 per user per month with annual billing. Business Premium adds bulk send and is listed at $15 per user per month annually; confirm plan limits before routing multiple MPIPHP records.
Electronic signatures generally require intent, consent, attribution, and a retained reproducible record under ESIGN and UETA. For consumer-facing MPIPHP transactions, review the electronic-record disclosure requirements in 15 U.S.C. §7001(c).
If MPIPHP contains protected health information, use a signNow workflow with the required BAA and apply HIPAA controls. HIPAA documentation retention is six years under 45 CFR 164.530(j), subject to applicable state rules.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.