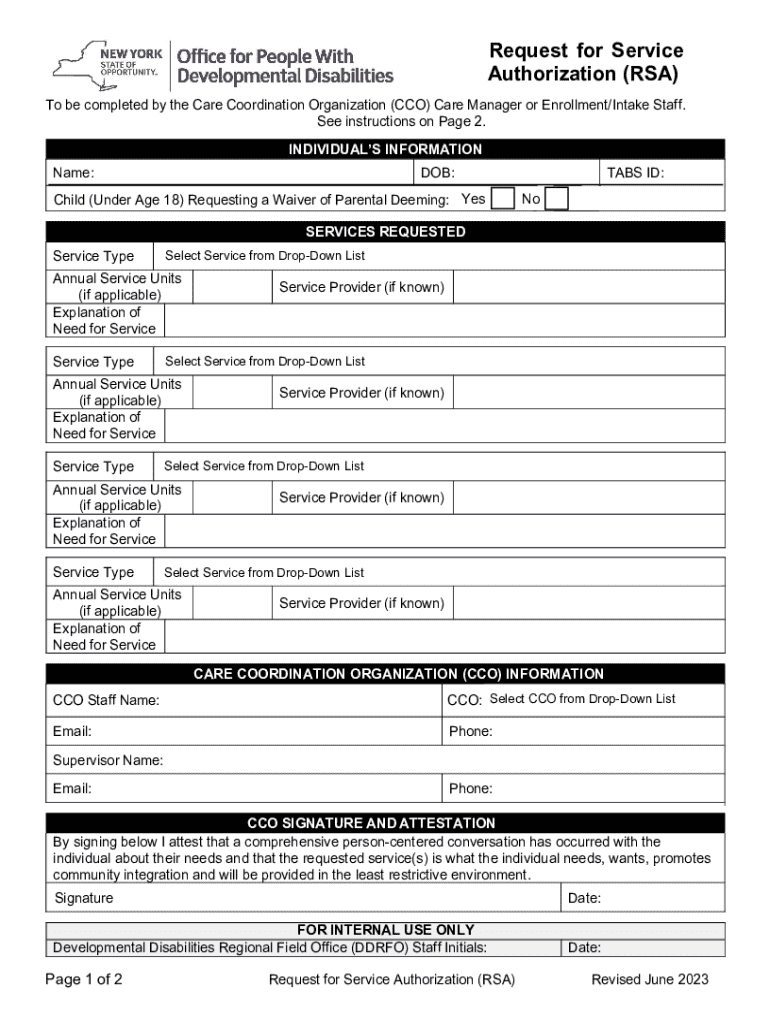
Request For Service Authorization Rsa To Be Comp
Use a Request For Service Authorization RSA To Be Comp 2023 template to make your document workflow more streamlined.
What this authorization form does
Request For Service Authorization Rsa To Be Comp is a document used to record a request for specified services and obtain the required authorization from a responsible signer. In signNow, the sender uploads the document, reviews or adds fillable fields, identifies the signer, and sends it electronically. The signer reviews the request, completes assigned fields, and applies an electronic signature. signNow records transaction activity in an audit trail and provides a completed copy for controlled storage. The form’s underlying organization, service, and retention requirements should be confirmed before use.
How the authorization workflow works
The workflow moves from document upload to field review, signer delivery, electronic completion, and audit-trail storage.
Upload: Upload the authorization document into the signNow editor. Prepare: Auto-detect fields, then correct or add required fields. Route: Send the request to the identified signer or signers. Finalize: Complete signatures and preserve the audit trail.
How to complete the authorization online
Use this sequence to prepare, route, sign, and preserve the Request For Service Authorization record in signNow.
Upload the form:
Upload the Request For Service Authorization document. Check the fields:
Review detected fields and add missing fields. Add the signers:
Enter signer details and configure signing order. Send for signature:
Send the authorization and monitor completion. Save the evidence:
Store the signed record and audit trail.
Features for completing the authorization
signNow combines field preparation, signer routing, electronic signatures, audit evidence, and record handling for the Request For Service Authorization workflow.
Field placement
Upload the Request For Service Authorization document and place required signer, date, and information fields before sending it for completion.
Signer routing
Route the authorization to named recipients by email, with signing order configured when multiple approvals are required.
Audit evidence
Capture timestamps, recipient actions, and completion history in an audit trail linked to the signed record.
Reusable template
Use reusable templates when the same authorization structure is sent repeatedly, reducing inconsistent field placement.
Mobile signing
Let recipients review and sign from supported desktop or mobile workflows without requiring paper handling.
Record control
Store the signed authorization and completion evidence in a controlled repository connected to the organization’s record policy.



 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Platform requirements for completing the form
Request For Service Authorization Rsa To Be Comp can be prepared in Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow also provides mobile apps for iOS and Android, with encrypted connections using TLS.
Supported browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile access iOS and Android mobile apps
Organizations should manage the devices used to access completed authorization records, restrict downloads, and apply account controls appropriate to the information collected. Teams using APIs, SSO provisioning, or regulated workflows should confirm the selected signNow plan and configuration before deployment.
Signer authentication and certificates
PKI certificates:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit trail:
Find and fill out the correct request for serviceauthorization rsato be comp
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| NY Request for Service Authorization (RSA) 2023 | 4.8 Satisfied (121 Votes) | |
| NY Request for Service Authorization (RSA) 2018 | 4.8 Satisfied (578 Votes) |
Recommended authorization workflow setup
Configure the Request For Service Authorization workflow around signer identity, evidence preservation, secure storage, and the retention rule governing the underlying service record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Legally binding eSignature |
| Audit trail | Export with certificate of completion |
| Document retention | Apply the governing record rule |
| Encryption | TLS 1.2/1.3 and AES-256 |
What the authorization audit trail records
The signNow audit trail links signer activity and document history to the completed Request For Service Authorization record.
Authenticate signer:
Capture timestamps:
Hash document:
Seal completion:
Record actions:
Export evidence:
Processing stages for the authorization
Processing depends on document readiness, recipient access, signer response, and the organization’s record-storage procedure.
Prepare the document
Deliver to signers
Complete signer review
Archive the completion record
Retention and record-keeping practices
Preserve the signed authorization, evidence of consent, and audit history under the retention rule that applies to its underlying service decision.
Set the retention period from applicable rules
Export the audit trail after signing
Restrict access to completed records
Document each record disposition
Privacy and disclosure checks
Personal information copied into the Request For Service Authorization may remain visible to recipients who do not need access. A signer may approve the request without a clearly recorded disclosure explaining electronic records and signature consequences. Shared links or broad folder permissions can expose the completed authorization and its audit history. Sending the authorization to an incorrect address can disclose requested services and related personal information.
Legal standing of electronic authorization records
For a U.S. business authorization, enforceability generally depends on intent to sign, consent to electronic records, attribution to the signer, and retention of a reproducible record under ESIGN and applicable UETA rules. Wills, certain court orders, family-law decrees, and other statutory exceptions remain outside that framework.

Troubleshooting authorization workflows
Resolve the specific upload, delivery, authentication, plan, privacy, and enforceability questions that can affect a completed Request For Service Authorization.
Upload the original Request For Service Authorization file again and check whether the PDF is password-protected, image-only, or damaged. signNow can place fields after upload, but an unreadable source may require a clean PDF or manual field placement before sending.
Open the recipient settings and confirm the signer’s email address, role, and signing order. Resend the invitation from the transaction record rather than creating a second request, preserving the original audit trail and avoiding duplicate authorizations.
If the signer cannot open the authorization, verify the email link, browser, and network connection. A sender can add SMS authentication when the selected signNow configuration supports it, then issue a fresh invitation after confirming the phone number.
Business includes legally binding eSignatures, audit trails, templates, and mobile apps at $8 per user per month when billed annually. It includes 100 signature invites per user per year, with overage fees, so review usage before sending high volumes.
For health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm that a BAA is in place before placing protected health information in this authorization workflow; the platform alone does not determine whether the process meets every HIPAA obligation.
An electronic authorization is not automatically enforceable merely because it has a signature image. Under ESIGN and applicable UETA rules, preserve intent, electronic consent, signer attribution, and a reproducible record; consumer transactions also require the disclosure described in 15 U.S.C. §7001(c).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.