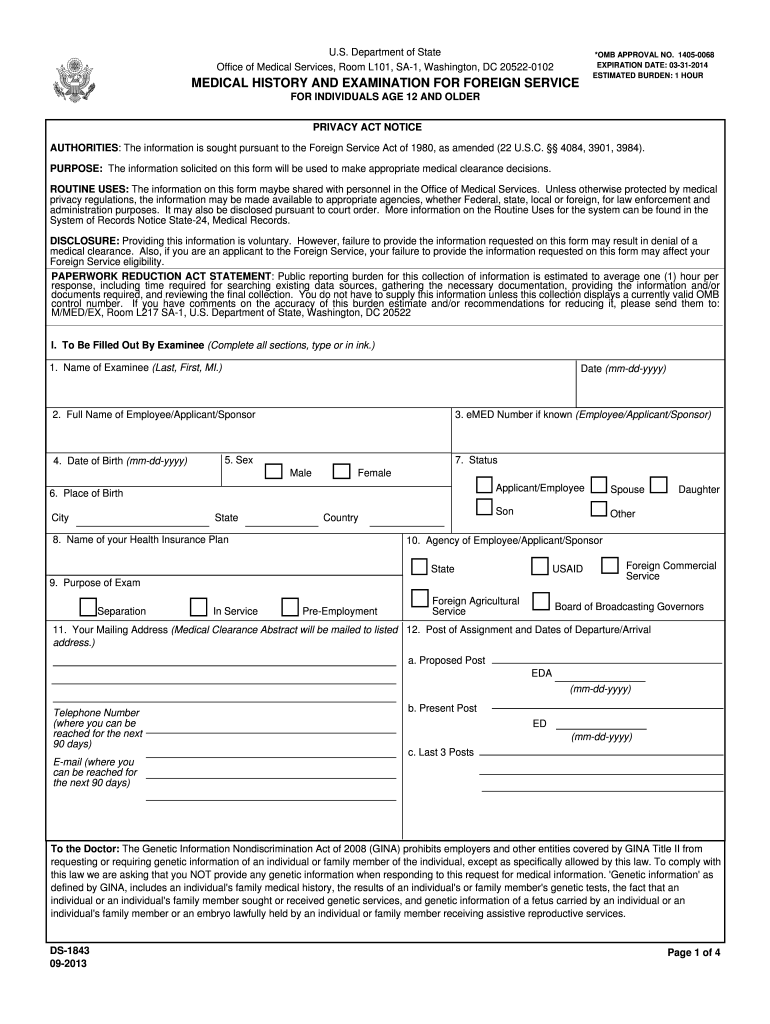
Verify Post Healthmedical Information US Department Of State
Use a Verify Post HealthMedical Information US Department Of State 2013 template to make your document workflow more streamlined.
What this Department of State form does
Verify Post Healthmedical Information US Department Of State is an electronic record used to verify health-related information for a Department of State process. The supplied form name does not identify an official form number, field list, filing deadline, or issuing-office instruction. In signNow, a sender uploads the source document, reviews detected fields, assigns signer and recipient roles, sends the verification record, and preserves the completed PDF with its certificate and audit trail. Confirm the agency’s current instructions before relying on electronic completion or submission.
Legal standing of this verification record
A completed electronic verification record can support U.S. business evidence when the signer demonstrates intent, consents to electronic records, can be attributed to the signature, and the record remains reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA law. Wills, codicils, testamentary trusts, certain court orders, and family-law decrees remain excluded.

Who uses this verification form
Government health teams
Government-facing health-information teams can use the document to collect a reviewable record before a Department of State process. They should confirm the required fields, recipient, consent language, and submission channel with the responsible agency office before sending.
Healthcare organizations
Healthcare organizations can prepare a controlled verification packet when a patient’s health information is requested for a government-related purpose. Role-based access, minimum-necessary disclosure, HIPAA analysis, and a preserved audit trail should govern every signer and recipient.
Features that support this verification workflow
signNow organizes the source document, signer actions, completion certificate, and controlled storage around the Department of State health-information verification process.
Document preparation
Upload the Department of State verification source and place required signer, date, and acknowledgment fields without recreating the document manually.
Field detection
Auto-detected fields help identify areas requiring review before the verification record is sent to its assigned signer.
Role assignment
Assign the responsible healthcare or government-facing participant and control the recipient sequence for the verification workflow.
Audit evidence
Capture the completed PDF, signer actions, timestamps, and certificate in one retrievable record for internal review.
Mobile signing
Use mobile apps when an authorized signer reviews or completes the health-information verification away from a desktop.
Connected storage
Connect approved records to Google Drive, Box, Egnyte, or AWS for controlled document storage and retrieval.
Complete this form in signNow
Use the source document and current Department of State instructions to prepare each verification field before requesting an electronic signature.
Upload document:
Upload the source verification document. Check fields:
Review detected fields and required health-information entries. Assign roles:
Assign signers and recipients by role. Send securely:
Send through the approved signing channel. Store records:
Download the completed PDF and certificate.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended workflow configuration
Configure the verification workflow around signer attribution, protected health information, reproducible records, and the Department of State’s current submission requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP when required |
| Signature type | Electronic signature with signer intent |
| Audit trail | Export certificate and action history |
| Document retention | Six years when HIPAA applies |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
Audit trail for the completed verification
The audit trail records the evidence surrounding this health-information verification, rather than merely documenting account setup or document upload.
Authenticate signer:
Capture timestamp:
Link document:
Seal evidence:
Export certificate:
Archive securely:
Security controls for this record
Transport encryption:
Stored-data encryption:
Control reporting:
Security certification:
Health-information compliance:
Electronic-signature law:
Find and fill out the correct verify post healthmedical information us department of state
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| DS-1843 2017 | 4.8 Satisfied (3043 Votes) | |
| DS-1843 2013 | 4.7 Satisfied (1121 Votes) |
Platform requirements for completion
Complete this verification record through Chrome, Firefox, Safari, or Edge on Windows 10, Windows 11, or macOS; signNow also provides iOS and Android mobile apps. Use TLS-protected connectivity.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows 10, Windows 11, macOS Mobile access iOS and Android mobile apps
Organizations handling health-related information should manage Windows, macOS, iOS, and Android devices through approved policies. Configure signNow access, API permissions, SSO provisioning, and retention controls according to the organization’s privacy program and the Department of State’s current submission instructions.



Retention schedule by record class
Choose the record class that actually applies; state, contractual, legal-hold, or agency rules may require longer preservation.
Six years: health records
Three years: tax records
Three years: employment records
Six years: broker records
Thirty years: exposure records
Record-keeping practices for this form
Preserve the completed verification record, its audit evidence, and access history according to the applicable health-information and organizational retention rules.
Apply the correct retention rule
Export every audit trail
Protect sensitive health information
Assign archival ownership
Privacy and disclosure pitfalls
Including a patient identifier or health detail not required for Department of State verification can expose protected information beyond the intended purpose. Skipping an electronic-record consent disclosure may weaken the record when a consumer must receive or sign health-related information electronically. Allowing shared administrator credentials makes it difficult to attribute edits, downloads, or signer-invitation changes to a specific person. Sending the completed verification record to an unintended recipient can create an unauthorized disclosure and trigger internal incident-response obligations.
Document exclusions and state rules
Excluded wills
Court orders
Family law
State notarization
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting this verification workflow
Resolve field, consent, plan, access, and submission questions before treating the completed record as ready for agency use.
The supplied form name does not include an official form number or agency field instructions. Upload the source document, compare every detected field with the Department of State version, and obtain agency confirmation before sending it for signature.
For health-related consumer records, ESIGN’s consumer-disclosure rule, 15 U.S.C. §7001(c), requires notice of the right to paper records, electronic access, and consent withdrawal procedures. Configure and retain that disclosure where the transaction is consumer-facing.
signNow lists HIPAA compliance as requiring a BAA. Execute the appropriate BAA before using the workflow for protected health information, then limit access and confirm the Department of State’s accepted transmission method.
The Business plan is listed at $8 per user monthly with annual billing and includes audit trails and templates. Business Premium is listed at $15 and adds bulk send and kiosk mode; choose based on the workflow’s actual volume.
A signer can receive the request through signNow and complete it from a supported browser or mobile app. If identity assurance beyond email is required, use the organization’s approved authentication controls and document that decision.
An electronic signature is not automatically sufficient for every agency process. ESIGN and UETA address electronic-signature validity, but the Department of State’s current instructions control submission, required identity proofing, and any wet-ink or in-person exception.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.