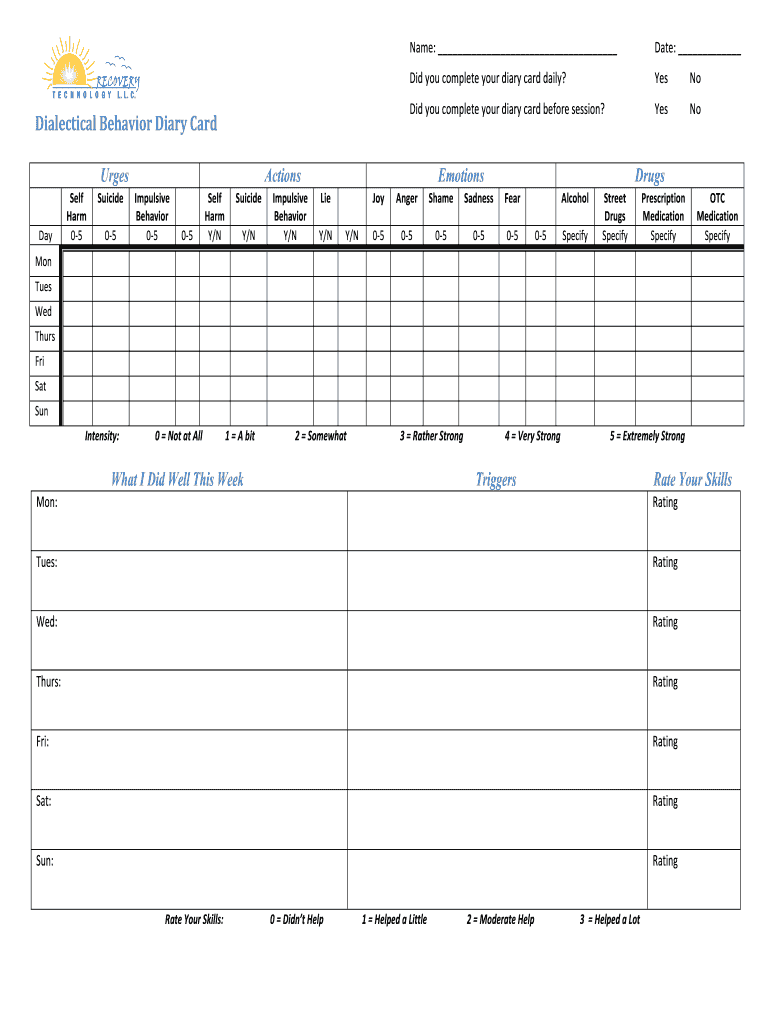
Dbt Diary Card Recovery Technology Recoverytechnology
Use a DBT DIARY CARD Recovery Technology Recoverytechnology 2012 template to make your document workflow more streamlined.
What this diary card technology does
The Dbt Diary Card Recovery Technology Recoverytechnology is a structured electronic diary card for recording information used in behavioral-health recovery workflows. Because the supplied form name does not identify an issuing agency, official fields, filing deadline, or required reporting threshold, those details cannot be stated reliably here. In signNow, a sender uploads the document, reviews automatically detected fillable fields, adds participant and clinician signature fields, sends the card for completion, and stores the signed copy with an audit trail. Organizations must separately confirm clinical, privacy, and state-law requirements before use.
Who uses the diary card recovery technology
Behavioral health
Behavioral-health practices can use the Dbt Diary Card Recovery Technology Recoverytechnology for structured patient diary entries, treatment-session preparation, consent records, and clinician review. The document should identify the participant, preserve the relevant reporting period, and limit access to authorized care-team members. signNow can route the completed card for electronic signatures and retain its audit history.
Care teams
Therapists, patients, and care coordinators can complete the Dbt Diary Card Recovery Technology Recoverytechnology remotely when the workflow permits electronic records. Organizations handling protected health information should evaluate HIPAA obligations, execute a business associate agreement where required, and configure authentication, permissions, and retention policies appropriate to the record.
Recommended diary-card workflow setup
Configure the diary-card workflow around signer identity, documented consent, audit evidence, protected information, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with documented intent |
| Audit trail | Certificate and completed action history |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 |
Complete the diary card in signNow
Use this signNow sequence for the Dbt Diary Card Recovery Technology Recoverytechnology, then confirm clinical and privacy requirements before collecting sensitive information.
Upload the card:
Upload document Check field placement:
Review detected fields Assign signers:
Add participants Deliver securely:
Send for signing Save audit trail:
Store evidence
How the diary card audit trail works
The audit trail records identity, timing, document history, signing actions, and completion evidence for this specific diary card.
Authenticate signer:
Capture timestamps:
Track document version:
Log signer actions:
Seal completion:
Export audit trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Choose a signing method for the diary card
- Upload the Dbt Diary Card Recovery Technology Recoverytechnology in the signNow web app when preparing a controlled template or one-time participant packet.
- Use the signNow mobile app when a participant or clinician needs to review and sign the diary card from an iOS or Android device.
- Use kiosk mode for supervised, on-site completion when several participants use an organization-managed device and each signing session must remain separated.
- Create a shareable signing link when the same diary-card template must be distributed through an approved portal or controlled communication channel.



Find and fill out the correct dbt diary card recovery technology recoverytechnology
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| 2012 Recovery Technology DBT Diary Card [2012-07-30] 2018 | 4.8 Satisfied (4851 Votes) | |
| 2012 Recovery Technology DBT Diary Card [2012-07-30] 2012 | 4.7 Satisfied (202 Votes) |
Security controls for diary cards
Data in transit:
Data at rest:
Security certification:
Information security:
Health information:
Electronic signatures:
Platform requirements for diary cards
Complete the Dbt Diary Card Recovery Technology Recoverytechnology in a current Chrome, Firefox, Safari, or Edge browser on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing authorized participants to review and sign from supported mobile devices. Use TLS-protected connections when transmitting the document.
Browsers Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, and Android Devices Desktop and mobile web access
Regulated care organizations should manage devices, browser updates, account provisioning, and access permissions centrally. Teams connecting diary-card records to internal systems should evaluate signNow API access, SSO provisioning, and certificate or long-term-validation requirements against their security and records policies before deployment.
Retention and record-keeping practices
A defensible diary-card workflow links the signed document, consent evidence, audit trail, access controls, and retention decision.
Set the retention period before collection
Export the signed card and audit history
Restrict access by care-team role
Document electronic-record consent clearly
Legal standing for electronic diary cards
An electronic Dbt Diary Card Recovery Technology Recoverytechnology record may support U.S. business evidence when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible with its audit history under ESIGN, 15 U.S.C. chapter 96, and applicable UETA law. Wills, testamentary trusts, court orders, and certain family-law filings remain excluded.

Privacy and disclosure issues to check
Personal diary entries may expose sensitive mental-health information when shared with unintended recipients. Missing consent language can weaken evidence that participants agreed to electronic records and signatures. Unrestricted access may allow unauthorized staff to view, edit, or download completed diary cards. Incomplete audit records can make it difficult to establish who signed, when, and which version was used.
Diary card completion and troubleshooting
These answers address document setup, signer access, electronic consent, plan limits, and privacy controls for this diary-card workflow.
Upload the original Dbt Diary Card Recovery Technology Recoverytechnology as a readable PDF or supported document, then check signNow’s detected fields before sending. Business plan users can use templates for repeated cards, while manual field placement remains available when the source file has no fillable fields.
Confirm that the recipient email is correct, resend the signing invitation, or provide a signNow signing link when appropriate. Business Premium includes quick invite links, while the sender should still verify the participant’s identity before accepting sensitive diary-card information.
Use signNow authentication controls appropriate to the information collected. Enterprise adds advanced signer authentication, while HIPAA-covered workflows require a business associate agreement and safeguards for protected health information under HIPAA.
The Business plan includes legally binding eSignatures, audit trails, templates, and mobile apps at $8 per user per month when billed annually. Subscription plans include 100 signature invites per user per year, with overage fees; confirm plan limits before high-volume use.
Electronic records may require consumer disclosure and access procedures under 15 U.S.C. §7001(c), including paper-record rights and withdrawal procedures. Configure the disclosure before signing and retain evidence that the signer could access the electronic diary card.
signNow is HIPAA compliant when a business associate agreement is required and in place. Compliance does not decide whether a particular diary-card record may be collected; the provider must still follow applicable privacy, authorization, retention, and state-law requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.