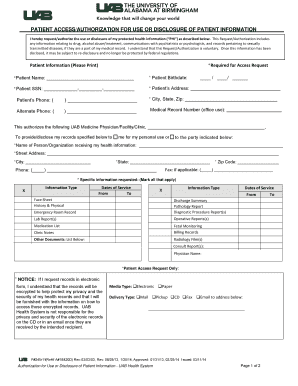
Patient Access authorization for use or disclosure of patient information
Use a PATIENT ACCESSAUTHORIZATION FOR USE OR DISCLOSURE OF PATIENT INFORMATION 2018 template to make your document workflow more streamlined.
What this patient authorization does
A Patient Access authorization for use or disclosure of patient information records a patient’s permission to release specified health information to a named recipient for a stated purpose. The form should identify the patient, information or records covered, recipient, purpose, expiration or event, and signature. The healthcare organization reviews whether the authorization is complete before disclosing information. With signNow, a sender uploads the form, places or detects fillable fields, routes it to the patient or representative, captures the electronic signature, and stores the completed document with its audit trail. HIPAA-covered records generally require six-year documentation retention under 45 CFR §164.530(j), subject to longer state rules or holds.
Who uses this patient authorization
Healthcare providers
Healthcare providers use the authorization for patient-directed releases, attorney requests, insurer communications, and family disclosures. Each request should identify the records, recipient, purpose, expiration, and signer before staff release protected information.
Patients and representatives
Patients and authorized representatives review the disclosure scope and sign when they permit a named recipient to receive specified information. Staff retain the completed authorization and evidence under HIPAA, state law, and organizational policy.
Features for patient authorization workflows
The workflow keeps patient consent, disclosure scope, signer evidence, and protected records connected from preparation through archival.
Complete scope
Capture the patient’s identity, requested information, recipient, purpose, and expiration in one structured authorization, reducing omissions before disclosure review.
Collect consent
Send the authorization to the patient or representative for electronic signing, with a clear record of consent and signing activity.
Verify signers
Use SMS OTP or other available authentication controls when the organization requires stronger evidence linking the signer to the authorization.
Protect records
Retain the signed authorization and completion history in a protected record set, supporting HIPAA documentation obligations when applicable.
Preserve evidence
Export the completed document and audit trail together so compliance staff can review the authorization, timestamps, and signer events.
Standardize workflows
Reuse an approved authorization template while keeping required patient-specific fields editable for each disclosure request.
How to complete this authorization
Prepare the patient-specific disclosure details, route the form for consent, and preserve evidence after signing.
Upload form: Upload the Patient Access authorization PDF to signNow. Check fields: Auto-detect fields, then verify patient and disclosure fields. Send for signing: Send the authorization to the patient or representative. Archive record: Store the signed authorization with its audit trail.
Security controls for patient information
HIPAA safeguards:
Transport encryption:
Stored encryption:
Control reporting:
Security certification:
Privacy frameworks:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Configure identity checks, evidence capture, and protected storage around the patient’s authorization and disclosure scope.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with consent |
| Audit trail | Export completion certificate and history |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |



Find and fill out the correct patient accessauthorization for use or disclosure of patient information
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| UAB Health System Authorization for Use or Disclosure of Information 2018 | 4.8 Satisfied (4069 Votes) | |
| UAB Health System Authorization for Use or Disclosure of Information 2014 | 4.8 Satisfied (7171 Votes) | |
| UAB Health System Authorization for Use or Disclosure of Information 2008 | 4.7 Satisfied (315 Votes) |
Patient Access authorization recordkeeping practices
Accurate retention and audit controls preserve the authorization’s scope, evidence, and disclosure history throughout its permitted use.
Apply the HIPAA six-year retention rule
Export the audit trail with every authorization
Archive patient authorizations securely
Track scope, expiration, and revocation status
Patient authorization retention schedule
Retention depends on HIPAA applicability, state healthcare rules, and active legal holds; apply the longest documented obligation.
6 years: HIPAA authorization records
Not specified: unrelated tax records
State period: healthcare records
Hold period: disputed disclosures
Authorization lifecycle: revocation records
Legal standing of patient authorizations
A completed electronic authorization can provide evidence of the patient’s intent, consent, signer attribution, and record integrity when executed under applicable requirements. ESIGN and UETA generally recognize electronic signatures, but wills, court orders, and family-law decrees remain excluded; state healthcare rules may impose additional requirements.

Privacy pitfalls in patient disclosures
Listing a recipient without a specific purpose can make the authorization too broad for the intended disclosure and difficult to validate during review. Sending the completed authorization through unapproved email or storage can expose protected health information outside the organization’s access controls. Failing to document electronic consent or signer authentication weakens evidence that the patient intended to authorize the named disclosure. Continuing disclosure after expiration or revocation can conflict with the authorization’s scope and create a preventable privacy incident.
Platform requirements for patient authorizations
The Patient Access authorization can be prepared and signed through supported web browsers on Windows or macOS, with mobile access through signNow apps for iOS and Android. Use an encrypted connection with TLS 1.2 or TLS 1.3 when handling patient information.
Browsers Chrome, Firefox, Safari, Edge Desktop operating systems Windows and macOS desktops Mobile platforms iOS and Android mobile apps
Healthcare organizations should use managed devices, restrict downloads to authorized users, and configure role-based access before sending this authorization. Enterprise deployments can connect signNow through API integrations and SSO provisioning; HIPAA workflows require a business associate agreement and organization-specific safeguards.
Healthcare authorization workflow examples
Healthcare teams can adapt a controlled authorization workflow to recurring patient disclosures without treating every disclosure as identical.
Fertility healthcare
Fertility Centers of Illinois can use a protected electronic workflow for patient-facing authorizations that require clear consent, signer evidence, and controlled handling of health information.
- Patient-facing healthcare authorization
- HIPAA workflow requires a BAA
The organization’s signNow use case is grounded in healthcare operations and API-enabled workflows. A patient authorization template can route the required fields, collect an electronic signature, preserve the completion history, and support controlled storage. HIPAA compliance remains an organizational responsibility and requires a business associate agreement where applicable.
Outpatient clinic
A regional outpatient clinic needs recurring authorizations for records released to attorneys, insurers, or family representatives, each with different scope and expiration terms.
- Different recipients and purposes
- Revocation must remain traceable
An approved signNow template can standardize the patient, information, recipient, purpose, and expiration fields while leaving case-specific values editable. The clinic should authenticate signers appropriately, export the audit trail, restrict access to authorized staff, and retain the record under HIPAA and applicable state requirements.
Patient authorization troubleshooting
Resolve authorization errors by checking the disclosure scope, signer evidence, HIPAA obligations, and retained audit record before release.
What does HIPAA require for this authorization’s retention?
When HIPAA applies, 45 CFR §164.530(j) requires documentation retention for six years from creation or the last effective date. Confirm whether state law, facility policy, a complaint, or a litigation hold requires a longer period before deleting the signed authorization or audit trail.
Does signNow provide a HIPAA-compliant workflow for patient information?
signNow identifies HIPAA compliance, but a covered entity or business associate must establish the required safeguards and execute a business associate agreement where applicable. Configure access controls, authentication, encryption, retention, and approved storage for this specific authorization workflow.
How can staff prove who signed the authorization?
Use signer authentication appropriate to the disclosure risk, such as an email invitation with SMS OTP when configured. Preserve the completion certificate and audit trail containing timestamps, signer activity, and document history; these records support attribution but do not replace required identity procedures.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.