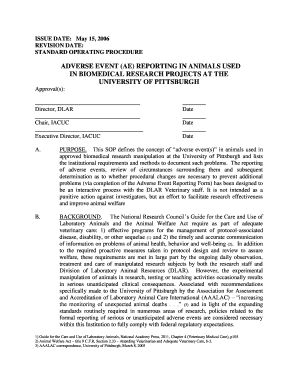
Dlar Adverse Event Reporting Sop And Form
Use a DLAR Adverse Event Reporting SOP And Form 2016 template to make your document workflow more streamlined.
What this adverse event form records
Dlar Adverse Event Reporting Sop And Form is a structured record for documenting and routing information about an adverse event. Because the supplied form name does not identify an issuing agency, reporting deadline, required fields, or governing program, the responsible organization must confirm those details in its approved SOP before use. signNow can hold the source document, identify fillable fields, send it to assigned reviewers or signers, capture completion activity, and retain the completed record with an audit trail. ESIGN and UETA may support electronic signatures when their requirements apply.
Features that support controlled reporting
A controlled signNow workflow can make adverse event reports easier to complete, review, route, and retrieve without changing the approved reporting procedure.
Reusable template
Upload the approved adverse-event SOP or form once, then reuse its configured fields instead of rebuilding the document for every report.
Role-based fields
Assign reporting, review, and approval fields to named participants so each person sees the information they are responsible for completing.
Flexible delivery
Send completed reports through email invitations or shareable links while preserving the document structure established by your reporting procedure.
Audit evidence
Capture signer identity, timestamps, actions, and completion history in an audit trail that supports internal review and record reconstruction.
Organized records
Store completed adverse event records and their signing evidence together, helping teams retrieve the correct report during quality review.
Connected workflow
Use signNow integrations such as Salesforce, NetSuite, Google Drive, Box, or API workflows when the reporting process requires connected systems.
Teams that manage reporting workflows
A safety or quality administrator can maintain the approved adverse event template, control access, assign roles, and monitor completion through signNow’s workspace controls. Shared templates reduce field drift while delegated sending lets authorized staff issue reports without editing the master document. Clinical operations or compliance teams can route a completed report to designated reviewers and retain the signed record. Business and higher plans include unlimited users at no extra cost, while administrators can separate template ownership, sending permissions, and review responsibilities.
Platform requirements for reporting teams
Complete Dlar Adverse Event Reporting Sop And Form through signNow in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing authorized users to review or sign assigned documents away from a desktop.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android mobile apps
Regulated teams should use managed Windows, macOS, iOS, or Android devices, current browser security controls, and organization-approved identity policies. API access, SSO provisioning, certificate settings, and retention configuration depend on the selected signNow plan and the reporting organization’s security requirements.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Recommended reporting workflow setup
Configure the document around the approved adverse event procedure, assigned roles, authentication requirements, and retention rule before sending the first report.
| Setting | Recommendation |
|---|---|
| Authentication method | Email authentication with SMS OTP for sensitive reports |
| Signature type | Electronic signature with recorded signer intent |
| Audit trail | Retain completion history with signer actions and timestamps |
| Document retention | Follow the approved SOP and applicable record rule |
| Encryption | Use TLS in transit and AES-256 at rest |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the reporting workflow works
The practical signNow flow begins with the approved document and ends with a completed report supported by an audit trail.
Upload: Upload the approved source form Configure: Review detected fields and assignments Route: Send to authorized reporters or reviewers Finalize: Complete, sign, and retain evidence
Ways to send and complete the report
- Use the signNow web app when a reporting coordinator needs to upload the approved form, place fields, verify recipients, and initiate a controlled reporting transaction.
- Use the signNow mobile app when an authorized reviewer or reporter must inspect assigned fields, complete the report, or sign from an iOS or Android device.
- Use kiosk mode for supervised, on-site completion where multiple reporters use a designated device and the organization controls the signing environment.
- Use a shareable signing link when an approved public or internal intake process needs a repeatable entry point without creating each invitation manually.
Find and fill out the correct dlar adverse event reporting sop and form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2016 Pitt IACUC DLAR Adverse Event Reporting SOP and Form [2016-12-21] 2016 | 4.8 Satisfied (2760 Votes) |
What the audit trail records
The audit trail documents the report’s signing events separately from the team’s initial template and account setup.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper sealing:
Action history:
Audit export:



Security controls for signed reports
Transport encryption:
Stored-data encryption:
Security reporting:
Security certification:
Health-data controls:
U.S. eSignatures:
Privacy pitfalls in adverse event reporting
Including patient names, contact details, or clinical information in unrestricted fields can expose personal data beyond the authorized reporting group. A report may lack documented consent or signer intent when users sign without reviewing the electronic-record disclosure required for consumer-facing transactions. Overbroad workspace permissions can allow staff to open adverse event reports unrelated to their assigned review or reporting responsibilities. Sending a report to the wrong recipient or link holder can disclose safety information and undermine the organization’s access-control policy.
Best practices for controlled reports
Use the approved procedure as the source of truth, then apply signNow controls consistently around fields, recipients, evidence, access, and retention.
Validate fields against the approved SOP
Separate reporting and review responsibilities
Archive the report with evidence
Review access before every send
Processing stages for each report
The form’s source materials do not establish a universal filing deadline, so timing must follow the responsible organization’s approved adverse event procedure.
Document preparation
Delivery to signers
Signer turnaround
Completion and archival
Risks of improper reporting
Missing event facts
Unauthorized disclosure
Weak signature evidence
Reduced record support
Troubleshooting the reporting workflow
These answers address field detection, routing, plan selection, privacy, signature validity, and electronic-record consent for this reporting workflow.
Upload the approved PDF or source document again, then use signNow’s field-detection workflow to identify fillable areas. Review every detected field manually because the platform cannot determine whether a field is required by your adverse event SOP.
Open the recipient settings and verify each email address, signing order, and assigned field. If the report contains protected health information, confirm the organization’s HIPAA workflow and BAA requirements before sending it externally.
Business is listed at $8 per user per month with annual billing and includes templates and audit trails. Business Premium is $15 annually billed and adds bulk send, kiosk mode, and quick invite links.
signNow states that HIPAA compliance requires a BAA. Confirm that the organization has the required arrangement and configure access, authentication, retention, and disclosure practices for the actual information in the report.
Electronic signatures can satisfy ESIGN and UETA requirements when intent, consent, attribution, and record retention are established. A reporting team must still verify whether its specific agency, protocol, or state rule requires another signing method.
If the form contains consumer-facing electronic records, the ESIGN consumer-disclosure rule requires clear paper-record rights, electronic-access capability, and a withdrawal process under 15 U.S.C. §7001(c). Obtain legal or compliance review before applying that workflow.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.