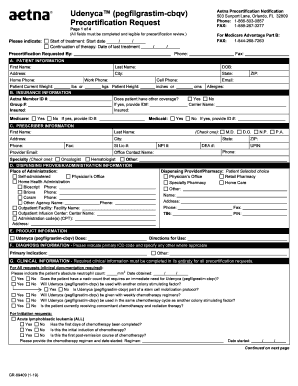
Udenyca Cbqv Precertification Request Udenyca Cbqv Precertification Request
Use a Udenyca cbqv Precertification Request Udenyca cbqv Precertification Request 2019 template to make your document workflow more streamlined.
About this precertification request
The Udenyca Cbqv Precertification Request is a healthcare administrative document used to request review before a service or treatment is provided. Its exact payer, provider, patient, clinical, and authorization fields depend on the issuing workflow, so the source version should remain authoritative. With signNow, a sender uploads the request, reviews detected fillable fields, assigns signer roles, and sends it electronically. The signer reviews and signs, while signNow records timestamps, actions, and completion evidence. Confirm payer acceptance, HIPAA obligations, and submission instructions before relying on the completed record.
How this request works in signNow
The signNow workflow moves this request from source document to signed, auditable record.
Upload: Upload the request PDF. Prepare: Review detected fields and add missing signer fields. Route: Send the request to the authorized signer. Archive: Store the signed request with its audit trail.
Complete the request in signNow
Follow the source request carefully, then use signNow to prepare, route, sign, and retain the completed document.
Upload:
Upload the request PDF. Review:
Check patient and payer fields. Assign:
Assign authorized signers. Send:
Send and monitor completion.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for this request workflow
signNow organizes the Udenyca Cbqv Precertification Request workflow from upload through signature, audit evidence, and record storage.
Field preparation
Upload the source request and inspect detected fields before adding signer, date, or required-response fields.
Signer routing
Assign the authorized healthcare or administrative signer and route the request through a controlled signing order.
Audit trail
Capture intent, signer actions, timestamps, and completion details in an electronic audit trail.
Reusable template
Use templates when the same Udenyca Cbqv Precertification Request workflow repeats with consistent fields and roles.
Mobile signing
Complete the request from signNow mobile apps when authorized staff work away from a desktop.
Record storage
Preserve the signed request and completion evidence for the organization’s applicable records policy.
Recommended setup for this request
Configure the request around signer identity, document history, secure storage, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn e-signature |
| Audit trail | Capture IP, timestamps, and actions |
| Document retention | Retain signed records under applicable policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
Find and fill out the correct udenyca cbqv precertification request udenyca cbqv precertification request
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2019 Aetna GR-69409 [2019-01] 2019 | 4.8 Satisfied (6075 Votes) |
Signer authentication and certificates
PKI support:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signing evidence:
Privacy pitfalls in this request
Patient identifiers can appear in uploaded pages, completed fields, notifications, and downloaded copies; limit access and avoid unnecessary disclosure. A missing electronic-consent record can weaken evidence that the signer agreed to complete this request electronically. Incorrect payer, provider, or patient fields can route the precertification request to the wrong party or require rework. Shared accounts can weaken signer attribution; assign individual users and review permissions before sending requests.



Troubleshooting this request workflow
Resolve field, signer, compliance, plan, and retention questions before sending the completed request.
Upload the original request as a clear PDF, then use signNow’s field detection and review every detected field before sending. Correct any misplaced patient, provider, payer, or signature fields manually so the completed request reflects the source document.
Use signNow’s signer authentication options, including SMS OTP where configured, and verify the recipient’s phone number. Authentication supports attribution, but the organization must still confirm the signer is authorized for this precertification request.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps. Business Premium adds bulk send, while Enterprise adds advanced signer authentication. Select the plan based on request volume and required controls.
For healthcare records containing protected health information, signNow states that HIPAA compliance requires a business associate agreement. Confirm the organization’s BAA and internal access, disclosure, and retention policies before routing the request.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention requirements are met. Confirm payer or provider rules separately because legal recognition does not guarantee electronic submission acceptance.
After completion, download the signed document and certificate of completion, then retain them under the organization’s applicable healthcare, payer, and records policy. The audit trail preserves signing actions, timestamps, and related event information.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.